Search results for tag #infosec

RE: https://eupolicy.social/@hpod16/117286020053320946
It’s interesting that people who support age verification have to ask what the problem is. As if it was a big mystery.
Asking people to reveal their personally identification so they can use the internet isn’t a problem that should need to be explained. But since you asked…
1. Our data can not be protected online. Especially by every random person who has the means to buy a domain and pay for hosting.
2. Forcing identification is a barrier for many people. That’s exclusion. And in many cases ableism.
3. Age verification won’t keep kids from using technology. If their parents are that disconnected, they’ll help them through the gates and move on. Restricting access creates a hurdle, not an impasse.
4. Age verification puts the onus on people using the web instead of the people make parts of it horrible. We are victims of nefarious systems. We are not the problem. The systems are. That should be the focus of solutions.
#EUKidsAct #Privacy #Internet #InfoSec #IfYouHaveToAsk
I get that the #EUKidsAct is getting a lot of negative chatter from the privacy advocates.
But at the same time to you have to acknowledge there is a serious problem here. I go out in public, I see parents park their kids in front of a tablet to keep them calm, with next to no supervision.
Teenagers are spending on AVERAGE 4-6 hours online per day, instead of going outside and interacting with humans.So let me ask you, genuinely. What are the concerns here? What needs to be addressed?

This dumb password rule is from Easybank (Austrian direct bank).
- At least 8 and at most 16 (!) characters
- **Must start with 5 digits (do we really want to know what's going on there?)**
- At least one uppercase and one lowercase letter
- (Some) special characters are permitted, most are not
- "Simple" patterns are prohibited
- PINs are case sensitive (at l...
https://dumbpasswordrules.com/sites/easybank-austrian-direct-bank/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Canada Revenue Agency.
Password checklist:
- 8 to 16 characters
- At least 1 upper-case character
- At least 1 lower-case character
- At least 1 digit
- No space
- No accented characters
- No special characters except: dot (.), dash (-), underscore (_), and apostrophe (')
- No more than 4 consecutive identical characters
https://dumbpasswordrules.com/sites/canada-revenue-agency/
#password #passwords #infosec #cybersecurity #dumbpasswordrules

Salesforce have somehow managed to implement a security control that lowers overall security, and pisses everyone off in the process - a rare achievement.
Our setup is quite simple: my users SSO into our IDP, they have to use a strong authenticator (FIDO2, Biometric, App OTP etc.) - Then they login to Salesforce via SAML
IDP sends a message in the SAML assertion to Salesforce that confirms they have used strong, phishing resistant auth.
What used to happen was: Salesforce would be more than happy with the assertion that strong MFA had been used - and would let the people do what they needed to do.
Now, however, they've decided that people who login via IDP's can no longer be trusted, so, when you do certain things like access a report from Salesforce, you must do MFA again with a "Salesforce-Native authenticator".
According to them:
"Step-up authentication must be completed using a Salesforce-native verifier, it cannot be delegated to an external SSO identity provider (IdP). Even if a user authenticates into Salesforce via SSO, they are still required to satisfy the step-up challenge using one of the following:
A Salesforce-registered MFA method (such as Salesforce Authenticator, a TOTP authenticator app, a security key, or a built-in authenticator like Face ID or Touch ID)
A one-time passcode (OTP) delivered via email or SMS to the contact information associated with their account
This means SSO users who do not have a Salesforce-native verifier registered will fall back to email or SMS OTP to complete the step-up challenge."
Read that last part. None of my users have Salesforce-native verifiers, because they are all associated with our IDP, where they have strong auth - so, the secure code they get is A) SMS or B) over Email - because its more secure and trustworthy than FIDO2, apparently.
Truly incredible.
https://help.salesforce.com/s/articleView?id=005321566&type=1
This dumb password rule is from Chegg.
Here are the (only fairly poor) rules for a new password. Enter 64 character password that matches all the rules (notice no rules on maximum length). That password you entered looks good! But we didn't change it. And your old password doesn't work. Or the new one. ¯\\\_(ツ)\_/¯
https://dumbpasswordrules.com/sites/chegg/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from SAS Eurobonus.
The best thing about rules, is that you can multiple different ones!
Like SAS that allows you to have a long password at least when signing
up, but you'll be sorry if you want to change your password later on.
https://dumbpasswordrules.com/sites/sas-eurobonus/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Return of Reckoning.
Password must be between 6 and 100 characters.
It doesn't say on the website, but the password only works in the related game client if it is purely alphanumeric. Not even special characters like % or $ are allowed.
https://dumbpasswordrules.com/sites/return-of-reckoning/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from El Corte Ingles.
Min 6 and max 8 characters for password! Can't contain anything
different than letters and numbers. Apart, the email address must have
at least 8 characters (sorry million dollar domain owners! :D)
https://dumbpasswordrules.com/sites/el-corte-ingles/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Southwest.
Password must be between 8 and 16 characters in length and include at least one uppercase letter
and one number. Certain special characters are also allowed, but the first character of the password must be alphanumeric.
https://dumbpasswordrules.com/sites/southwest/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from SunTrust.
At least there are a variety of special characters to choose from.
https://dumbpasswordrules.com/sites/suntrust/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Coppell, TX - Water Utility.
Local Utility with a password restriction of 30 characters. Better than some for sure, but still dumb.
https://dumbpasswordrules.com/sites/coppell-tx-water-utility/
#password #passwords #infosec #cybersecurity #dumbpasswordrules

Socket: Malicious Twitch Browser Extension Exposes 30,000 Users’ OAuth Tokens to Russian Bot Service https://socket.dev/blog/malicious-twitch-browser-extension @SocketSecurity #infosec #Twitch #bot
The "Vaults" folder encryption app (https://flathub.org/apps/io.github.mpobaschnig.Vaults) is a very cool concept, I think it would benefit from being more widely discovered (keywords may help: https://github.com/mpobaschnig/vaults/issues/195)
I wonder what I could use it for, in a future where GNOME OS will provide per-user home directory encryption out of the box with #systemd, and Pika Backups already has encryption.
Anyone using Vaults (or similar) for something interesting?
#encryption #gocryptfs #CryFS #infosec #security #Linux #GNOMEOS


Revolut Discloses Sensitive Customer Data Following Fraudulent Government Requests
Revolut confirmed a data breach on September 12, 2026, after disclosing sensitive customer information to an unauthorized third party posing as a government agency. The attackers used a legitimate government email domain to send fraudulent data requests that bypassed the company's verification checks.
****
#cybersecurity #infosec #incident #databreach
https://beyondmachines.net/event_details/revolut-discloses-sensitive-customer-data-following-fraudulent-government-requests-l-t-k-6-q/gD2P6Ple2L
This dumb password rule is from Telcel.
- The username is the cell phone number (easy to get)
- The company creates a password between 8 and 12 characters for you
- Password must contain at least 1 capital letter and no special characters
https://dumbpasswordrules.com/sites/telcel/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from myezyaccess.com patient portal system.
12-character maximum password length. This is not a single website but a patient portal system used by hundreds of medical facilities via subdomains, with password policy apparently being consistent for all sites.
https://dumbpasswordrules.com/sites/myezyaccess-com-patient-portal-system/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Slovenska sporitelna.
Slovenska sporitelna is the biggest bank in Slovakia. Despite pretty new version of the internet banking (rolled out in 2018), their password policy restricts password to be 16 characters long at most and prohibits any special characters.
https://dumbpasswordrules.com/sites/slovenska-sporitelna/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Mobility.
The username is the customer number, which is sequential and cannot be changed, currently 7 digits long for new customers.
The password has to be exactly 6 digits long, only numbers allowed.
https://dumbpasswordrules.com/sites/mobility/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Chase Bank.
* Can't use any special characters except ! # $ % + / = @ ~
* Max length restriction (32 characters).
* No runs of identical characters ("aaa") or sequential characters ("abc").
* Password check is case-insensitive
https://dumbpasswordrules.com/sites/chase-bank/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
From yesterday.
Socket: Malicious Chrome and Firefox Extensions Steal Crypto Traders’ Session and Wallet Data https://socket.dev/blog/chrome-firefox-crypto-data-theft @SocketSecurity #infosec #Chrome #Firefox #fraud #threatresearch

Dad just called "to let me know" that "he got an alert from Microsoft on his computer" and "he just spoke to someone from Microsoft and they're going to run some scans or something."
I explained to him, for the ♾️ time, that it's a scam, it's always a scam, it's just a scammy website popping up fake alerts. "What am I supposed to do then?" he asks me. "Just ignore it, it's a scam," I tell him, as I've told him countless times before.
Dad has a Chromebook.
🤦
#infosec #sandwichGeneration
This dumb password rule is from SunLife.
- 8 to 10 characters
- At least 1 letter and 1 number
- No spaces, symbols, or accents
https://dumbpasswordrules.com/sites/sunlife/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from A1 Mobile Serbia.
A1 mobile Serbia is a mobile provider in Serbia that imposes poor password rules.
Translation: "Length of the password must be between 8 and 20 characters and can only have letters and digits."
https://dumbpasswordrules.com/sites/a1-mobile-serbia/
#password #passwords #infosec #cybersecurity #dumbpasswordrules

Hey, questions for folks on the more equipment side of #infosec.
#Faraday cage for phone and keyfob? Overkill or common sense? Prices are all over the place, assume cheap off brand are scams? Any recommendations for vendors if a practical idea?
It's kinda making me crazy that stores have started put RF readers in the carts and baskets, and readers everywhere are grabbing data they shouldn't just by driving around. Faraday sleeves seem like a good idea in theory, but I don't know if the theory is really practical, as all the tests I've found seem to be manufacturer funded.
As an aside, I wonder what happens if you're driving and you put a keyless fob in a faraday sleeve. Would the car turn off? I don't know if they continue to handshake the device once the car is on.
This dumb password rule is from Vélib’ Métropole.
Your password must be at least 10 characters, with at least 1 uppercase character, 1 lowercase character, 1 number and 1 special character (only from this list: @, $, €, #, %, *, ., ;, !, ?).
You're not allowed to paste passwords.
https://dumbpasswordrules.com/sites/velib-metropole/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Replit.
Forces to use minimum 8 characters in the password and it must contain at least one uppercase.
https://dumbpasswordrules.com/sites/replit/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
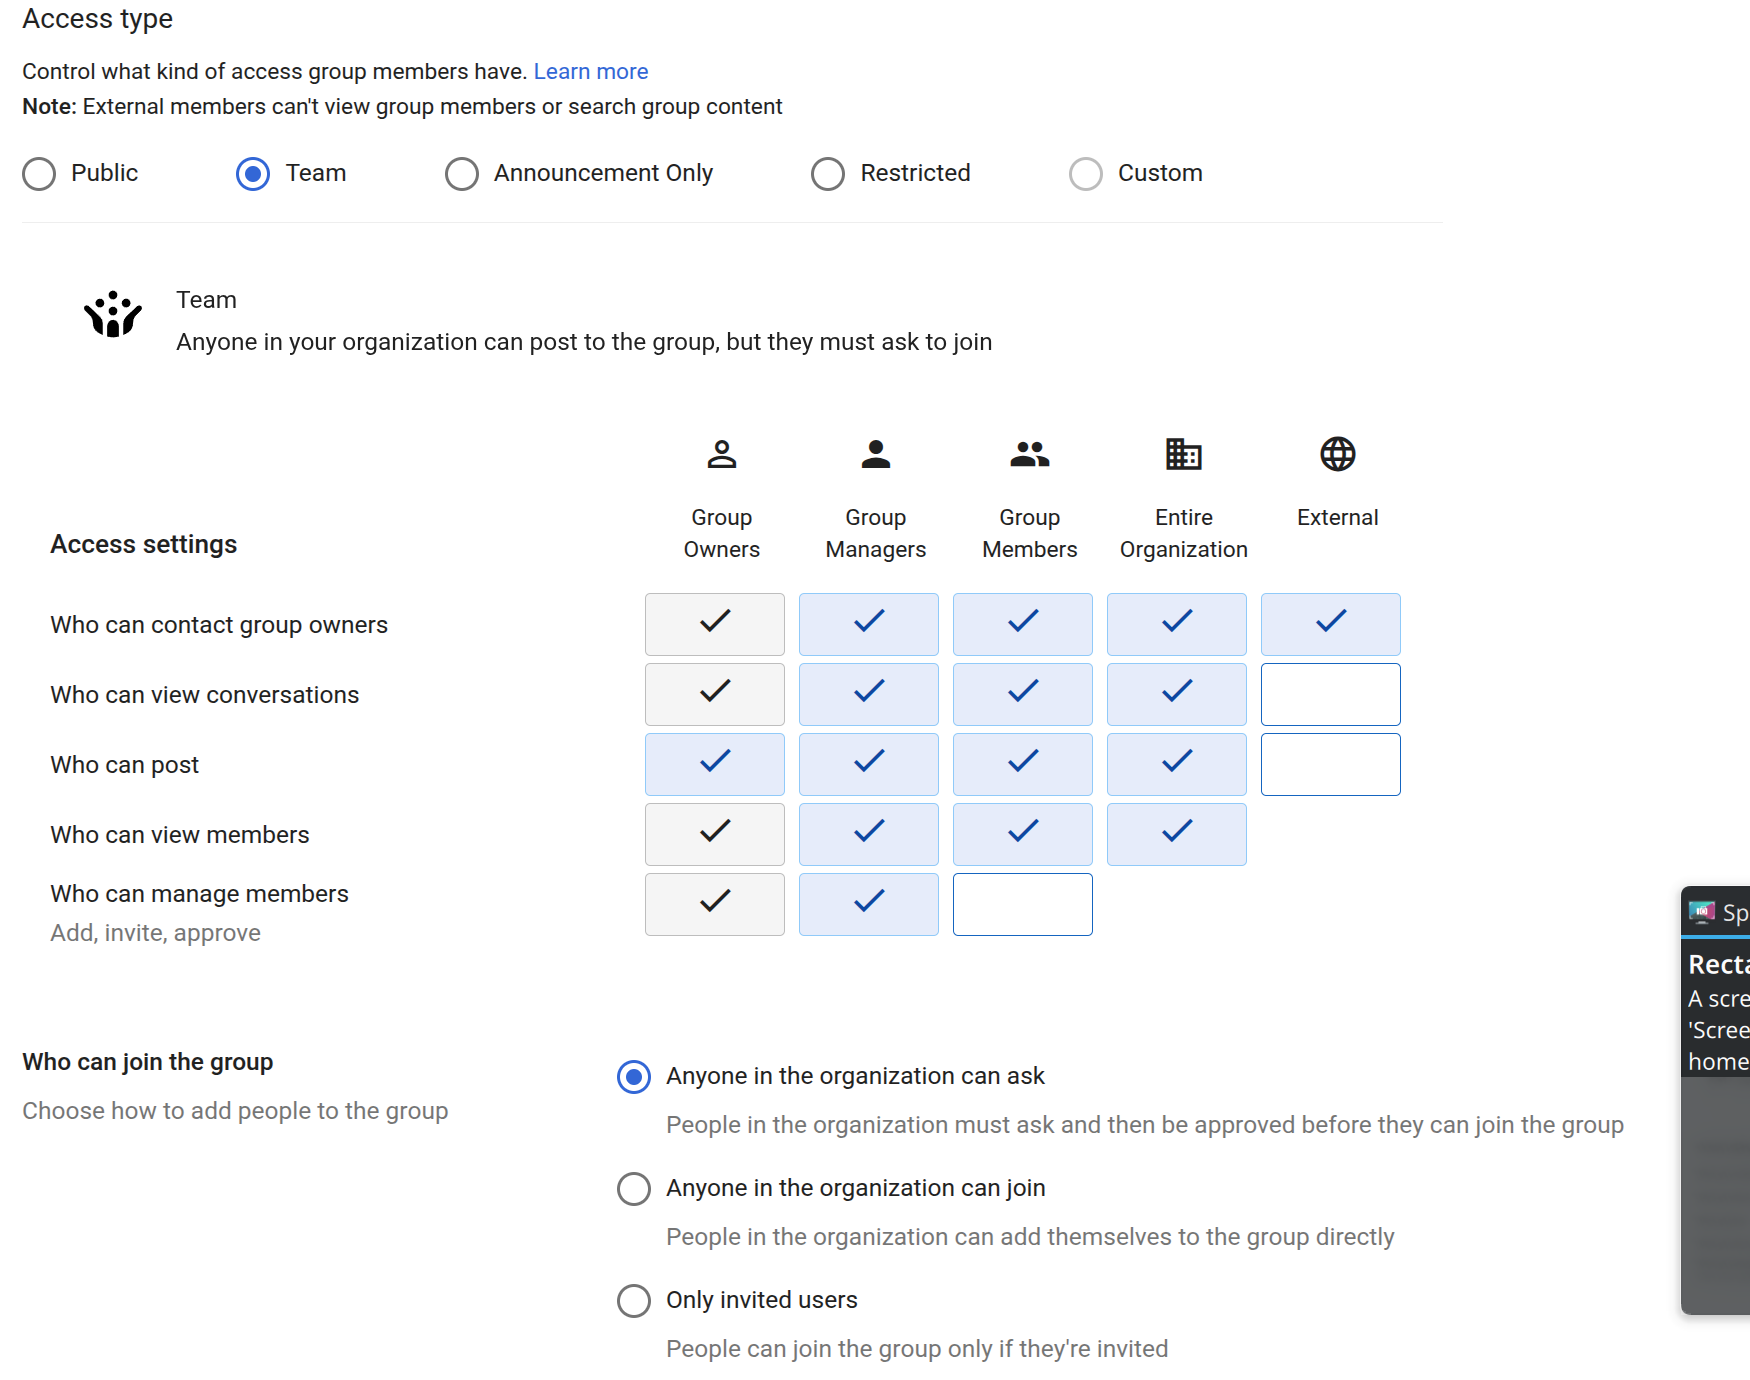
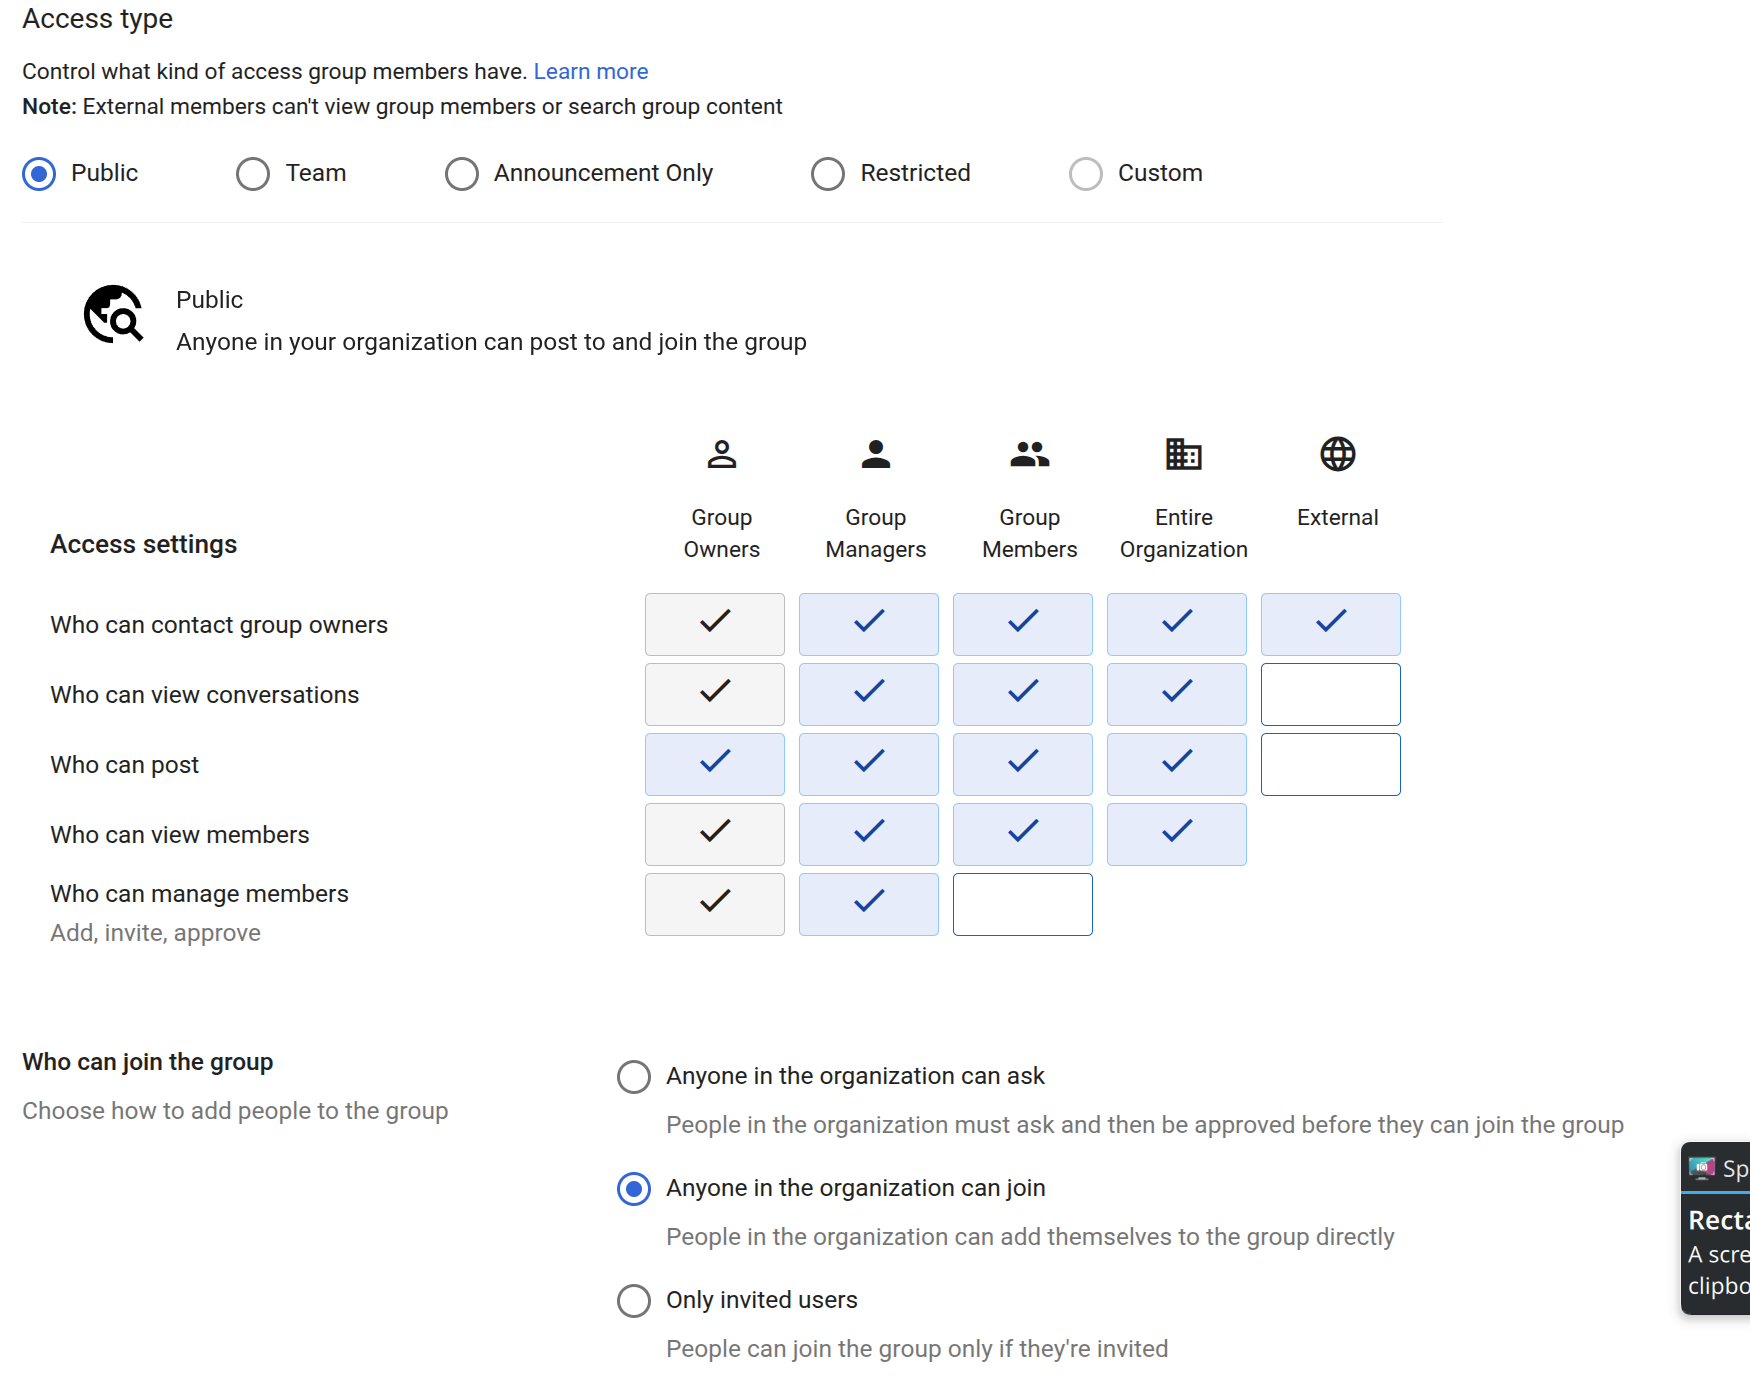
I've had admin powers at 5+ companies' Google Workspace/G Suite over the past decade or so. Every single one had groups which were misconfigured, often so anyone in the whole company could join without approval or see the message history at https://groups.google.com without being a member at all.
This is because for any sensible configuration of Google Groups when using it for email groups you have to use the "Custom" permissions mode. The default Public mode doesn't allow external people to email the group, but does allow the whole company to see all the messages. The default Team mode, has the same problem of everyone being able to see all the messages.
Also let's not forget that dangerous little "Anyone in the organisation can join" toggle at the bottom which is on by default. So any random new starter can join your confidential company directors group and get all the emails sent to it.
Giving Google the benefit of the doubt here, I think the reasoning might be that Google Groups is intended as a kind of company forum, not for private email groups. However that isn't how anyone uses it in my experience...
#security #infosec #google #googleworkspace
Alt...
Screenshot of the default Google Group settings for team mode
Alt...
Screenshot of the default Google Group settings for public mode