Search results for tag #security

#EU rejects Trump’s big beautiful security deal with Russia & all of Europe
#European leaders push back against Washington’s proposal for broader #security framework, warning that #Moscow cannot dictate continent’s future
#Trump described potential agreement as very big deal involving not only Ukraine but all of Europe
#ComradeKrasnov #untrustworthy #TraitorTrump #TrumpIsARussianAsset #DementiaDon #TrumpUntrustworthy #dictators #sovereignty #USThreats #USAggression

Headsup to all #WoodpeckerCI users,
we try to harden our core and plugins for quite some time, still it is not fully done jet.
So for time being we highly recomend to run pipelines with the gated feature!

🚀 Defguard 2.2 Hardware Key (FIDO2) MFA
🆕 What's new:
- FIDO2 hardware keys as WireGuard® MFA factor
- Multi-step MFA flows per location
- Redesigned mobile client
- MFA setup in the desktop client
- Firewall bulk actions
👉 https://defguard.net/releases/2.2.0/features/
#vpn #sysadmin #devops #selfhosted #SelfHosting #wireguard #OpenSource #release #security #privacy #homeLab #anonymity #floss #docker #CyberSecurity #InfoSec #OnlinePrivacy #DataProtection #InternetSecurity #NetworkSecurity
Alt...
Defguard 2.2 Release - Enterprise VPN on WireGuard with built-in FIDO2 hardware key MFA
OpenBSD top(1) adds flag to show chroot, pledge and unveil status https://undeadly.org/cgi?action=article;sid=20261106104957 #openbsd #top #chroot #pledge #unveil #security #development #freesoftware #libresoftware
New patch releases for Alpine Linux:
3.21.10
3.22.8
3.23.8
3.24.4
- A security fix in apk-tools 3.0.9 and 2.14.13 to prevent crashing on certain malformed data.
https://alpinelinux.org/posts/alpine-3.21.10-3.22.8-3.23.8-3.24.4-released/
When the eMudhra Intermediate CA was compromised, the #Python ecosystem had to move fast.
Within two days, fixes shipped for certifi, Python, pip, uv, sigstore, virtualenv, conda & more, with PyPI and python.org patched as well.
Read how PSF #security staffing made the difference, and what’s next:
https://pyfound.blogspot.com/2026/11/how-python-ecosystem-responded-to.html

🗝️ Any passwords over 256 characters are fine.
Ref: https://sshhole.com/
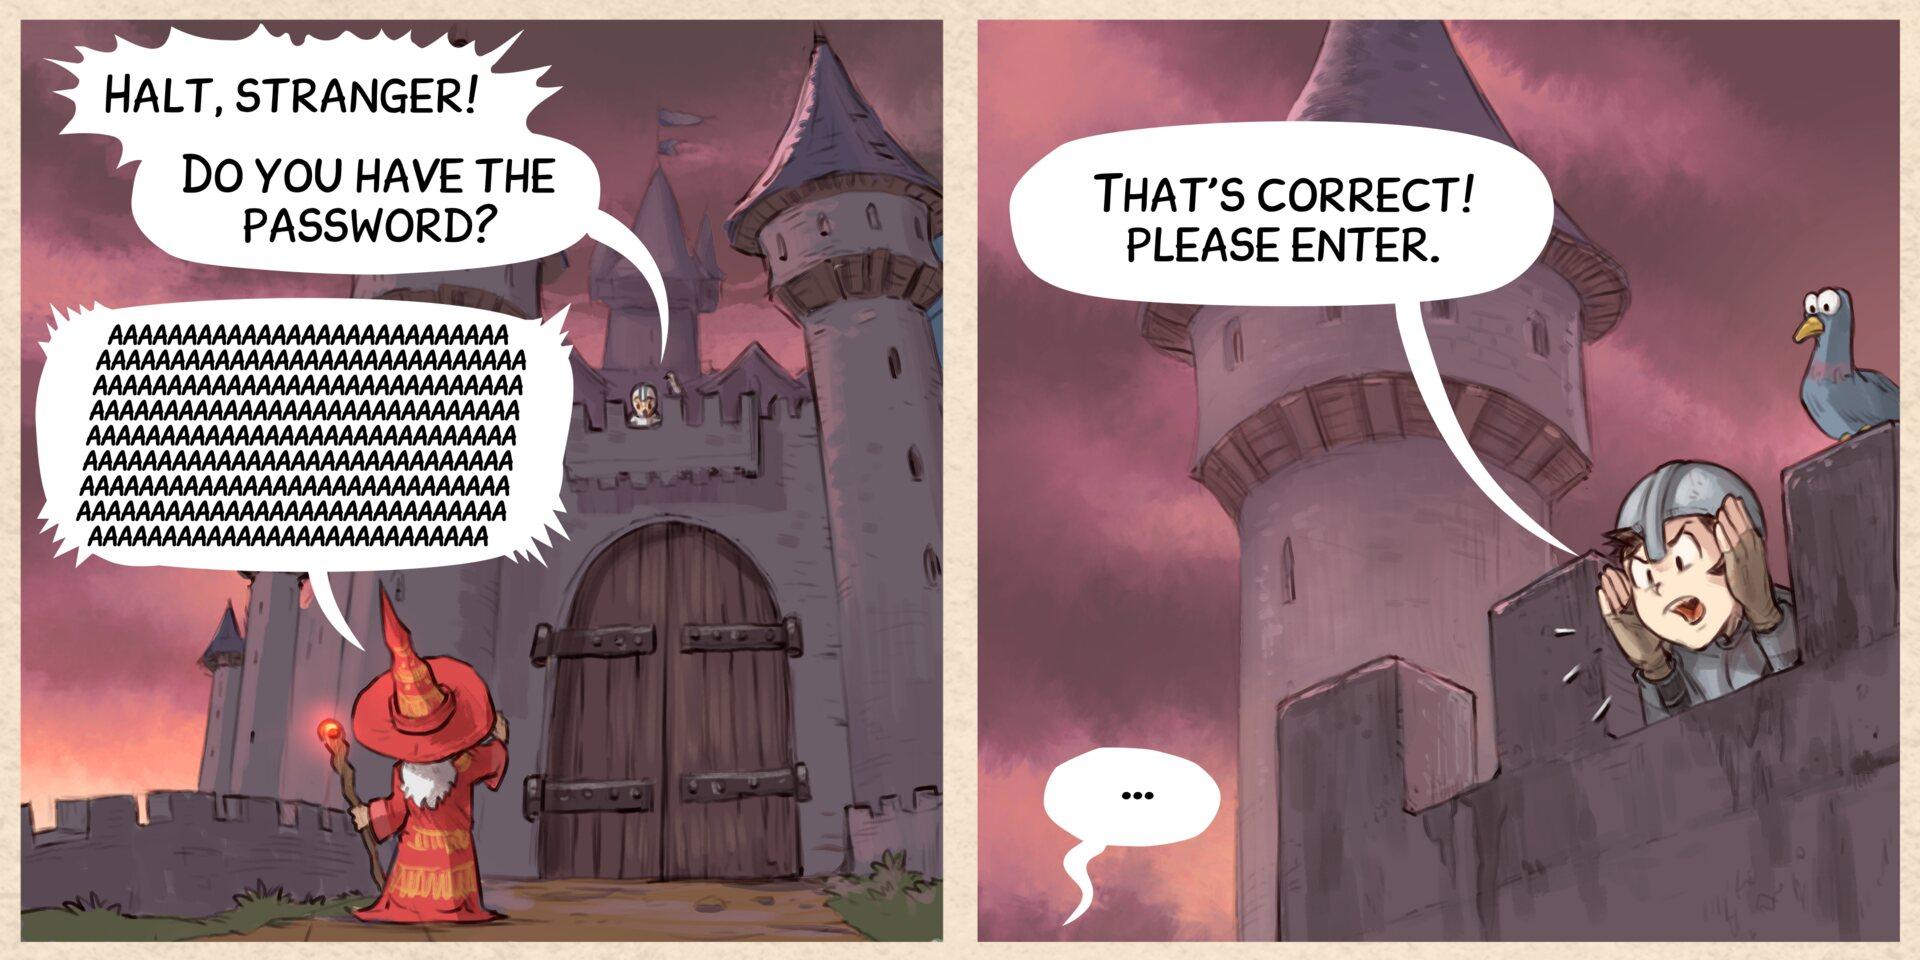
Alt...
A comic in two panels
Panel 1. A wizard walks on the bridge in front of a castle, door closed. From the top of the castle a guard shoot:
Guard: Halt! Do you have the password?!
Wizard:AAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAA
Panel 2. Shot on the guard:
Guard: "That's correct, please enter!"
Wizard: ...?
Security advisory regarding openssh-server on Alpine Linux:
https://alpinelinux.org/posts/2026-11-05-openssh-password-authentication-bypass/
Debian, Ubuntu and derivatives hit by APT flaw that could give attackers root access https://www.gamingonlinux.com/2026/11/debian-ubuntu-and-derivatives-hit-by-apt-flaw-that-could-give-attackers-root-access/
Critical security vulnerability affects OpenSSH on Alpine Linux systems
Urgent: Immediately set 'PasswordAuthentication no' in /etc/ssh/sshd_config and restart the sshd service. Make sure you have ssh key authentication or other ways to access your machines.
Also make sure to update openssh to the latest version.
The openssh fix will be backported all the way back to Alpine 3.16

The OpenPGP card stack is now complete on FreeBSD! Joining oct, openpgp-card-ssh-agent and openpgp-card-tools-git just landed in ports:
oct: manage YubiKeys, Nitrokeys & co. from the CLI
https://www.freshports.org/security/openpgp-card-tools/
openpgp-card-ssh-agent: SSH login with the key on your card, works with standard clients
https://www.freshports.org/security/openpgp-card-ssh-agent/
oct-git: hardware-backed Git signing and verification
https://www.freshports.org/security/openpgp-card-tools-git/
Private keys never leave the card. 😃
Thanks to Heiko Schaefer ( @hko ) & ( @wiktor ) for the tools and Älven for the commits!
#FreeBSD #OpenPGP #Security #PGP #RunBSD #Cryprography //cc @feld
Debian Linux apt security update: man-in-the-middle arbitrary code execution. Apply updates as soon as possible.
https://lists.debian.org/debian-security-announce/2026/msg00526.html
#Google security alert.
I just had notification on my burner phone (used for purchases etc) that Google had scraped my phone number. My phone numbers are my private data & they can fuck right off with assuming to seize it. I have deleted the number from my account but I bet they still have it squirreled away somewhere. Bastards.
#android #phonesecurity #security
Most info here https://www.androidpolice.com/google-phone-number-link-to-signed-in-accounts/
We’re excited to welcome Brett Smith as the PSF’s new Security Developer 🐍🔒 Brett joins @sethmlarson and @miketheman to help scale #security response for the #Python ecosystem.
https://pyfound.blogspot.com/2026/10/announcing-new-security-developer-2026.html


Been in the @protonprivacy ecosystem for 18 months and been pretty happy.
Now - with them pushing AI deep into their development cycle, bullying their employees and the CO increasingly sounding like an unhinged tech bros - it's time to consider alternatives.
Unless change happens fast, I'll be switching to various other EU/UK privacy providers across the board.
And Proton stop getting my money. This will absolutely not help their business.

Andy Yen should be removed as Proton's CEO.
Each time I've had beef with something related to Proton, he's been the one driving it.
www.404media.co/manifestos-fear-and-loser-thinking-inside-protons-ai-reckoning/
(sans paywall)
https://unwall.app/www.404media.co/manifestos-fear-and-loser-thinking-inside-protons-ai-reckoning/

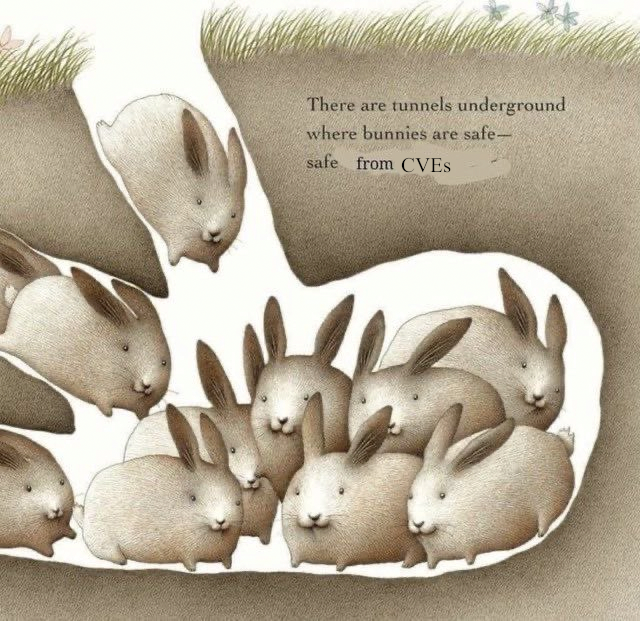
Alt...
Drawing of a bunch of rabbits inside a burrow with the text "There are tunnels underground where bunnies feel safe - safe from CVEs."
🐍🛡️🎙️ Check out PSF Security Developer in Residence @sethmlarson on the Real Python Podcast!
Hear about the latest in #Python #security: LLMs and vulnerability triage, trusted publishing on PyPI, PEP 770 SBOMs, and CI/CD tips.
We have published a report on a security incident on gitlab.alpinelinux.org. An attacker tried to exploit CVE-2026-97229. We found no evidence it succeeded but can't rule it out, so we rebuilt
GitLab from scratch.
Alpine packages and releases were not affected, and no signing keys were exposed.
All GitLab passwords have been reset. If you reused yours elsewhere, change it there.
https://alpinelinux.org/posts/GitLab-security-incident-CVE-2026-97229.html
🐍🚀 Out now: Tablib 3.10.0
The format-agnostic tabular dataset library
🔒 Security fix to escape dataset title in HTML serialisation
🦥 Support for Python 3.15 with lazy imports
💧 Drop support for EOL Python 3.9
🩹 And a bunch of fixes
https://github.com/jazzband/tablib/releases/tag/v3.10.0
#Python #Tablib #release #security #Python315
LibreSSL 4.4.0, 4.3.4, 4.2.3 released https://www.undeadly.org/cgi?action=article;sid=20261025115016 #openbsd #libressl #ssl #tls #https #crypotography #crypto #security #networking #www #developement #freesoftware #libresoftware