Search results for tag #infosec

Network security question: How are people restricting outbound connections based on DNS names?
For example: Server A wants to connect to cdn.network.com, and that can resolve to a huge range of IPs, so not feasible to allow list all possible outbound connections.
I vaguely remember some dns proxy / firewall magic where it tracks the answer and opens up the IP.

This dumb password rule is from ADP.
Forced to change the password during the first login. At least they
could use proper grammar in their rule list.
https://dumbpasswordrules.com/sites/adp/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
How are we all handling this Certificate thing? Anyone have an easy way to check the certificate issuance transparency lists? (Without downloading gigs of text files?)
TLDs for .gh .as and .sl are effected. Google says they aren't sure what certs are good or bad or which the bad guys minted...
Hackers obtain counterfeit TLS certificates for Google and other large services - Ars Technica https://share.google/98Q3e4OnkjAnuf5KX
This dumb password rule is from Microsoft (e company store).
Max of 16 character oh and please don't use any characters we don'y know how to escape properly
also if it starts with ? you may break our wonderful website. What out with your password generator
duplicated characters is far too insecure to allow here.
https://dumbpasswordrules.com/sites/microsoft-e-company-store/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Munich Foerdermittel Portal.
You register on their funding portal and receive an email with an activation link to set a password.
The email further informs you about their password policy:
- At least 8, but no more than 20 characters
- At least one lowercase and uppercase letter
- At least two digits (1,2,3,4,5,6,7,8,9,0) or...
https://dumbpasswordrules.com/sites/munich-foerdermittel-portal/
#password #passwords #infosec #cybersecurity #dumbpasswordrules

The two types of #infosec product sales experiences.
1) getting called daily for something you have no intention of buying ever.
2) finding something you really need and trying to buy it, only to be told “great, we only sell through the channel - who is your preferred reseller?”
NO ONE. SELL ME YOUR SHIT, COWARDS!
This dumb password rule is from Rushmore Loan Management Services.
Hmmm.. why are they afraid of double and single quotes in my passwords?
https://dumbpasswordrules.com/sites/rushmore-loan-management-services/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
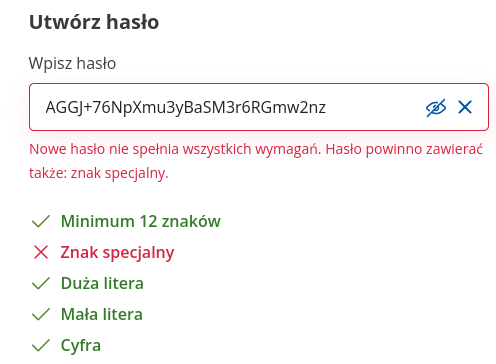
Profil taki Zaufany, profesjonalnie mocno, bardzo bezpieczeństwo, wow uszanowanko.
Alt...
Zrzut ekranu z interfejsu tworzenia hasła dla Profilu Zaufanego.
Hasło zawiera znak "+". Interfejs ostrzega, że:
"Nowe hasło nie spełnia wszystkich wymagań. Hasło powinno zawierać także: znak specjalny."
This dumb password rule is from MTS Serbia.
MTS is a national mobile and internet provider in Serbia and they have bad password rules.
Translation: The password must have more than 6 character, less than 17 characters and one
of the following combinations: upper case or lower case letter and a number, upper case or
lower case letter and a ...
https://dumbpasswordrules.com/sites/mts-serbia/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from MetLife.
Max length of 20 characters, no special characters allowed.
Pasting into the second password field is disabled even with
the Chrome extension Don't Fuck With Paste.
https://dumbpasswordrules.com/sites/metlife/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from PCPartPicker.
There are no rules for passwords. Passwords can be any length (including one character)
of any complexity. No password change confirmation emails are sent.
https://dumbpasswordrules.com/sites/pcpartpicker/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Sears.
"cAsE sensitive, no spaces, ! or ?
8 characters min - 1 letter, 1 number
Can't repeat same character more than 3 times in a row
Cannot be or contain your username or email address"
https://dumbpasswordrules.com/sites/sears/
#password #passwords #infosec #cybersecurity #dumbpasswordrules


 [
The FBI's NSPM-7 Joint Mission Center was built to implement a presidential memo that cites anti-Americanism, anti-capitalism, anti-Christianity and extremism on migration, race and gender as common threads in domestic terrorism. FOIA records reported by Talking Points Memo show 13 IRS employees (10 Criminal Investigation agents and three analysts) and two attorneys from the DOJ Office of the Deputy Attorney General detailed to the center, while the FBI's FY2027 budget request says it draws on 10 agencies to integrate intelligence and financial analysis. The IRS holds broad authority over nonprofit status, and TPM reports that DHS agents in Minneapolis cited NSPM-7 while using undercover agents and financial investigations to surveil unions, churches and other protest groups. The records are heavily redacted and DOJ declined to comment, leaving the center's scope and targets unclear.
https://talkingpointsmemo.com/news/fbi-nspm-7-joint-mission-center
#infosec #privacy #Surveillance #DigitalRights #CivilLiberties #NSPM7
This dumb password rule is from amaysim.
Passwords must be 6-15 characters. If you enter more than 15 characters at signup, there is no error,
but the system apparently silently truncates to 15 characters. So of course, logging in subsequently
fails if you enter the untruncated password. How convenient.
https://dumbpasswordrules.com/sites/amaysim/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This is a typical AI article that again mentions "rogue agents" which is really a public relations blame dodge - trying to move the blame elsewhere. And the truth? Inadequate guardrails for sure, but poor prompting and the training process itself is to blame. That puts blame squarely on the AI company itself. Rogue is when a human acts out against the rules on purpose, these agents were simply following orders as they understood them.
https://thehackernews.com/2026/10/openai-parts-ways-with-three-safety.html

New.
Socket: Pretty Themes, Hidden Loaders: GlassWorm-Linked Extensions Span VS Code Marketplace and Open VSX https://socket.dev/blog/glassworm-vscode-themes @SocketSecurity #infosec #threatresearch #JavaScript #Git
This dumb password rule is from myezyaccess.com patient portal system.
12-character maximum password length. This is not a single website but a patient portal system used by hundreds of medical facilities via subdomains, with password policy apparently being consistent for all sites.
https://dumbpasswordrules.com/sites/myezyaccess-com-patient-portal-system/
#password #passwords #infosec #cybersecurity #dumbpasswordrules


🤬 … oh Microsoft 🤦🏻♂️
Somewhere right now, a nonprofit staffer is clicking around Microsoft 365 looking for a critical file. It's gone. And Microsoft just confirmed it isn't coming back. 😳
Not "we'll look into it"... Not "give us 48 hours"... Gone. 🤬
I've seen this movie before. People assume the cloud is the backup. It isn't. The cloud is where your data lives, which means it's also where your data can vanish. One wrong click, one bad sync, one retention policy nobody read, and you're the drunk landscaper who just weed-whacked your own files.
Nonprofits feel this harder than anyone. Smaller teams, tighter budgets, donor records and grant documents they can't afford to lose. The exact folks who assume Microsoft has it covered are the ones finding out it doesn’t.
So, do this today. Find out who owns your backups. If the answer is the cloud, you don't have backups. Get a real one, test that you can actually restore from it, and sleep better tonight.
Disaster isn't a question of if. It's when.
#Microsoft365 #DataProtection #ITLeadership #Cybersecurity #CloudComputing #BusinessContinuity #security #privacy #cloud #infosec #Backup
This dumb password rule is from Eurocircuits.
Minimum 4 and maximum 30 chars. Use only letters (a-z), numbers (0-9) and underscore (_)
https://dumbpasswordrules.com/sites/eurocircuits/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Fundatec.
Must be exactly 6 alphanumeric characters, does not show special characters are not allowed, username is your social security number (easily searchable) and the form is sent over plain HTTP. Did I mention this company applies college entrance exams for **Computer Science** nationwide in Brazil?
https://dumbpasswordrules.com/sites/fundatec/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
The dutchies have a centralized identity that you are using to basically interact with everything government. That contains pensions and health related issues.
This is called DigID. It is run by a company called Solvinity an was was supposed to be taken over by a U.S. company called Kyndryl.
The dutch cabinet (= government) has now blocked this takeover.
I think the topic of souvernty is slowly landing in the right heads. I guess also ... thank you @bert_hubert and everyone else making noise there🙂
#infosec #cybersecurity #souveraeneInfrastruktur #sovereignty #digid
This dumb password rule is from University of Western Australia (Pheme).
Passwords:
1. Must contain at least 8 characters;
2. Must contain at least 3 out of 4 types of characters
(uppercase letters, lowercase letters, digits, special characters);
and
3. Must not contain
"the user's account name or parts of the user's full name
that exceed two consecutive characters".
...
https://dumbpasswordrules.com/sites/university-of-western-australia-pheme/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Sears.
"cAsE sensitive, no spaces, ! or ?
8 characters min - 1 letter, 1 number
Can't repeat same character more than 3 times in a row
Cannot be or contain your username or email address"
https://dumbpasswordrules.com/sites/sears/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Green Flag.
- 8 to 10 characters
- No special characters
https://dumbpasswordrules.com/sites/green-flag/
#password #passwords #infosec #cybersecurity #dumbpasswordrules

Unsolicited security researcher: I see that your website doesn’t use TLS! This is critical and here are links explaining why.
Me: Yes, it does.
Researcher: Oh. Well, will you reward me anyway?
Me: …
Just #infosec things.
This dumb password rule is from myRTA.
The Roads and Traffic Authority's 'Online Services' website for New South Wales, Australia.
Password rules:
- Must be between 6 and *10* characters long
- Must be a combination of letters and numbers
- Cannot be the same as any of the previous two passwords, including the current password
- Is ca...
https://dumbpasswordrules.com/sites/myrta/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
Interesting.
Socket Joins New OpenJS Program to Fund Node.js Security Work https://socket.dev/blog/openjs-nodejs-security @SocketSecurity
More, from September 25:
OpenJS Foundation Launches the Security Stewardship Program to Fund Ecosystem-Wide Vulnerability Work https://openjsf.org/blog/openjs-foundation-launches-the-security-stewardshi @openjsf #infosec #JavaScript

Hackers Turned Ethereum Into a Secret Messaging System for Malware
A North Korea-linked malware campaign has found a way to keep infected computers connected to its operators. Instead of storing malware on Ethereum, the attackers hide the location of a control server inside cryptocurrency transfers.
The campaign reaches developers through fake job offers, tainted code repositories and malicious software packages. Running the code can install a remote access tool and a credential stealer across Windows, macOS and Linux.
https://cybersecuritynews.com/ethereum-secret-messaging-system/
#Infosec questionnaire pro-tip:
> We currently host most resources in AWS’s … region, but this is subject to change without notice as operational needs arise.
Some askers are insistent that they need to know precisely where their data is hosted. Commit to the larger geo region (eg “in the US (or EU)” as appropriate), but refuse to lock yourself into a single data center. That defeats the whole purpose of cloud computing.
Anyone interested in AI safety, adversarial testing of agentic system, putting Zuck on blast, or having a rolling good time on infosec matters should follow @jonny , and turn on notifications, because he's live-tooting his adversarial testing of Meta's Muse with methods and results both hilarious.
#Muse #Meta #AI #AISafety #InfoSec #PromptInjection #AIAgent
This dumb password rule is from Telekom/T-Systems MyWorkplace.
Telekom's MyWorkplace is a Single Sign On / login hub for their
Open Telekom Cloud which is basically an Amazon AWS clone. It's
rather new and especially for business customers. Especially
because it is for business customers, there's absolutely no reason
to limit a password to 16 characters. Eve...
https://dumbpasswordrules.com/sites/telekomt-systems-myworkplace/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
New.
Another 23-year-old who traded the rest of his life for a criminal shopping spree. And guess what? Turning on a dime, this reformed criminal now works "as offensive security lead at the Dutch company Neo Security." How thin is the separating line?
KrebsonSecurity: Dutch Police Arrest ‘Reformed’ Hacker in Shiny Hunters Investigation https://krebsonsecurity.com/ @briankrebs #infosec #ransomware #cybercrime
This dumb password rule is from Telekom.
At first glance, their policy looks good - sure, the upper limit was chosen without necessity
and they enforce characters from all four groups, but your password manager will most likely come up with something suitable.
The website even tells you how 'wunderbar' your new password is - only to t...
https://dumbpasswordrules.com/sites/telekom/
#password #passwords #infosec #cybersecurity #dumbpasswordrules

To be frank, I’ve become extremely frustrated since the acquisition because now the environment combines the worst aspects of a make-it-up-as-you-go small company with the worst aspects of a faceless corporate overlord. I love my coworkers, I don’t love the general approach to projects and customers.
I live in the Netherlands, I have a skilled worker visa as well as a Dutch marriage, I’m transitioning to citizenship in a year. I need a primarily WFH job but I can hybrid in Amsterdam. I have broad general infosec skills, with the most experience in C source code review but I am familiar with reverse engineering and interested in threat intel. I can provide unlimited access to Mastodon’s most popular dog for morale. #infosec #FediHire #jobs #jobsearch
This dumb password rule is from Merrill Lynch.
Passwords must be between 8 and 20 characters, and some special characters are allowed. Users with randomly-generated passwords may find it particularly annoying to generate a password that works for their password safe.
https://dumbpasswordrules.com/sites/merrill-lynch/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Polytechnique Montreal.
Passwords must have a minimum length of 8 characters
Passwords must have a maximum length of 30 characters
Passwords must contain a minimum of 2 digits
Passwords must contain a minimum of 2 letters
Password must be different than the last one used
Passwords may contain these special characte...
https://dumbpasswordrules.com/sites/polytechnique-montreal/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Apple.
Can't contain 3 or more consecutive identical characters, nor can it be more than 63 characters long.
https://dumbpasswordrules.com/sites/apple/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Stuttgart Media University.
Your password has to be between 10 and 14 characters.
Also, you need to have at least one number, one uppercase letter and one lowercase letter.
And at least one of these special characters: ```!.,;+-=#$()[]{}&*```.
But don't use any of these special characters: ```<>|§@€?:%^\"'`°~```.
And don't...
https://dumbpasswordrules.com/sites/stuttgart-media-university/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Estheticon.
- At least 8 characters but limited to 20 characters at max
- At least 1 digit
- At least one letter (just a letter in general, no specific casing required)
- No special characters at all
https://dumbpasswordrules.com/sites/estheticon/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Rogers.
I can only use 4 special characters?
Password guidelines
- Your password should be between 8-20 characters and have at least one number and one letter.
- The following special characters are allowed: ! @ # $
https://dumbpasswordrules.com/sites/rogers/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
Socket, posted yesterday: Malicious Firefox Extension Poses as PDF Identity Verifier to Hijack Google Accounts https://socket.dev/blog/firefox-google-account-takeover @SocketSecurity #infosec #Firefox #Google #cybercrime

#EconomicJustice is an #infosec issue.
Cybersecurity defenders face an ever-growing flood of professionalized online criminal activity: hacking, scams, ransomware, fraud, etc., etc.
One thing many online criminal groups have in common is, they’re located in impoverished countries where the standard of living is brutal, life is precarious, and many people think that stealing from people in first-world countries is reparations for the harms of #imperialism and #colonialism.
1/3
I WONDER WHAT FIREWALL THEY GONNA RECOMMEND
#Shitpost #Shitposting #Infosec #ShamelesslyStolenFromReddit
Alt...
This image is an advertisement for Palo Alto Networks' interactive firewall selector. It invites users to try the guide to select the best security for their cloud workloads and applications.
This dumb password rule is from CVent.
Password Rules
- 8 to 20 characters with at least 1 number and 1 letter.
- No symbols or spaces.
https://dumbpasswordrules.com/sites/cvent/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Inria.
This is the account for those who work at [Inria](https://www.inria.fr/)
"the French national research institute for
the digital sciences".
You have to wonder what's wrong with these special characters but not
the other ones.
- Password expiration once a year
- Your password must contain at leas...
https://dumbpasswordrules.com/sites/inria/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
I am suspicious of the reports that an #OpenAI agent "hacked" a government website in #Australia.
No concrete details have been given of what the "hack" entailed.
I am suspecting that the agent was able to access data that wasn't meant to be public either by guessing unlisted URLs or leveraging an IDOR vulnerability.
In my opinion, the primary blame for either of those would lie with the Australian government for building an insecure website, not with OpenAI.
https://en.wikipedia.org/wiki/2026_OpenAI_infiltration_of_Medicare
#infosec
1/2