Search results for tag #security

Another coordinated Nix/Lix #security update. Have a look!
Offical advisory: https://discourse.nixos.org/t/security-advisory-for-nix-and-lix-october-2026/80547
Lix blog post: https://lix.systems/blog/2026-10-13-lix-cves/
CVEs for these issues are pending.
week 26's app icon is for Lockpicker: "Recover passwords from their hash" by @sstendahl
check out all my recent app icons here:
https://planetpeanut.studio/icons
and if you want to help sponsor the effort:
https://planetpeanut.studio/sponsors
it really helps. 🌱
#linux #gnome #opensource #foss #app #icon #design #security #cryptography #password #hacking
Alt...
An unlocked purple padlock on a teal background with a light gold hairpin sitting diagonally in front of it.
week 27's app icon is for KawaiiFi: "Wi-Fi scanner and analyzer" by Zach Leytus
check out all recent icons here:
https://planetpeanut.studio/icons
and if you want to support an-app-icon-a-week:
https://planetpeanut.studio/sponsors
it really helps! 🌱
#linux #gnome #opensource #foss #app #icon #design #wifi #security #cute #kawaii
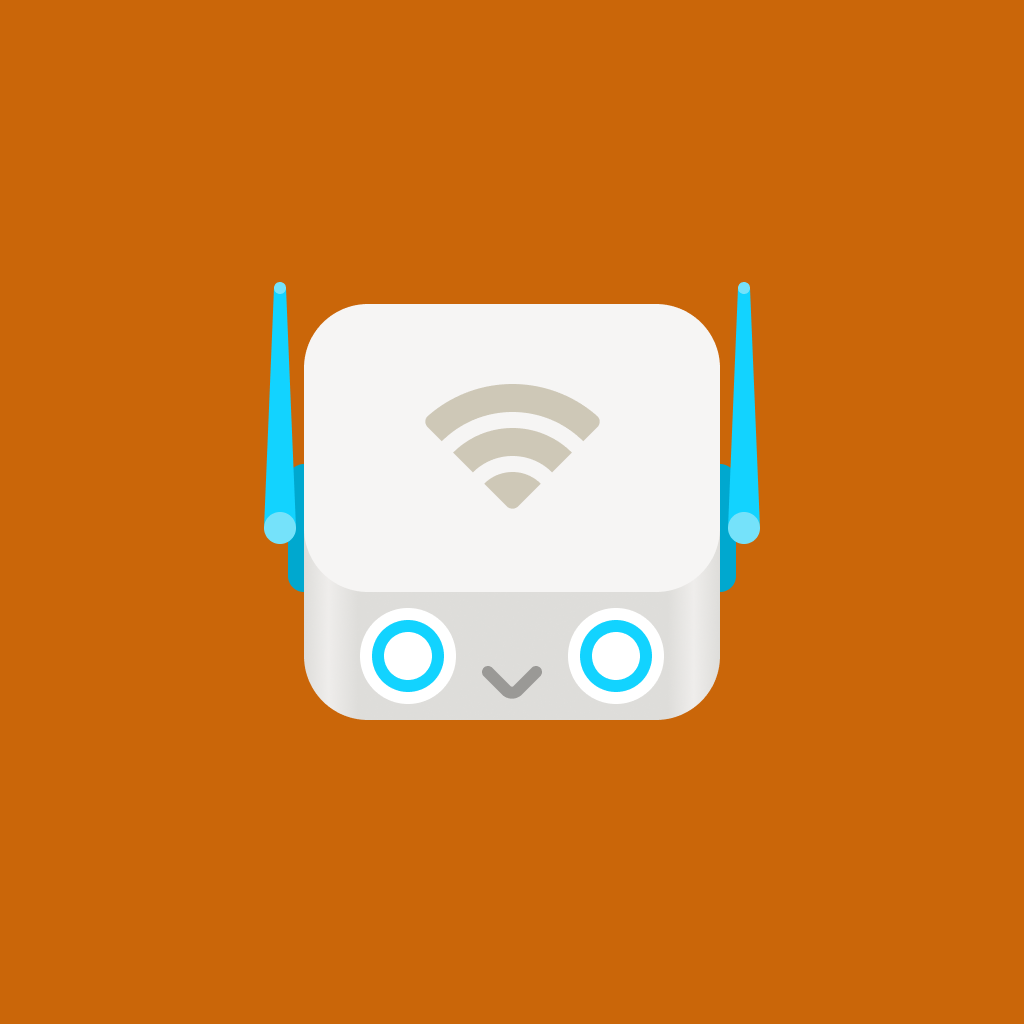
Alt...
A rounded rectangular wifi router with two blue antennas sticking out from the sides. the top has a Wi-Fi symbol, the from a "O v O" face.

@rmondello I find the #attestation part of that article is actually fair in some aspects.
Hardware attestation seems fundamentally #antiuser to me and is typically done via #closedsource #security theater. Now I'm just a random person on the internet, that's a good point.
But I'm not the only one: https://www.gnu.org/philosophy/can-you-trust.html
While #TOTP is fishable, and the article is weaker for not acknowledging it, I think there is a point to be made that it still is a useful defense against other threat models and has therefore arguably more than zero increased value - whether that makes it "great" or not.
Some of us are of the opinion that if #passkeys aren't some trusted computing scheme, perhaps hardware #DRM shouldn't be part of the standard. Beyond at most cheap separate portable hardware key dongles (and even those seem questionable to me as a possibly enforced item). Yet #TPM attestation is in there: https://www.w3.org/TR/webauthn-2/#sctn-tpm-attestation
I also find the claim that the writer of the article isn't "understanding the topic being discussed" is weakening your points!
Nevertheless, your insight was useful and I appreciate you entering the discussion.
Alas, this will always be a risk with this kind of #van - many have #engines where timing belt runs in #oil - if #servicing is neglected its easy for the belt to perish and split altogether, causing the engine to lose timing and valves to clout the pistons (requiring multiple parts replacements).
So there's always a criminal market for "cheap" engines, places like #FoodBanks are seen as soft touches as they lack the #security resources of corporates and may even be targeted by angry men who think they are too "woke" (especially as they often help out domestic violence victims who are fleeing abusive situations)
@stux is het inmiddels (weer) mogelijk om een account op mstdn.social te registreren met een alias emailadres van @protonprivacy ?
#privacy #security #proton
Canonical reports a DDoS attack has taken several of their websites offline.
Critical services, like repos, PPAs, Snaps, etc are not affected.
https://www.omgubuntu.co.uk/2026/10/ubuntu-website-ddos-part-2?v1
This is not security. This is the exact opposite of it. This is new and If I have to wildly speculate they are just migrating from one system to another and need to refresh the hashes stored. It has all the signs.
Just effing say so!
Alt...
Connection expired. For your security we will periodically ask you to reconnect.

So in the last 20 years, has anyone in open source actually figured out a good way to do cryptography in a way that doesn't involve the terminal or interacting directly with files? Or is it still just a privilege that the tech-illiterate folks aren't allowed to enjoy?
I know there are a few GUI programs that are like wrappers for OpenPGP and such. Are those any good for people who aren't technical?
I wanna mess around with various options. Any recommendations?
#techSupport #askFedi #crypto #notThatCrypto #encryption #cryptography #security
xorg-server 21.1.25 and xwayland 24.1.14 released due to more security issues https://www.gamingonlinux.com/2026/10/xorg-server-21-1-25-and-xwayland-24-1-14-released-due-to-more-security-issues/
LibreSSL 4.2.2 and 4.3.3 released https://www.undeadly.org/cgi?action=article;sid=20261007052424 #openbsd #libressl #openssl #tls #ssl #https #cryptography #security #crypto #portablesoftware #freesoftware #libresoftware
What did this old #gammon think would happen?
Its not his job to audit what headgear customers are wearing, let alone try and guess their religion - presumably #Waitrose in #Worthing has #CCTV and #security staff like everywhere else and if they thought the chap with the helmet was dodgy they would have stepped in (any ban on wearing them is more a precaution against robbery, but its equally likely he was simply riding a motorcycle and maybe even picking groceries for home delivery so the staff knew him!)
Also why was he intervening in a complaint from some old granny lady about the state of loos? He's not allowed to go into loos that aren't for his gender presentation anyway - should have just bought his chocs for his ill friend and kept quiet...
Ubuntu is shaking up its OpenPGP implementation, adding Rust-based Sequoia PGP to 26.10 installs.
GnuPG is still included, but Canonical plans to phase it out in a future release.

NVIDIA security bulletin for Sept 30 notes many GPU issues https://www.gamingonlinux.com/2026/09/nvidia-security-bulletin-for-sept-30-notes-many-gpu-issues/
OpenBSD 8.0 is due out soon, and -current snapshots identify as 8.0 already. So it's time to reprise "You Have Installed OpenBSD. Now For The Daily Tasks." https://nxdomain.no/~peter/openbsd_installed_now_for_the_daily_tasks.html which should help answer some common questions. #openbsd #newrelease #maintenance #sysadmin #security #dailytasks #freesoftware #libresoftware
 boosted
Blair is reported to have said that the Freedom of Information Act was one of the things he regretted the most. Possibly even more than Devolution (although that was inevitable). This is an example of why. The government must hate it.
But don’t worry, practice will make perfect.
#FOI #FreedomOfInformation #Blair #Labour #Legislation #UKPol #FacialRecognition #Privacy #Security

OpenBSD -current has moved to version 8.0 https://www.undeadly.org/cgi?action=article;sid=20260927120854 #openbsd #current #newversion #pleasetest #development #networking #security #freesoftware #libresoftware
OpenBSD gains new networking daemon - rtrd(8) https://www.undeadly.org/cgi?action=article;sid=20260927120124 #openbsd #rtrd #rpki #bgpd #routing #networking #security
Turns out WebKit cannot store a non-extractable X25519 CryptoKey in IndexedDB.
Kind of a big deal for security/privacy.
If you know anyone at Apple/on the WebKit team, please nudge them about this.
https://bugs.webkit.org/show_bug.cgi?id=312279
#webkit #cryptography #security #privacy #x25519 #indexedDB #safari #apple #web #dev #SmallWeb