Search results for tag #networking

NixOS bullshit thread [SENSITIVE CONTENT]
@cxberger The simple answer is that writing the recommendation to the wiki was a simple thing to do. Changing networking defaults on the default install is a much more complicated endeavour.
The recommendation for `systemd.network` originates from discussions in #networking:nixos.org, the author of the networkd page for the most part me.
Tonight it's #NetMCR (https://www.
netmcr.uk/) in #Manchester from 7pm!
"For our September meetup, we’ve a short talk and space for more if you’re keen to offer something on the night:
* Lightning talk: Tim Wilkes, ‘An intro to the NICC’s Open Forum’*
- Just a quick overview of the NICC’s Open Forum and why it might be of interest to attend, later this year."
Go and chat with some nice people, have some weird 🍻, and if you're hungry, 🍔 and 🍟!
There will be a PF tutorial at EuroBSDCon 2026 in Brussels:
Network Management with the PF Packet Filter Toolset on OpenBSD and FreeBSD
Featuring Tom Smyth and Peter Hansteen, 2026-09-11, 10:30, full day
See https://events.eurobsdcon.org/2026/talk/RKCHRW/
To register: https://tickets.eurobsdcon.org/eurobsdcon/brussels/
#eurobsdcon #bsd #openbsd #freebsd #networking #firewall #security

I haven't explored the rest of this site yet, but this writeup I found that basically matches my home network hardware to a T is proving to be a perfect resource for me in getting VLANs setup. Peeking at the menu it looks like this is most likely a great resource for other stuff as well.
Hey #IPv6 folks: If I do NOT have a /64 assigned to me and only have a single IPv6 assigned, am I better off adding fd00::/7 addresses to the jails and then NAT'ing to them like I do with the IPv4 addresses?
I don't think I have any other kind of choice here.

The fascinating part of my home FTTH connection is that the latency is extremely low.
In other words, if I'm somewhere else with a comparable connection, I get a latency (via WireGuard and toward a host on the LAN) of around 20 milliseconds, which is barely more than what, just a few years ago, you would get on a local Wi-Fi network.
In short, it feels like working locally. It might sound obvious, but it never fails to amaze me.
Excited to have ordered my first length of fibre ever! When I started learning networking there was still Coax around and Fibre was a mythical beast!
Now I am going to start replacing the Cat5 in my house for the #homelab
woot!!
Ironically the first run of fibre is the one that has never had physical network cable before, outside. But you gotta start somewhere.
My only question is if Telus has an ONT/gateway box that has both SPF and Ethernet ports? 🤔 questions for another day. This is not a high priority project but nice to get started in earnest.
#homelab #networking #fibre #home #diy
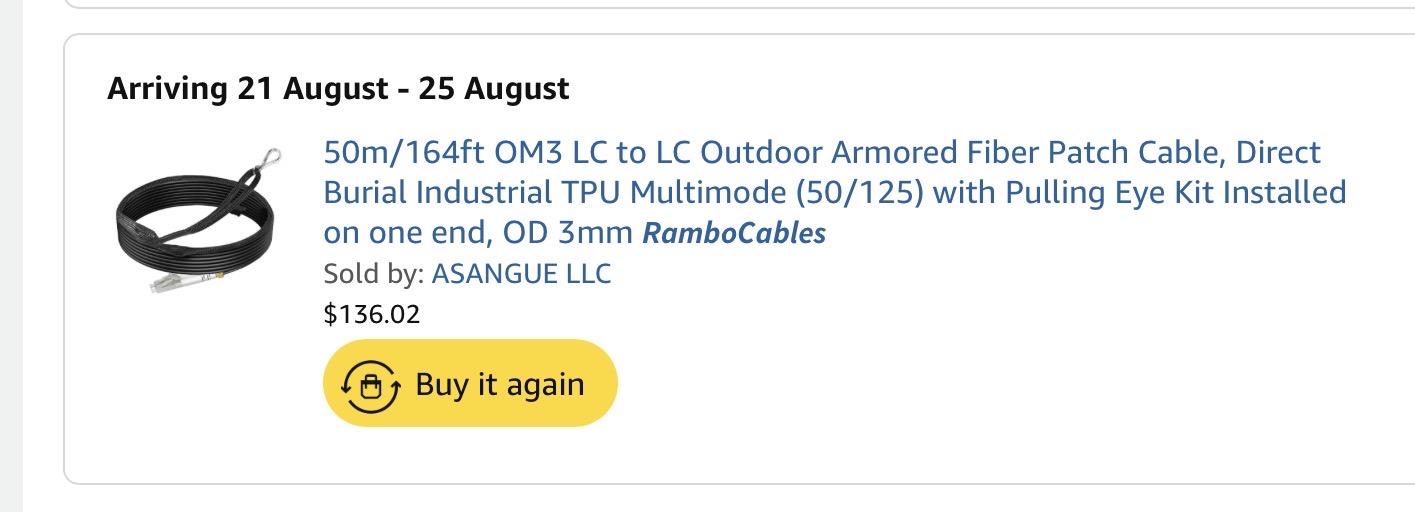
Alt...
Amazon screenshot
Arriving 21 August - 25 August
50m/164ft OM3 LC to LC Outdoor Armored Fiber Patch Cable, Direct
Burial Industrial TPU Multimode (50/125) with Pulling Eye Kit Installed
on one end, OD 3mm RamboCables
Sold by: ASANGUE LLC
$136.02
Buy it again
This week at SIGCOMM, Inho Choi will present a paper about a fast TCP migration and load balancing system called Capybara, which means it’s time for… another episode of Distributed Systems Explained by ̶C̶a̶t̶s̶ Capybaras!
L4 load balancers are fast, scalable, and widely used in cloud systems: when a new connection arrives, the load balancer picks a server for it. For our purposes, connections are birds and servers are capybaras.
This bird has been assigned to a server.
[🧵, 1/9]
#distributedsystems #networking #capybara #sigcomm #distributedsystemsexplainedbycats

Alt...
a capybara with a yellow bird on its head

OK, #fediverse #hivemind, here's a #question.
I want to put #VPN gateways at my house and my mother's house 500 km away, so I can have remote access to both home networks.
Given everything that's going on in the consumer router market, what would you suggest?
I was at one point considering the D-Link DSR-250V2. Is there anything else out there that's reasonably priced and reasonably secure? Are there any #FOSS solutions for this? #networking

Alt...
product information image for the D-Link DSR-250V2

Alt...
product information image for the D-Link DSR-250V2
Finally getting around to trying to learn #Wireshark and understand some of the network stuff a little more.
One of the first things I noticed which seems kind if odd to me is that periodically I see a slew of #ICMP ping requests to my laptop IP from source addresses that are external to my network.
Is this normal? What external IPs should I be expecting to send ping requests to my laptop on my home network?
Note to self: Just don't touch #ipsec. It's shit all way round and always breaks. Just use something else.
Why?
Every time I want an encrypted tunnel between two public IPs I think like "oh yea, using IPSec here would be easy and straight forward".
And then it never fucking works reliably. And if it does work it stops to work the next time you try to apply the exact same config. And it fails with shit like this...
What have I done wrong?!? Why work sometimes??



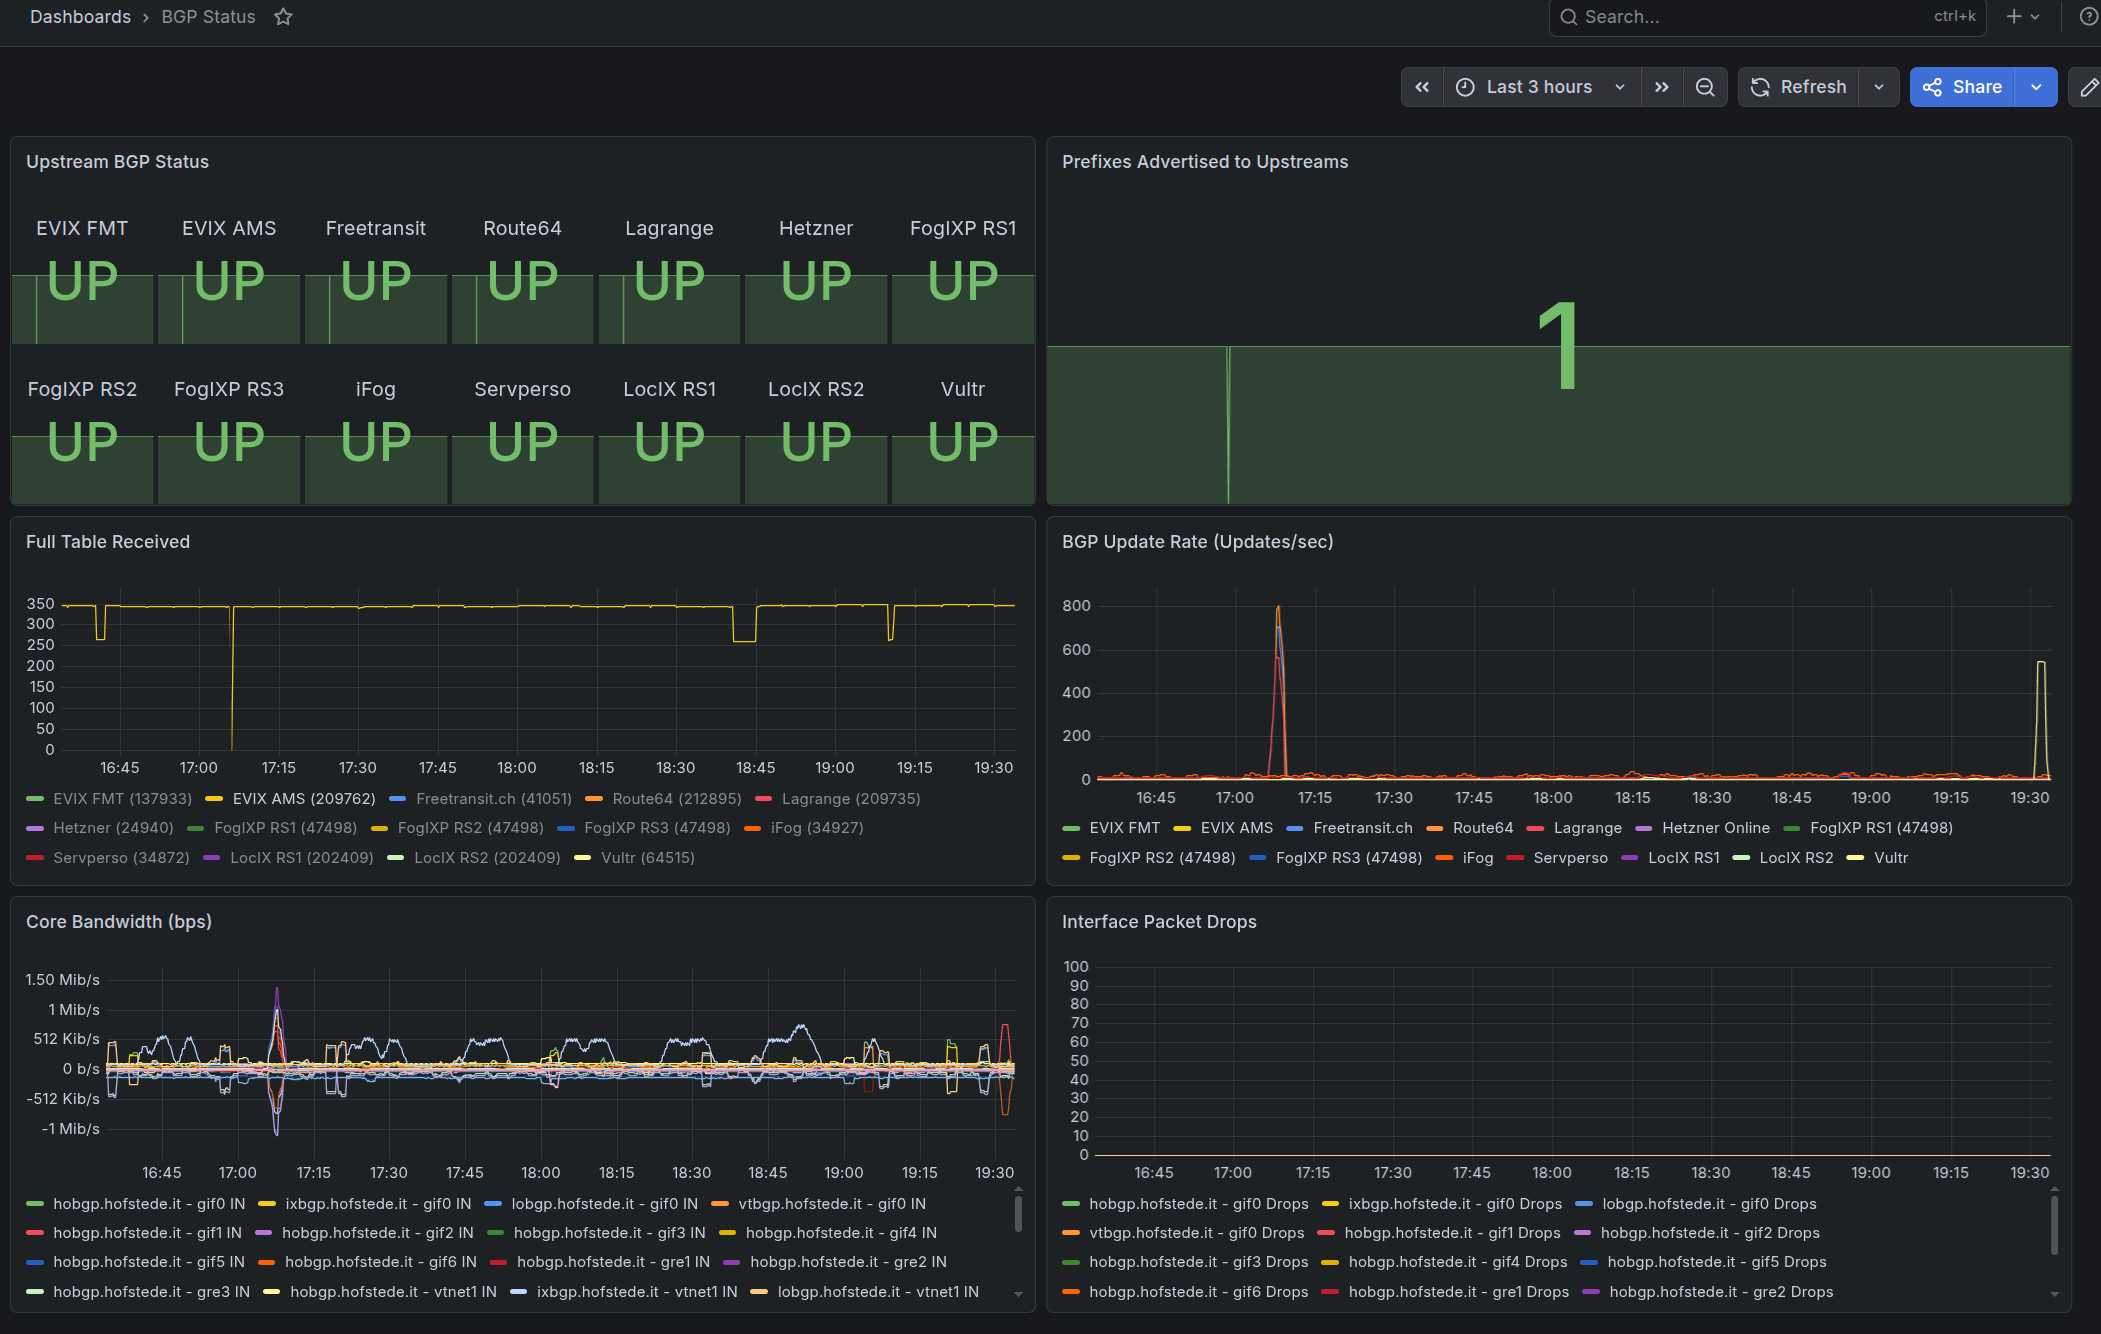
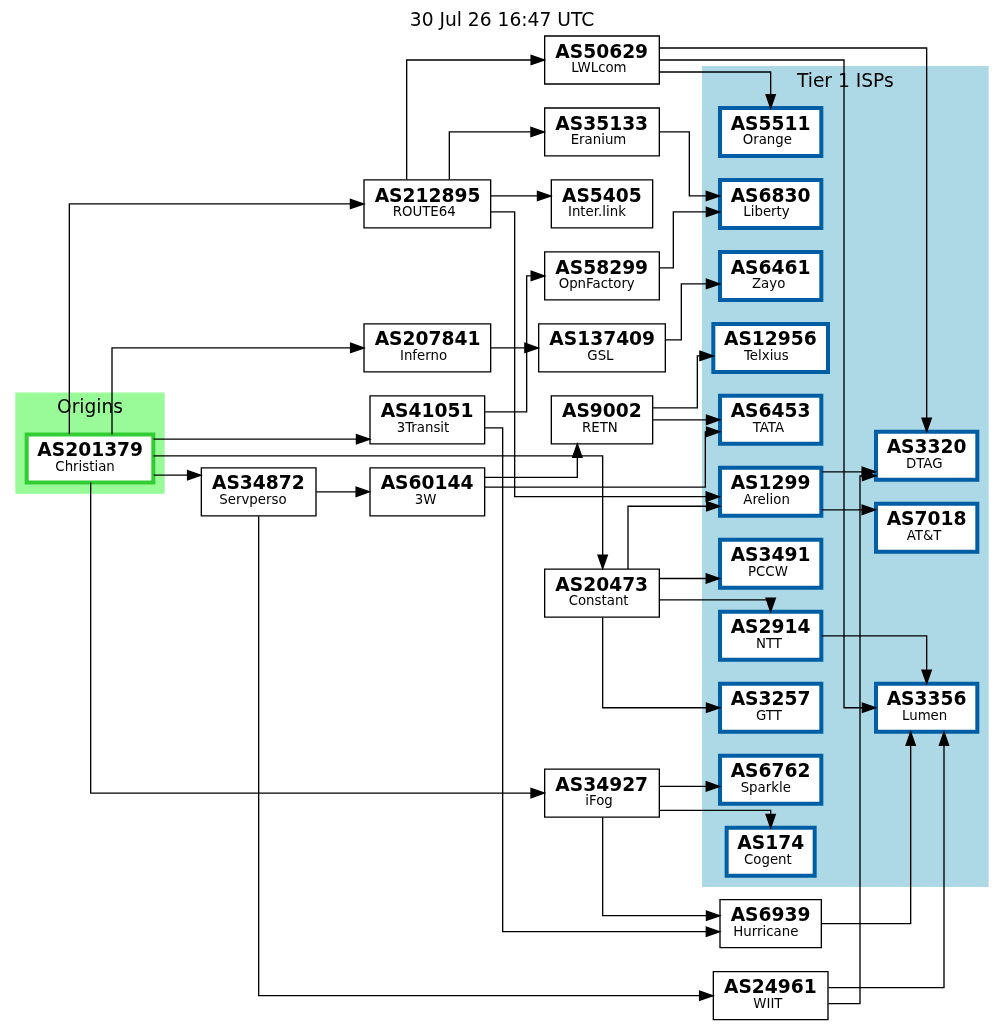
I really don’t need any more peers for my AS201379! (Okay, maybe a few more...)
Started back in December 2025, and now this "little" infrastructure is running:
14 individual eBGP sessions
3 Internet Exchanges
Multiple transit providers
110+ direct peers
All 100% IPv6 (2a06:9801:1c::/48) because legacy IP belongs in the last century.
Powered entirely by FreeBSD  : 4 routers on 15.1-RELEASE running FRR and PF.
#BGP #IPv6 #FreeBSD #Routing #Networking #sysadmin
Are there any #networking and/or #homelab types out there who can offer an answer to a question I have?