Search results for tag #linux
Hey #Linux people.
⚠️I am not techy - please keep this in mind if replying.
I got a cheap Kindle Fire HD 10 for a LARP. I used it as is yesterday (cos time) but I would like to put Linux on it so it's more customisable.
I just need it to edit and view PDFs, make notes, and view web pages.
Ability to connect a portable keyboard would be great but not essential.
Is this achievable for a non techy chronically ill human?


I'm really enjoying the now accurate dates announcements in GNOME Calendar's minicalendar widget (in the sidebar and the event editing dialog's date picker) for screen reader apps for vision-impaired users, as detailed in https://gitlab.gnome.org/GNOME/gnome-calendar/-/work_items/1446.
Here's a video showing how the current nightly version works with Orca as I navigate the widget with the keyboard… there's more to it than the eye can see!
#GNOMECalendar #accessibility #a11y #usability #screenreader #Orca #GNOME #Linux #calendar
@thelinuxEXP
Really looking forward to #Affinity on #Linux
The craft apps are useful for importing and exporting stuff but they are a long way off being usable.
Here is today's #Linux and #OpenSource news video!
In this one, we have Affinity and macOS apps coming to Linux, Proton clarifying the "AI situation", Mint showcasing more new apps, some unfortunate SUSE layoffs, and a lot more!

Heya folks! It's sync day, and that means it's time for the weekly Solus roundup! Read all about it on our forums: https://discuss.getsol.us/d/13121-week-45-2026
#FOSS #Linux #Solus #OpenSource
- Evan
There are a lot of new #Linux distros/desktops popping up, and just my opinion, but I would not use anything that's been #VibeCoded unless I knew with certainty that the developers are coders and have a plan for maintaining it. Anything less, and you're stuffing your computer with asbestos.


Desktop icon survey results are now in my blog: https://akselmo.dev/posts/desktop-icon-survey-results/
 boosted

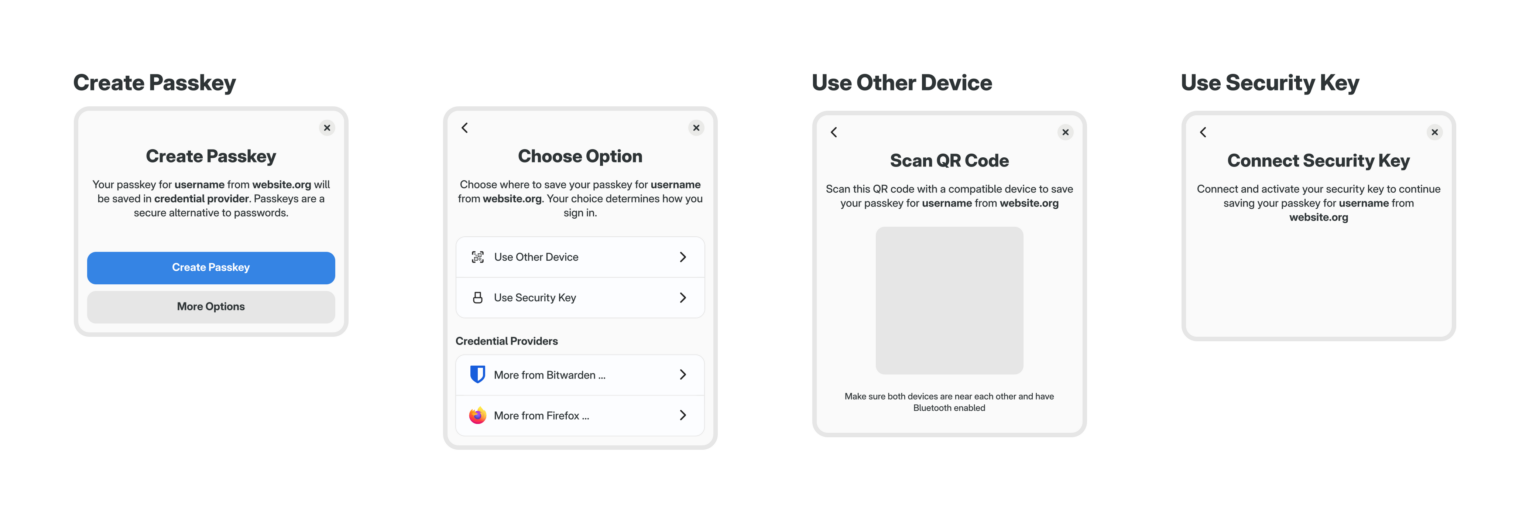
#Passkeys on #Linux is getting closer!
The Credential portal has been merged to be enabled with a feature flag in the next release of xdg-desktop-portal.
The GNOME design team, funded by the Sovereign Tech Fund, has produced a design for using passkeys in the GNOME desktop environment. https://blogs.gnome.org/psauberz/2026/11/06/fellowship-update-2026-11-06/
The Credentials for Linux project is going to take that feedback back to credentialsd and work with the community to implement the designs.
Exciting stuff!
Alt...
Some details of the credentials portal mockup showing the passkey creation
[$] Locking down hibernation for the winter
When a computer hibernates, the kernel writes the contents of memory to disk and then shuts the system down. Resuming from hibernation involves reading that data back into memory, [...]
The first open source software that we used, and the FOSS that we have most recently started using regularly.
https://linuxafterdark.net/linux-after-dark-episode-134/
Alt...
Linux After Dark artwork
Just a reminder that we are 100% independent, come support us :) https://www.gamingonlinux.com/support-us/
Sending email via my usual webmail interface is working fine.
Sending email via the command line utility that I use is *mostly* working fine.
There is one destination (that I know of!) that is rejecting email with:
550 5.7.1 Message rejected:
Message lacks SPF/DKIM/DMARC Auth Records
So they get delivered via the web interface, but not via the script I'm using.
* I own my own domain
* I can connect via shell
* it is shared hosting
* I do not administer the machine,
* My access to logs is limited
* my options are limited.
I'm currently *really* busy with other things, but it would be really nice to get this fixed. If someone can provide me with the right level of "This is what's wrong" then I'd be very grateful.

This week, I had to do some work with Linux, so I found myself working with Alpine Linux again. And, of course, one of the worst and most absurd security vulnerabilities in recent times popped up. 😆
Fortunately, none of my setups met the conditions required for exploitation.
That said, I've been running some interesting experiments on a Raspberry Pi 4, the same one that has been running FreeBSD for quite some years, hosting a Time Machine service in a jail and handling backups from other servers.
Long story short, I installed Alpine Linux on the Raspberry Pi and moved FreeBSD into a KVM virtual machine, with the disks passed through directly to it.
The result? The VM runs beautifully with 3 GB of RAM (possibly even 2 GB), and I still have the rest of the Raspberry Pi available to run OpenBSD, NetBSD, and other systems I need for different setups.
It's a sad that bhyve doesn't (yet) support virtualization on that device. Or at least, that was still the case the last time I checked.
New blogpost:
"Running a law firm on Free software (2026 edition)"
This is an update, covering what has changed in the last couple of years.
I will write about some of the bits separately, when I find some more time!
https://decoded.legal/blog/2026/11/running-a-law-firm-on-free-software-2026-edition/
The latest iteration of @fedora has arrived with @gnome 51 and @kde Plasma 6.8
https://www.linux-magazine.com/Online/News/Fedora-45-Now-Available?utm_source=mam
#Fedora #GNOME #OpenSource #Plasma #Linux #FOSS
Alt...
Linux Magazine News

Today's C programming exercise: what can possibly go wrong with the KEY_MAX check here (MUSL SHA512 implementation)?
/* key limit is not part of the original design, added for DoS protection. */
#define KEY_MAX 256

// ...

static char *sha512crypt(const char *key, const char *setting, char *output) {
  // ...
  /* reject large keys */
  for (i = 0; i <= KEY_MAX && key[i]; i++);
  if (i > KEY_MAX)
    return 0;
  len = i;
  // ...
}
(Note that this was done for legit reasons, large payloads can clog sha512crypt and result in a DoS).
Hint: look what's been hiding in plain sight since the first version of MUSL:
on error "*" is returned.
So MUSL basically said "fine, crypt() returning NULL in case of error just crashes a lot of applications, so we'll always return a string and in case of error you'll get a "*"".
Again, a fair point (even though one that arguably breaks the UNIX contract of crypt()). Rather than crashing applications that always forget that crypt() can also return a NULL, just return a placeholder in case of errors that will never match upon comparison.
A couple of years later, 2016, OpenSSH gets CVE-2016-6210 - a potential user enumeration vulnerability.
The reasoning is simple. Logging in a user that doesn't exist usually results in an immediate error, while a user that exists will take a bit longer because stuff needs to be encrypted and hashes compared - and thanks to that time difference an attacker could brute force a system to figure out what users exist.
How did OpenSSH solve that problem? Well, the solution was as creative as it can get:
/*
 * If we don't have a salt we are encrypting a fake password for
 * for timing purposes.  Pick an appropriate salt.
 */
if (salt == NULL)
  salt = pick_salt();
It basically says "the user you're asking for doesn't exist, but I'll just pick up the salt of another random user and encrypt your password anyway - just for the sake of wasting time, so you can't guess by the request time if the user exists or not".
Again, it may be unorthodox, but it's a sensible solution to prevent timing-based user enumeration on the system.
But wait, what's the UNIX /etc/passwd convention for users with login disabled? That's right:
daemon:*:1:1:daemon:/bin:/bin/false
A * instead of the actual password.
And on #Alpine #Linux root has a * - it disables login, but, unlike !, it doesn't break PAM-authenticated SSH keys too.
How does #ssh check your password on login?
It looks into /etc/shadow, and if it sees a $6$ hash it assumes that it's SHA512.
But what happens when you try to log in as root? And maybe with a password longer than 256 characters?
The * in /etc/passwd prevents you from doing that. But OpenSSH won't tell you no directly. It'll try to get the salt of one of your neighbours and encrypt your password anyway.
But what if you get the salt for a SHA512 hash?
Remember that sha512crypt on MUSL was designed to specifically fail if you pass a payload longer than 256 characters.
And what does crypt() on MUSL do when the underlying crypto routine fails?
That's right - rather than NULL, it returns *.
So what does SSH do then?
It compares what crypt() returned (*) to what /etc/shadow contained as the password for that user (*).
And boom.
Note that this critical security vulnerability has been the result of unorthodox fixes for real problems that, when compounded together, led to an explosive mix.
It's fair for a password hashing function to refuse to encrypt payloads that are too long to prevent DoS. But it perhaps should have done so by raising errors that the downstream consumer could interpret.
It's fair for a library developer to assume that most of the folks will always expect crypt() to return some string, and a lot of stuff may break if there are errors. But perhaps silently returning an arbitrary string in case of errors isn't something you'd expect from a standard library.
It's fair for OpenSSH to prevent timing-based enumeration attacks by making sure that the same time is spent on each authentication request, regardless if the user exists or not. But perhaps picking up the salt of another random user to encrypt the password passed by another user is just begging for something to go wrong at some point.
This is a case where 3 unorthodox solutions to 3 real problems compounded together to create a problem that is even bigger than the problem they were trying to solve individually.
The lesson: if you write code, make sure that it always works in predictable ways. Make sure that it does what's expected for it to do, that it always returns what people expect it to return. Don't let individual problems break that contract if possible. And don't fail silently if possible.
Because when your code starts doing something that people don't expect it to do, you're just asking for a CVE to come in your ways - weeks, months or even years later.
I have just realised that, when I see someone tooting here about software that they have developed, it is very rare that it is not FOSS.
That proprietary software is - for me and my feed - the exception, rather than the rule.
A new GOG Galaxy is coming in 2027 with full Linux support https://www.gamingonlinux.com/2026/11/a-new-gog-galaxy-is-coming-in-2027-with-full-linux-support/
@mathzy @Tutanota @protonprivacy I understand.
I feel that it is a shame that we are looking for the "least worst" alternatives in so many areas of tech.
I mean, I am comfortable with debian based Linuxes but AI code is now in the #Linux kernel.
Maybe that is the way it has to be but it spurs me on to try to get to grips with #NetBSD.
I'm looking for a "craft beer" operating system. Conforming to the tech equivalent of the Bavarian beer purity laws.

There's a vulnerability on If I had my Alpine computer working at the moment, it wouldn't affect me because I don't have SSH turned on. If you're not able to update yet, be sure to turn off password authentication. Source: musl based linuxes for SSH where the password can be easily bypassed by including a long enough password and meeting some other requirements.

Big learning curve yesterday, trying to get a Phidget load cell playing nicely with a python script on Linux. I am a rank beginner with Python. Finally got the hardware USB recognized and the script running without error messages. Also had to learn how to make a virtual environment and run everything under that. The key was getting the virtual environment to see the global python libraries by adding the command "python3 -m venv --system-site-packages
.venv" when creating the environment. It might be obvious to you pros, but was not mentioned in any official Phidget documentation that I could find. There is an official Control Panel that is only available for Windows and macOS, but not for Linux.
Next up, making a script to live graph the load cell vs time.

Alt...
Load cell for measuring applied force mounted on a yellow steel plate with four bolts
[$] User namespaces + file capabilities = trouble
User namespaces are a key part of the kernel's toolkit for assembling containers; processes within a user namespace can appear to have full root access to the system while gaining [...]
Critical security vulnerability affects OpenSSH on Alpine Linux systems
[$] LWN.net Weekly Edition for November 5, 2026
The LWN.net Weekly Edition for November 5, 2026 is available.

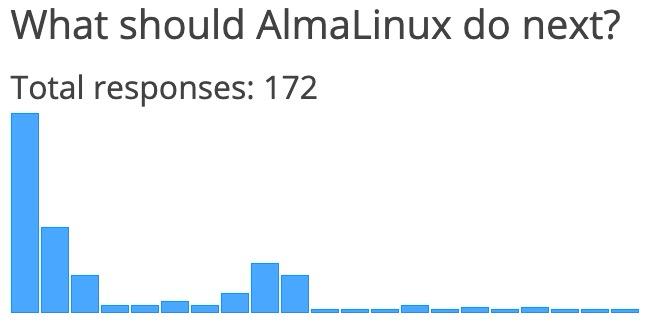
It's been 3 weeks since we opened the @almalinux "What next?" survey, and this trend is interesting to me. I think it's the same for nearly all surveys, but that long tail is hard to watch.
The biggest reason: I know that millions of users across the world are impacted by our decisions, but only 172 people have shown up to make their voices heard.
My goal is 200 responses, and with only 12 days left it's going to be hard to hit that. Help me by sharing the link in your own communities and making sure as many perspectives as possible are heard.
If you care about AlmaLinux as a platform, show up. Your voice will absolutely have an impact.
https://almalinux.org/survey #linux #opensource
Alt...
A bar graph showing tall bars at the left, and much small bars toward the right, indicating a lot of engagement early, and less engagement over time
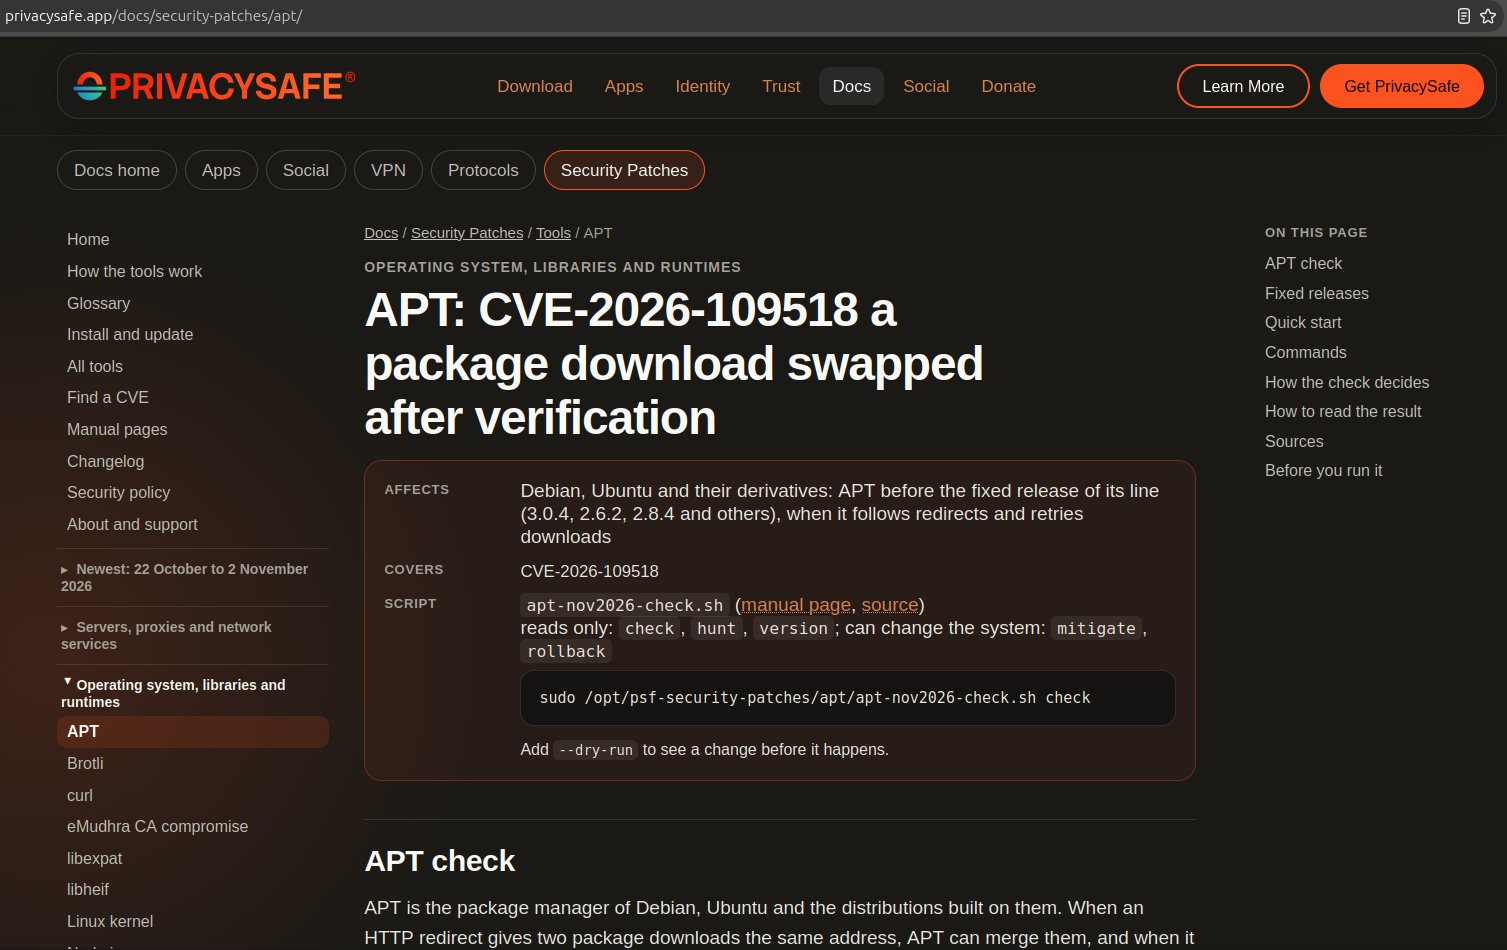
🤓 Our @privacysafe team has done it again and offers a FREE #cybersecurity tool for fixing a major vulnerability on #Ubuntu and #Debian GNU / #Linux. Support our effort! https://privacysafe.app/docs/security-patches/apt/
Alt...
APT CVE
#Affinity kommt für #Linux  | heise online https://www.heise.de/news/Affinity-kommt-fuer-Linux-11509360.html
[$] Plasma X11 session removal surprises some Fedora users
The KDE Project announced, in 2025, that Plasma 6.7 would be the last version of the desktop environment that would support X11 sessions. Those who keep up with KDE's announcements [...]
NVIDIA stable driver 620.70.06 released for Linux https://www.gamingonlinux.com/2026/11/nvidia-stable-driver-620-70-06-released-for-linux/
[$] Portable Python scripts with dependencies
A basic Python script is portable: it can be copied between machines with little concern about compatibility. A script that depends on third-party packages requires quite a bit mor [...]

Which one should be the default?
Vote below! 👇
| Classic Slackware: | 0 |
| Minimalist Slackfetch: | 0 |

Debian Linux apt security update: man-in-the-middle arbitrary code execution. Apply updates as soon as possible.
https://lists.debian.org/debian-security-announce/2026/msg00526.html
Die #SpendeDesMonats geht diesmal an den #Signalmessenger
#Signal ist für mich die sinnvollste Alternative zu den ganzen
"TechBro"-Messengern. 👍️
Unterstützt auch eure lieb gewonnenen Software-Projekte! Nur weil der Download nichts
kostet, heißt es nicht, dass kein Aufwand hinter den Projekten steckt. 👍️
 [
I have the damnedest #Linux problem with my desktop. I've been trying to get Windows off the last computer in my house and it's a challenge, y'all. It hates my RTX 4070 and I'm not sure how to fix it. Under Windows everything works fine. I installed #Bazzite ( #fedora really) and on startup it recognizes all four of my monitors and works fine, until the displays go to sleep.

 [
fucking #NVIDIA #linux driver install bullshit has been kicking my arse for several days now… 😤😡🤬 😩
I’ve learned / re-learned more filesystem (#btrfs) / grub / initramfs / sys config / recovery troubleshooting bs than I care to poke several large sticks at (yay? 😩) & have finally declared (temporary) defeat by just reinstalling so that I can regroup & re-try now that I’ve saved ALL the articles & written ALL the reference notes… 😮💨
(my homedir is on its own partition so it's nbd but still 😕)
but first, coffee 🙃
#ComputerToucherBS
Bazzite 45 arrives powered by Fedora Linux 45 for gamers https://www.gamingonlinux.com/2026/11/bazzite-45-arrives-powered-by-fedora-linux-45-for-gamers/