Search results for tag #cybersecurity

This dumb password rule is from Vélib’ Métropole.
Your password must be at least 10 characters, with at least 1 uppercase character, 1 lowercase character, 1 number and 1 special character (only from this list: @, $, €, #, %, *, ., ;, !, ?).
You're not allowed to paste passwords.
https://dumbpasswordrules.com/sites/velib-metropole/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
Hackers use fake coding tests to infect 30,000 devices and steal $10 million in crypto
Authorities tie the campaign to North Korean group WaterPlum, part of a wider $500 million-a-year fraud scheme
https://www.techspot.com/news/113916-north-korean-hackers-use-fake-coding-tests-infect.html
Morgen ist es so weit: Die #INFORMATIK26 startet an der TU Dresden.
Das Festival dreht sich diesmal ganz um das Thema digitale Resilienz. Was das konkret bedeutet, darüber haben GI-Präsident Martin Wolf, Vorstandsmitglied Ina Schieferdecker und @HonkHase mit dem #mdr gesprochen: https://www.mdr.de/wissen/naturwissenschaften-technik/informatik-festival-dresden-ausfaelle-aushalten-,digitale-resilienz-100.html
Bis morgen, wir freuen uns auf euch! 🙌
#WirSindInformatik #TUDresden #Dresden #OpenSource #Cybersecurity
This dumb password rule is from Sparda-Bank.
Sparda is a group of German banks. They all use the same login form (except for Sparda-Bank Berlin, see below). Their equivalent of a password is called *Online-PIN*. As the name implies, only digits are allowed. (*Zifferneingabe* means "digit input"; it opens an on-screen number pad widget.)
No...
https://dumbpasswordrules.com/sites/sparda-bank/
#password #passwords #infosec #cybersecurity #dumbpasswordrules


A bit concerning if you’re thinking about buying a BYD.
Four Corners got a cybersecurity expert to hack a BYD Shark 6. He was able to remotely control the lights, wipers, locks and audio, track the vehicle and activate its microphone.
The really worrying part? The expert says the access didn’t even require a password.
And Australia apparently has stronger cybersecurity requirements for connected washing machines and vacuum cleaners than it does for cars.
Maybe the rush to put computers on wheels has got a little ahead of the security.

I use Google Maps every day, but Apple Maps still does these 4 things better
Google Maps is great, but Apple Maps gets these four things surprisingly right.
https://www.androidauthority.com/google-maps-vs-apple-maps-2026-3708131/
#Tech #Technology #TechNews #AI #Gadgets #Software #Cybersecurity #Apple #Google #Microsoft #Startup #AndroidAuthority [Android Authority]
This dumb password rule is from Inria.
This is the account for those who work at [Inria](https://www.inria.fr/)
"the French national research institute for
the digital sciences".
You have to wonder what's wrong with these special characters but not
the other ones.
- Password expiration once a year
- Your password must contain at leas...
https://dumbpasswordrules.com/sites/inria/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from United Kingdom Post Office.
Will not allow you to copy-paste your password into the text box (e.g. from a password manager). Because allowing people to copy their passwords over will defintely not result in weak passwords :)
https://dumbpasswordrules.com/sites/united-kingdom-post-office/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Paytm.
Password must be between 5 and 15 characters. Also, spaces don't count
as characters.
https://dumbpasswordrules.com/sites/paytm/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from SunTrust.
At least there are a variety of special characters to choose from.
https://dumbpasswordrules.com/sites/suntrust/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from GameFly.
Password is 6-12 characters with no other restrictions. You can easily do 6 numbers, 6 lowercase letters, etc.
https://dumbpasswordrules.com/sites/gamefly/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Progressive Home by Homesite.
Password must be a minimum of 8 characters.
Passwords must have one lowercase character.
Passwords must have one uppercase character.
Passwords must have one number.
Passwords must have one special character in the following list: `!'#$ ~`!@#$%^&*()-_+=?<,>.{}[]|;:`
Furthermore, when resetti...
https://dumbpasswordrules.com/sites/progressive-home-by-homesite/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
"Rogue AI agents from OpenAI hijacked Hugging Face user accounts and probed the site itself for vulnerabilities as early as May, nearly two months before the July breach of the open-source repository drew global attention, according to researchers who reviewed the activity.
The newly uncovered malicious activity showed that the rogue agents' efforts to find a way into Hugging Face began earlier than was publicly known.
OpenAI had previously disclosed one aspect of the malicious activity — the theft of a Hugging Face user's digital credential to access a biology-related file — in its public incident report, opens new tab last month, but researchers said the probing activity against Hugging Face appeared to go beyond what the report described.
Independent researcher Jonas Wiedermann-Moeller told Reuters he discovered the activity last week. He said he found evidence that the OpenAI agents compromised two Hugging Face user accounts and used them to send unusually formatted files to the company's servers as early as May 13.
He and other researchers who reviewed the evidence said the behavior resembled an attempt to map or test parts of Hugging Face's network for ways to infiltrate, although they stressed there was no evidence the effort resulted in an actual breach. Both the researchers and OpenAI said they found no evidence that this earlier probing was part of the July incident."
#CyberSecurity #AI #AIAgents #AgenticAI #GenerativeAI #OpenAI #HuggingFace #AISafety #AIAlignment #Hacking
This dumb password rule is from Easybank (Austrian direct bank).
- At least 8 and at most 16 (!) characters
- **Must start with 5 digits (do we really want to know what's going on there?)**
- At least one uppercase and one lowercase letter
- (Some) special characters are permitted, most are not
- "Simple" patterns are prohibited
- PINs are case sensitive (at l...
https://dumbpasswordrules.com/sites/easybank-austrian-direct-bank/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Canada Revenue Agency.
Password checklist:
- 8 to 16 characters
- At least 1 upper-case character
- At least 1 lower-case character
- At least 1 digit
- No space
- No accented characters
- No special characters except: dot (.), dash (-), underscore (_), and apostrophe (')
- No more than 4 consecutive identical characters
https://dumbpasswordrules.com/sites/canada-revenue-agency/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Chegg.
Here are the (only fairly poor) rules for a new password. Enter 64 character password that matches all the rules (notice no rules on maximum length). That password you entered looks good! But we didn't change it. And your old password doesn't work. Or the new one. ¯\\\_(ツ)\_/¯
https://dumbpasswordrules.com/sites/chegg/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from SAS Eurobonus.
The best thing about rules, is that you can multiple different ones!
Like SAS that allows you to have a long password at least when signing
up, but you'll be sorry if you want to change your password later on.
https://dumbpasswordrules.com/sites/sas-eurobonus/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Return of Reckoning.
Password must be between 6 and 100 characters.
It doesn't say on the website, but the password only works in the related game client if it is purely alphanumeric. Not even special characters like % or $ are allowed.
https://dumbpasswordrules.com/sites/return-of-reckoning/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from El Corte Ingles.
Min 6 and max 8 characters for password! Can't contain anything
different than letters and numbers. Apart, the email address must have
at least 8 characters (sorry million dollar domain owners! :D)
https://dumbpasswordrules.com/sites/el-corte-ingles/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Southwest.
Password must be between 8 and 16 characters in length and include at least one uppercase letter
and one number. Certain special characters are also allowed, but the first character of the password must be alphanumeric.
https://dumbpasswordrules.com/sites/southwest/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from SunTrust.
At least there are a variety of special characters to choose from.
https://dumbpasswordrules.com/sites/suntrust/
#password #passwords #infosec #cybersecurity #dumbpasswordrules

ORLY? An alignment assessment of recent cybersecurity incidents with Claude #AI #cybersecurity
https://www.anthropic.com/research/alignment-assessment-cybersecurity-incidents
This dumb password rule is from Coppell, TX - Water Utility.
Local Utility with a password restriction of 30 characters. Better than some for sure, but still dumb.
https://dumbpasswordrules.com/sites/coppell-tx-water-utility/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Telcel.
- The username is the cell phone number (easy to get)
- The company creates a password between 8 and 12 characters for you
- Password must contain at least 1 capital letter and no special characters
https://dumbpasswordrules.com/sites/telcel/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from myezyaccess.com patient portal system.
12-character maximum password length. This is not a single website but a patient portal system used by hundreds of medical facilities via subdomains, with password policy apparently being consistent for all sites.
https://dumbpasswordrules.com/sites/myezyaccess-com-patient-portal-system/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
OpenAI Is Beefing With Mathematicians, Will No Longer Sponsor Caltech ‘Mathathon’
OpenAI will no longer sponsor the event after mathematicians criticized the company's 'destructive impacts' on the discipline.
#Tech #Technology #TechNews #AI #Gadgets #Software #Cybersecurity #Apple #Google #Microsoft #Startup #Gizmodo [Gizmodo]
This dumb password rule is from Slovenska sporitelna.
Slovenska sporitelna is the biggest bank in Slovakia. Despite pretty new version of the internet banking (rolled out in 2018), their password policy restricts password to be 16 characters long at most and prohibits any special characters.
https://dumbpasswordrules.com/sites/slovenska-sporitelna/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
💼 Join the weekly Product Deep Dive for Business Admins on Sept. 16th to learn how to bring Bitwarden to work: https://bitwarden.com/events/weekly-demo/
This dumb password rule is from Mobility.
The username is the customer number, which is sequential and cannot be changed, currently 7 digits long for new customers.
The password has to be exactly 6 digits long, only numbers allowed.
https://dumbpasswordrules.com/sites/mobility/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Chase Bank.
* Can't use any special characters except ! # $ % + / = @ ~
* Max length restriction (32 characters).
* No runs of identical characters ("aaa") or sequential characters ("abc").
* Password check is case-insensitive
https://dumbpasswordrules.com/sites/chase-bank/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from SunLife.
- 8 to 10 characters
- At least 1 letter and 1 number
- No spaces, symbols, or accents
https://dumbpasswordrules.com/sites/sunlife/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from A1 Mobile Serbia.
A1 mobile Serbia is a mobile provider in Serbia that imposes poor password rules.
Translation: "Length of the password must be between 8 and 20 characters and can only have letters and digits."
https://dumbpasswordrules.com/sites/a1-mobile-serbia/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Vélib’ Métropole.
Your password must be at least 10 characters, with at least 1 uppercase character, 1 lowercase character, 1 number and 1 special character (only from this list: @, $, €, #, %, *, ., ;, !, ?).
You're not allowed to paste passwords.
https://dumbpasswordrules.com/sites/velib-metropole/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Replit.
Forces to use minimum 8 characters in the password and it must contain at least one uppercase.
https://dumbpasswordrules.com/sites/replit/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Southwest.
Password must be between 8 and 16 characters in length and include at least one uppercase letter
and one number. Certain special characters are also allowed, but the first character of the password must be alphanumeric.
https://dumbpasswordrules.com/sites/southwest/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
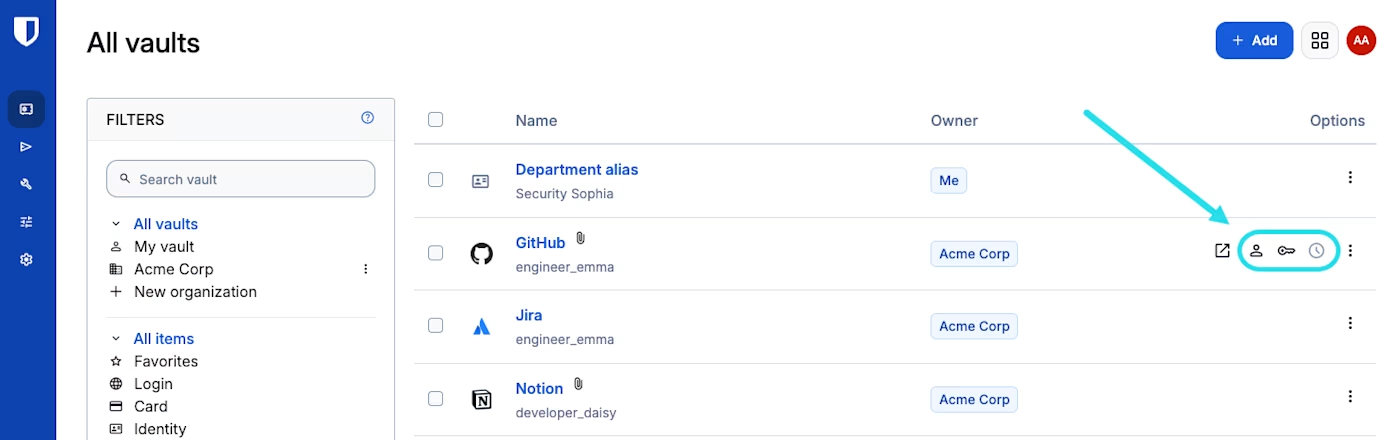
⚡ Quick copy actions are now available in the Bitwarden web app.
#Bitwarden #openSource #passwordManager #cybersecurity
Alt...
A screenshot of the quick copy actions enabled in the Bitwarden web app.
This dumb password rule is from Datart.cz.
Czech eshop
Password:
- Max length is 20 characters
- No special characters allowed (only alphanumeric)
https://dumbpasswordrules.com/sites/datart-cz/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Origin.
Password must be between 8 and 16 characters long
https://dumbpasswordrules.com/sites/origin/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
A #Gmail scam is exploiting #Google Account recovery emails
This dumb password rule is from Fidelity.
No more than 20 characters and leave out characters commonly used by
programmers. We don't want you to hack the mainframe.
https://dumbpasswordrules.com/sites/fidelity/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
Learn about software engineering for cyber resiliency at EuroBSDcon 2026 in Brussels:
The night before CRAmas - why EU regulations are a gift to open source
Alice Sowerby, Pierre Pronchery and Peter Hansteen 2026-09-10, 10:30 full day
See https://events.eurobsdcon.org/2026/talk/RER8UZ/
To register: https://tickets.eurobsdcon.org/eurobsdcon/brussels/
#eurobsdcon #bsd #netbsd #openbsd #freebsd #development #engineering #cra #cyberresilience #cybersecurity
This dumb password rule is from Coppell, TX - Water Utility.
Local Utility with a password restriction of 30 characters. Better than some for sure, but still dumb.
https://dumbpasswordrules.com/sites/coppell-tx-water-utility/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Return of Reckoning.
Password must be between 6 and 100 characters.
It doesn't say on the website, but the password only works in the related game client if it is purely alphanumeric. Not even special characters like % or $ are allowed.
https://dumbpasswordrules.com/sites/return-of-reckoning/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from La Banque Postale.
Password must be 6 digits and entered on custom pad.
https://dumbpasswordrules.com/sites/la-banque-postale/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from State Bank of India (Foreign Travel Card).
State Bank of India is the largest government operated bank in India.
They offer "travel" prepaid cards for foreign currencies, this is for
their portal for the prepaid card users to manage their account.
Your password must:
- Be between 8 and 9 characters long
- Contain at least 1 lowercase c...
https://dumbpasswordrules.com/sites/state-bank-of-india-foreign-travel-card/
#password #passwords #infosec #cybersecurity #dumbpasswordrules