Search results for tag #security
KeePassXC 2.8.0 is out.
The update finishes off the port to Qt6, and adds Quick Unlock, AppImage buffs and long-awaited support for auto-type on Wayland.
https://www.omgubuntu.co.uk/2026/10/keepassxc-2-8-auto-type-wayland?v1
Steam Client update fixes Vulkan games hanging after alt-tab, and a security update https://www.gamingonlinux.com/2026/10/steam-client-update-fixes-vulkan-games-hanging-after-alt-tab-and-a-security-update/

Both home services that use PHP have thankfully received upstream image patches. They’ll be updated and started automatically in the wee hours.
Today's PHP Security Release, and How We're Strengthening PHP Security (PHP Foundation)
🔒 Kitten Security update
I just released a Kitten hotfix that upgrades the Kitten runtime to today’s Node 24.22.1 with a number of critical security fixes, including the eMudhra fix.
All Kitten production servers will automatically update within the next six hours if you do nothing.
If you want to upgrade your servers sooner, like I just did, sign in to your Settings panel and use the manual upgrade feature.
In response to the eMudhra / emSign certificate security incident we've published guidance for Python users to update CA certificates: https://discuss.python.org/t/information-for-python-users-regarding-emudhra-emsign-ca-certificate-security-incident/109576

Expect quite a few sites to return error pages today and possibly through the week. Here's my piece on the new PHP zero-day that affects about 70 percent of the Internet. We'll be updating the story with important new developments.
https://krebsonsecurity.com/2026/10/widespread-php-flaw-may-cause-many-site-outages-today/
Alt...
A Shutterstock photo showing a computer screen from the side. The screen background is dark blue, and the text is light blue. The text is HTML and PHP code.

Shall we switch off all of our #movim, #nextcloud, and #wordpress instances right now until a new #PHP is available in the #Debian #security suite?
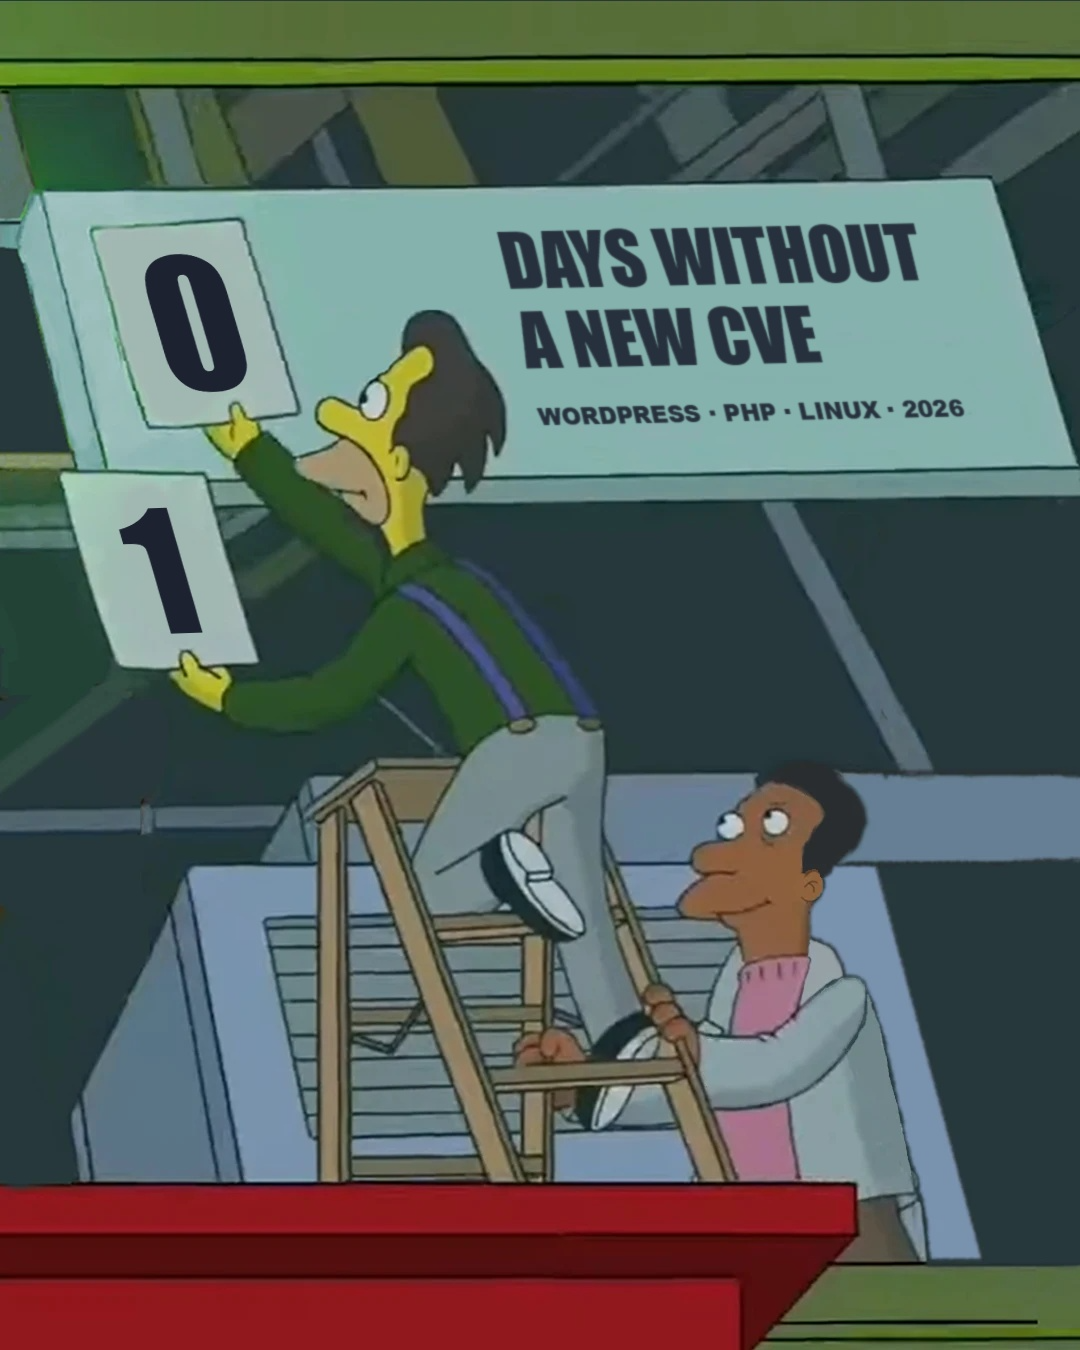

High-severity vulnerability in PHP. No patch yet. It’s coming (see @php). It’s recommended to simply shutdown your PHP applications until the patches land (as it involves remote code execution).
#php #security https://fosstodon.org/@php/117474977977509509
🚨 A heads-up for anyone running #WordPress, #Moodle, #Nextcloud or other PHP-based services.
PHP has confirmed two critical vulnerabilities, both rated 9.2/10. Fixes are scheduled for today, 21 October, at 14:00 UTC.
Prepare to patch PHP, not just your applications. CERT-EU advises considering temporary isolation of public-facing services if prompt patching isn't possible.
It sounds pretty bad. Affected versions are not yet confirmed but I've heard 5.4+

We are shipping an immediate #security update for our CA store shortly. We recommend updating once those evaluations complete and the channels have advanced.
The small channels (#NixOS only) are ongoing and will be finished within the hour. The big channels (#NixOS/#Nixpkgs) will unfortunately take a while longer.
https://hydra.nixos.org/eval/1830475 26.05-small
https://hydra.nixos.org/eval/1830473 unstable-small
October is #CybersecurityAwarenessMonth. Let's spread #Privacy & #Security together. 💪
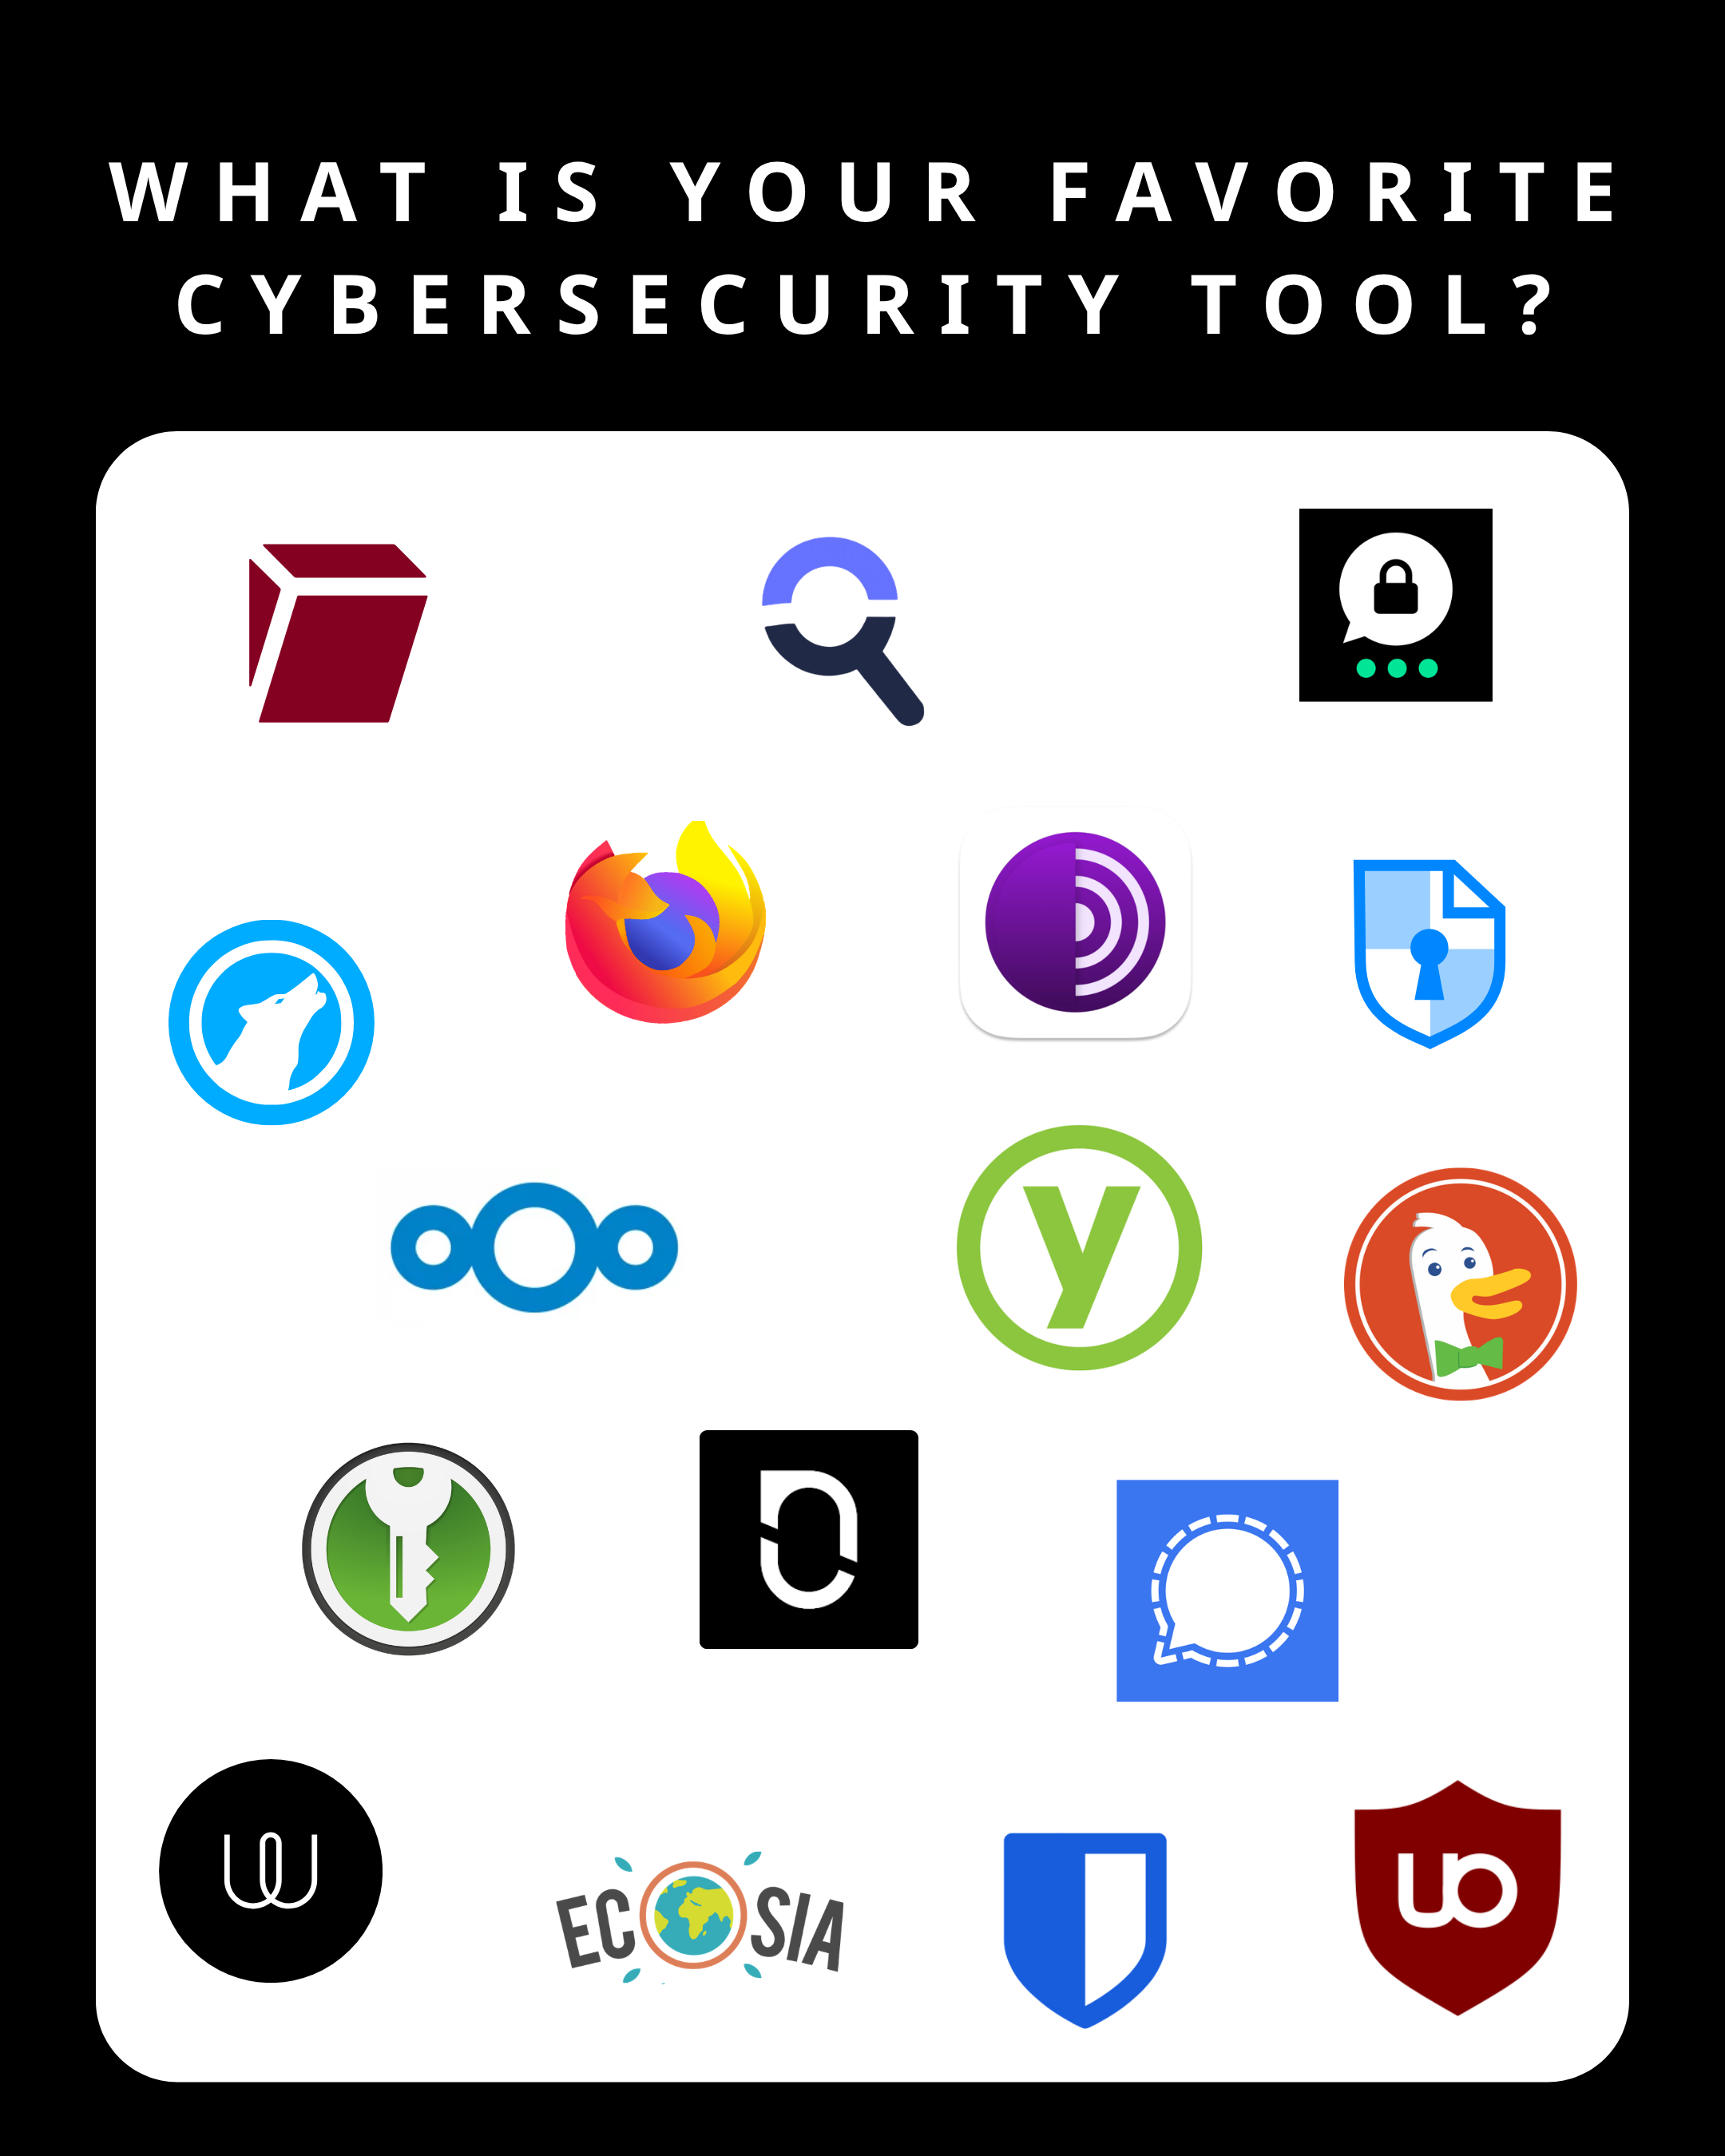
Let us know what your favourite cybersecurity tool is in the comments.
@firefox @torproject @yubico @duckduckgo @signalapp @bitwarden @ecosia @nextcloud @StartpageSearch @ublockorigin
Alt...
App icons of different tools: Tuta, StartPage, Threema, Librewolf, Tor Browser, Cryptpad, Nextcloud, Yubico, DuckDuckGo, KeePassCX, Notesnook, Signal, Wire, Ecosia, Bitwarden, uBlockOrigin.
Happy OpenBSD 8.0 release day to all who celebrate!
https://undeadly.org/cgi?action=article;sid=20261020021401 + https://www.openbsd.org/80.html
#openbsd #newrelease #development #security #networking #freesoftware #libresoftware
Now that the new release is out, "You Have Installed OpenBSD. Now For The Daily Tasks." https://nxdomain.no/~peter/openbsd_installed_now_for_the_daily_tasks.html (or tracked https://bsdly.blogspot.com/2024/09/you-have-installed-openbsd-now-for.html) has been updated (version numbers incremented) #openbsd #installing #maintaining #freesoftware #libresoftware #security #developement
These stories always both amuse and horrify me. Memory stick supply problem? Sure just send a squaddie out to the local market. What could be the harm? It was more difficult to bring a US-based computer into the nation than it was just to buy local,” he said. “So they were just going out into the local market in Kabul or whatever city that they were out. And I used to do this: go out, make relationships with the local vendors. ‘Hey I need 100 USB sticks.’”
With a fresh OpenBSD release just around the corner, this may be a good time to reprise my 2021 article "What every IT person needs to know about OpenBSD" https://nxdomain.no/~peter/what_every_it_person_needs_to_know_about_openbsd.html (also available in smaller chunks at apnic.net) #openbsd #security #networking #development #freesoftware #libresoftware
#MPs from all political parties (left and right wing) in #EastAnglia report feeling unsafe and in many cases actual #attacks and #security incidents..
This is likely worse than the 1990s/00s but a similar level of danger to that MPs experienced in the 20th and previous centuries..
https://www.itv.com/news/anglia/2026-10-15/exclusive-survey-reveals-mps-still-facing-death-threats

🚀 Defguard 2.2.0-beta1 is out!
🆕 Test now:
- Multi-step MFA flows per location
- FIDO2 hardware keys as MFA factor
- MFA setup in the desktop client
- Firewall bulk actions
- Redesigned mobile client
Not for production yet, great for testing.
👉 https://defguard.net/releases/2.2.0-beta-1/notes/
#vpn #sysadmin #devops #selfhosted #SelfHosting #wireguard #OpenSource #release #security #privacy #homeLab #anonymity #floss #docker #CyberSecurity #InfoSec #OnlinePrivacy #DataProtection #InternetSecurity #NetworkSecurity
Alt...
WireGuard Hardware Keys/FIDO2 MFA/2FA

Concerning read on the surveillance capabilities and security/privacy risks of Muse, the latest product from Meta. Particularly disturbing is how much information it can gather even if you have not given it permission or access - via contacts who have done so.
https://paulfwalsh.substack.com/p/metas-muse-ai-agent-is-a-commercial