Search results for tag #cybersecurity

This dumb password rule is from EllieMae Access.
Must reset password every 6 months and password requirements are not displayed _anywhere_.
Reset uses a Security Question, and you have to choose from a list of 5.
https://dumbpasswordrules.com/sites/elliemae-access/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
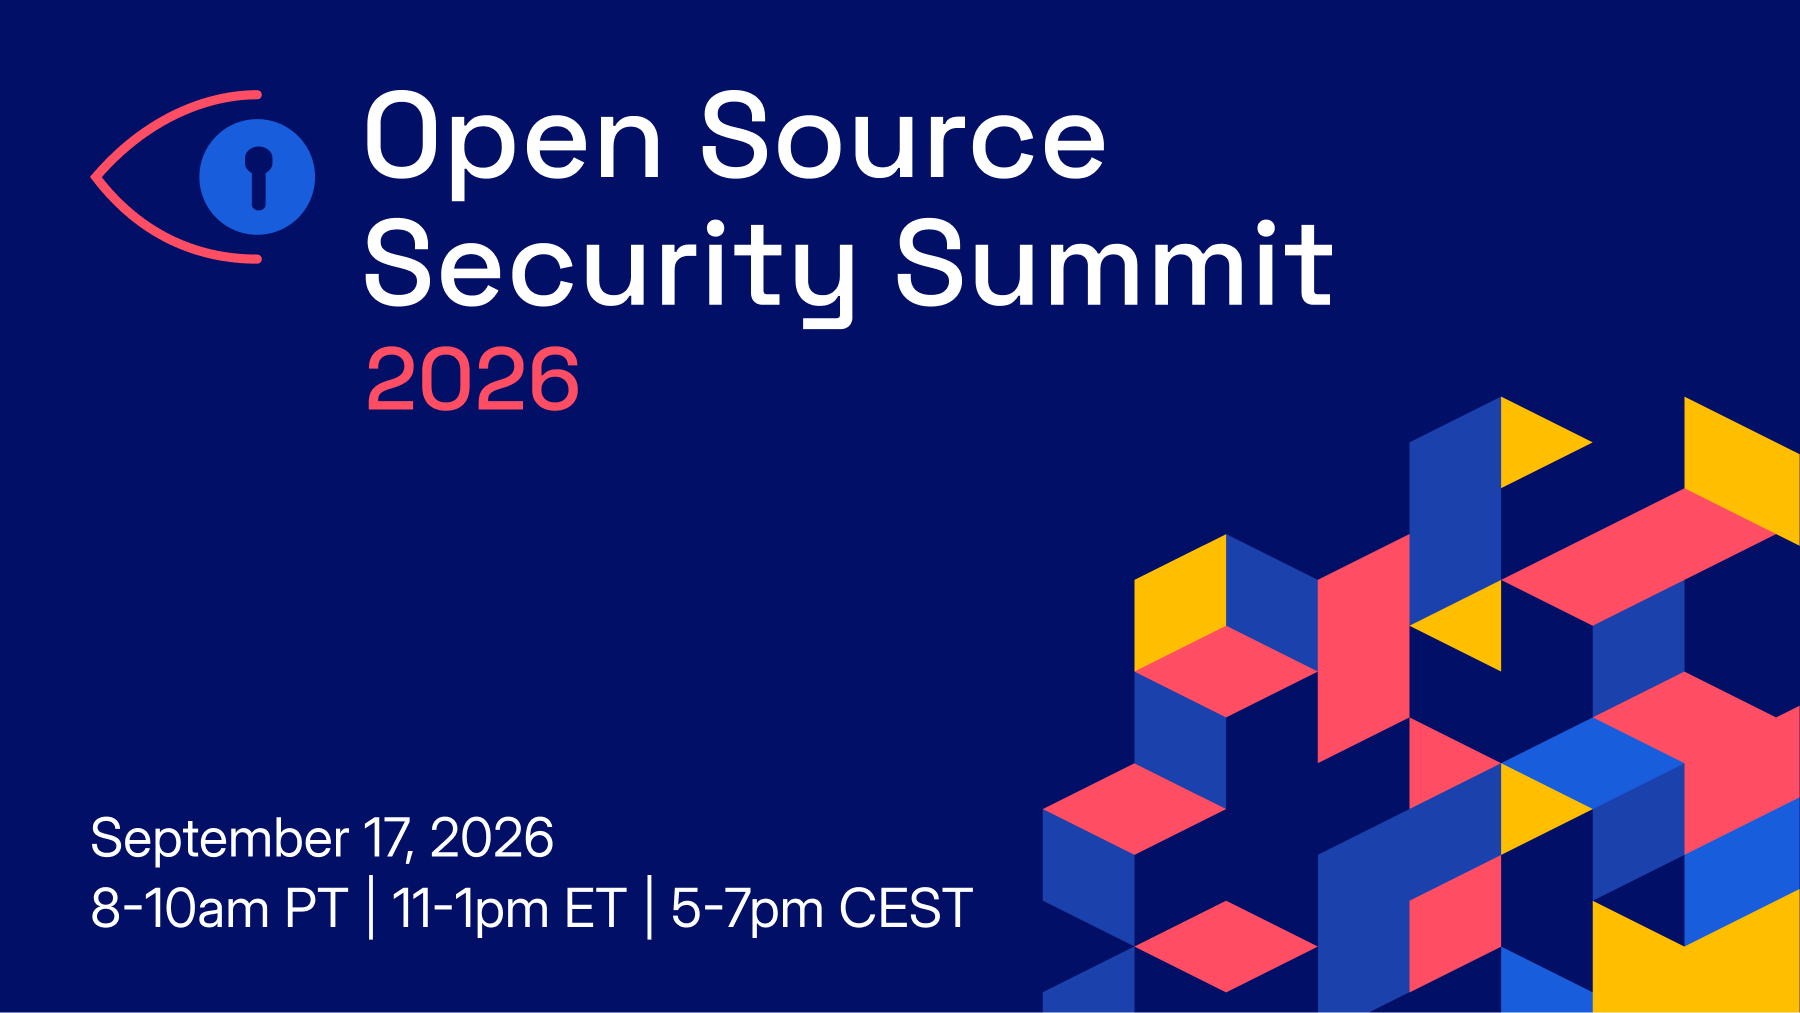
Have you saved your seat for the 7th annual Open Source Security Summit?
https://opensourcesecuritysummit.com/
Alt...
Social graphic for the 2026 Open Source Security Summit, September 17, 2026, 8-10am PT, 11-1 PM ET, 5-7 PM CEST
Scary retelling of the OpenAI/Huggingface incident,
https://www.dwarkesh.com/p/openai-huggingface
#ai #huggingface #openai #cybersecurity
This dumb password rule is from HDFC Bank.
Only a maximum of 15 characters and some special characters are not allowed.
https://dumbpasswordrules.com/sites/hdfc-bank/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from BMW ConnectedDrive.
Although the prompt suggests good things, after many failed attempts to
set a new password, it turns out you can ONLY use the special characters
shown in the prompt
https://dumbpasswordrules.com/sites/bmw-connecteddrive/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from SunTrust.
At least there are a variety of special characters to choose from.
https://dumbpasswordrules.com/sites/suntrust/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Lenovo.
- **Between 8 and 20 characters, not more.**
- 1 alphabetic letter
- 1 number (0-9)
- **1 symbol ($!#&)**
https://dumbpasswordrules.com/sites/lenovo/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Eurocircuits.
Minimum 4 and maximum 30 chars. Use only letters (a-z), numbers (0-9) and underscore (_)
https://dumbpasswordrules.com/sites/eurocircuits/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Dwr Cymru (Welsh Water).
Limits password length to a maximum of 16 characters
https://dumbpasswordrules.com/sites/dwr-cymru-welsh-water/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Very.co.uk.
Password field allows *only* the listed Special Characters ($ . , ! % ^ \*).
You're also forced to use both upper, and lower letters, as well as a number.
https://dumbpasswordrules.com/sites/very-co-uk/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from GoDaddy SFTP.
Max 14 characters for the most important password in your shared hosting environment.
https://dumbpasswordrules.com/sites/godaddy-sftp/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Raiffeisen Bank Serbia.
There are a couple of password limitations when creating a new account (and
changing existing password) on Raiffeisen Bank Serbia on-line banking portal.
Password length is limited to minimum 8 and maximum 32 characters. Also, minimum
uppercase letters 1, minimum lowercase letter 1, minimum digit...
https://dumbpasswordrules.com/sites/raiffeisen-bank-serbia/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from HDFC Bank.
Only a maximum of 15 characters and some special characters are not allowed.
https://dumbpasswordrules.com/sites/hdfc-bank/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from NordVPN.
- Password cannot be longer than 48 characters.
https://dumbpasswordrules.com/sites/nordvpn/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from CAF (French Family Allowance Fund).
You have to enter your 8-digit password using this Frenchy keypad.
https://dumbpasswordrules.com/sites/caf-french-family-allowance-fund/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
Bitwarden Password Manager almost doubled their price...? 💵 🤔
I do not remember a notification...? 🧾 🤔
Hmmm... 🤔 🤨
[EDIT] ➡️ People have since sent Me a link:
https://itsfoss.com/news/bitwarden-quiet-changes/
#bitwarden #password #passwordmanager #cybersecurity #security
This dumb password rule is from NVV (Nordhessische VerkehrsVerbund).
Password length must be 4 to 10 characters with only a few special characters allowed.
https://dumbpasswordrules.com/sites/nvv-nordhessische-verkehrsverbund/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Itaú Bank.
I know, it's in spanish, let me translate this monstrosity for you.
- Allowed characters: letters A to Z uppercase or lowercase (ñ is not allowed), number 0 to 9, #, $, %, &, +, -, . :, ;, _.
- You must use 8 characters.
- The password must contain at least one letter and at least one number.
- ...
https://dumbpasswordrules.com/sites/itau-bank/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
If this sale goes through, I for one will move all my banking and investments to a bank not involved with this. #Canada needs to become less entangled with US ownership. The timing of this is very concerning. Do read this article. If you also will move your accounts, be public about it.
What will you do?
#RBC #BMO #banking #digitalsovereignty #security #cybersecurity #buyCanadian
https://www.cbc.ca/news/politics/moneris-deal-canadian-digital-sovereignty-9.7304962
This dumb password rule is from E-Redes.
Portuguese power distribution company, which requires short passwords (10 to 15 characters), no repetition of the same character, not using the username, the word "PASS" or the word "SAP" in the password, and limiting which special characters can be used.
https://dumbpasswordrules.com/sites/e-redes/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Intel.
https://dumbpasswordrules.com/sites/intel/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
Encryption keeps us safe and secure online.
A backdoor is only possible by breaking encryption. And then anybody can abuse that cybersecurity weakness.
The government's last attempt to force Apple to build a backdoor into our accounts failed.
We'll fight the latest order.
Find out more ⬇️
#encryption #e2ee #privacy #cybersecurity #apple #surveillance #ukpolitics #ukpol
Shadowy attempts to break our right to privacy are completely rejected:
⚫️ Only 12% believe the government should be able to issue secret orders to gain access to private data.
⚫️ 87% believe there should be a legal obligation to tell people if their private conversations have been accessed.
#encryption #e2ee #privacy #cybersecurity #apple #surveillance #ukpolitics #ukpol
The UK government is trying yet again to ram a backdoor into Apple's encrypted products.
But you ask the UK public and over 90% say they should have a right to private conversations online.
New polling by the Center for Democracy & Technology makes it clear that attacks on encryption aren't backed by public opinion.
Read more ⬇️
#encryption #e2ee #privacy #cybersecurity #apple #surveillance #ukpolitics #ukpol
This dumb password rule is from Zurich.
Password must be EXACTLY 8 characters long.
Alpha numeric characters ONLY.
The first character must be alphabetic.
NO spaces.
The new Password cannot be the same as the last 32 passwords you have used. (they actually store your last 32 passwords)
https://dumbpasswordrules.com/sites/zurich/
#password #passwords #infosec #cybersecurity #dumbpasswordrules

Today's story is the result of an ungodly amount of research, and I am very glad to finally be able to share it with you.
Authorities in Australia have arrested two men believed to be members of TeamPCP, a prolific cybercrime and data extortion group blamed for perpetrating the longest running spree of software supply chain attacks ever.
In a statement released today, the Australian Federal Police (AFP) said two unnamed suspects from Western Australia, aged 21 and 23, were arrested in connection with a “sophisticated cybercrime syndicate that allegedly created malicious open-source software to rob thousands of global businesses.”
The AFP did not name the defendants, but KrebsOnSecurity learned the 21-year-old suspect’s real identity in June, and has been communicating with him ever since. This story includes interviews with TeamPCP’s self-described spokesperson, and examines clues left behind by the TeamPCP leader that likely led to his undoing.
https://krebsonsecurity.com/2026/08/two-alleged-teampcp-hackers-arrested-in-australia/
This dumb password rule is from Polytechnique Montreal.
Passwords must have a minimum length of 8 characters
Passwords must have a maximum length of 30 characters
Passwords must contain a minimum of 2 digits
Passwords must contain a minimum of 2 letters
Password must be different than the last one used
Passwords may contain these special characte...
https://dumbpasswordrules.com/sites/polytechnique-montreal/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from University of Windsor.
The password policy applies to alumni as well. Must be at least 10
characters long, with at least 1 upper case and 1 lower case
character, at least 1 number, at least 1 special character. Password
expires every 120 days, and you can't reuse an old one.
https://dumbpasswordrules.com/sites/university-of-windsor/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
Hello friends, I've seen the below image come up a few times elsewhere and am going to expound a little!
While the hyperlinks in the image display correctly, those aren't actually the addresses of those sites! Instead, they're the Internationalized Domain Name replacements - examples of what are called IDN Homograph Attacks.
It's incredibly hard to include all characters from all active alphabets in the mechanisms that resolve domain names - so currently that letter set is restricted, and instead uses a translation system called Punycode to move between a visual URL with the correct characters and a domain name your computer can actually resolve to a website.
So while neurovagrant[.]com is fine either way, nӘ̃urovagrant[.]com isn't! The actually domain would be xn--nurovagrant-rkg322d[.]com.
Notice that xn-- ! That's what tells browsers and other software that it's an IDN domain, and to try and translate it.
Attackers use this to their benefit. So:
xn--mcrosoft-security-teams-1ec[.]com can appear in your email, on your twitter feed, in other places visually as: mícrosoft-security-teams[.]com
You may think you're signing in to check your retirement at vanguarɗ[.]com but it's actually sent you to xn--vanguar-4cd[.]com
A link that appears as vḙnmo[.]com actually sends you to the website xn--vnmo-q64a[.]com
They even target kids! Take a look at xn--rblox-jua[.]com - which looks like röblox[.]com in most settings. Note the diacritical mark above the first o.
If anything looks off, there's a reason. Always view links with skepticism, don't click on things unnecessarily, and always sign into the sites you use by going to the domain name you know.
Stay frosty out there, friends.
#cybersecurity #infosec #StayFrosty

Alt...
Screenshot that says "Spot the difference" and shows two different maybank and citibank addresses - one that is legitimate, and one that uses a cyrillic 'a' to send you to an illegitimate site.
This dumb password rule is from Munich Foerdermittel Portal.
You register on their funding portal and receive an email with an activation link to set a password.
The email further informs you about their password policy:
- At least 8, but no more than 20 characters
- At least one lowercase and uppercase letter
- At least two digits (1,2,3,4,5,6,7,8,9,0) or...
https://dumbpasswordrules.com/sites/munich-foerdermittel-portal/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Jaa Lifestyle.
When we try to change password and accidentally gave a wrong password for confirm password.
Lets try to read and figure out what they are trying to point out.
https://dumbpasswordrules.com/sites/jaa-lifestyle/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Sephora.
Password must be between 6 and 12 characters. No other rules
specified.
https://dumbpasswordrules.com/sites/sephora/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from KPMG Talent Community.
While stating otherwise, the site actually *accepts a backslash* in the password
and displays a forward slash as the example of the disallowed backslash
Password:
- Must be at least 8 characters long
- Must contain at least 1 number
- Must contain at least 1 letter
- Must contain at least 1 spec...
https://dumbpasswordrules.com/sites/kpmg-talent-community/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Sparkasse.
„Sparkasse“ is a group of banks which is pretty popular in Germany. It
calls its passwords „PIN“ („persönliche Identifikations-Nummer“ —
personal identification number), the rules are pretty horrific and its
not even a number, even though it is called as such! Here is a
screenshot from the branch...
https://dumbpasswordrules.com/sites/sparkasse/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
Iranian hackers shut down UK power plant last month in an unprecedented cyber attack. The attack, believed to be the most successful cyber attack of its kind, took place at the same time as a series of attacks on US water infrastructure, which affected 12 states.
https://www.bbc.com/news/articles/ce9793g34yvo
#cybersecurity #cybercrime #geopolitics #Iran
This dumb password rule is from Easyjet.
No more than 20 characters, use any symbols you like... Oh except #, &, +, or space of course.
https://dumbpasswordrules.com/sites/easyjet/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from LINE.
Password must:
- be between 8 to 20 characters
- not contain characters that repeat in a row
Password must contain three of the following:
- an upper-case letter
- a lower-case letter
- a number
- a symbol
https://dumbpasswordrules.com/sites/line/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Replit.
Forces to use minimum 8 characters in the password and it must contain at least one uppercase.
https://dumbpasswordrules.com/sites/replit/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
 Michael T Babcock [https://en.pronouns.page/@bigntallmike] » 🌐
@mikebabcock@floss.social
Please use open source systems whenever possible so you can review the source code. Encourage vendors you work with to stop keeping their software hidden so it can be audited.
Slovakia discovers Russian backdoors in 279 new traffic cameras — SMS-triggered shell access and passwordless live feeds found in EU-funded rollout | Tom's Hardware
https://www.tomshardware.com/tech-industry/cyber-security/slovakia-discovers-russian-backdoors-in-279-new-traffic-cameras-national-security-service-deactivates-offending-units
For those who can read the original:
https://www.sk-cert.sk/sk/varovanie-pred-rizikami-cestnych-meradiel/index.html