Search results for tag #security
I love my fairphone, in case you are considering one. Daily driver in the US and while traveling. Murena is a/the? US distributor.
I'm not affiliated with either, but this was my choice to move away from/off oligarch technology.
#repairability #antioligarchy #opensource #security
its good wider community (mostly older folk/seniors?) came out in support after this Islamic Centre in #Cornwall was attacked (including funding upgraded #CCTV and #security equipment!) but offenders need to be caught
After ramming gates, they poured used engine oil around the grounds from what appears to be a 20/25 litre container + maybe a smaller 5l one.
Not stuff you generally have lying around, unless you do your own oil changes or work in a repair garage!
Also to bust the gates they needed access to a large vehicle they didn't mind putting a few (more?) dents/cracks in the bumper, suggesting lads from local rural community (building not obviously Islamic from outside) with an interest in vehicles (but also with history of reckless driving)

...
- #Surveillance
- Controlling content we see
- Making unaccountable life-changing decisions
The #Labour manifesto promised it would regulate AI. But #Starmer succumbed to pressure from #BigTech and pursued ‘growth’ over our rights
It’s time for our new Prime Minister & Minister for AI, Narayan, to introduce legislation that will #regulate AI and ensure that works for all of us and does not harm our #HumanRights
https://action.openrightsgroup.org/tell-andy-burnham-regulate-ai
#safety #security #privacy #DigitalAlert
[2/2]
EuroBSDCon 2026 talks online https://undeadly.org/cgi?action=article;sid=20260916093106 #openbsd #eurobsdcon #conference #development #security
Adamsdesk Bans Font Squirrel Over Privacy Concerns?
Find out what lead to the discovery of privacy concerns, complications whether to ban linking to certain websites and what decision was made.
https://www.adamsdesk.com/posts/font-squirrel-privacy-concern/
#blog #privacy #security #tech #technology
Alt...
A squirrel sitting in an opening covered in grass with a row of tall trees stand in the background around bushes. Above is bold title that reads, 'Adamsdesk Bans Font Squirrel?' with a red no symbol over top of the squirrel.
Security through obscurity - the last days
The traditional approach to ‘if no one knows then they won’t find out’ that has been adopted by many companies and organisations to protect their systems is finally on it’s way out - and in part we have AI attacks to thank for it.

We had a big wave of automated Mastodon signups with very predictable usernames.
I first tried the sledgehammer approach and blocked known VPN ranges at the firewall.
It (partially) worked.
It also blocked legitimate ProtonVPN users. 😬
So I replaced that with a tiny custom Mastodon validator that rejects the actual abusive username pattern instead.
Much cleaner: block the abuse, not the transport.
How-to + code:
https://gist.github.com/chofstede/a422427570004719196cde948521dd04
#Mastodon #Mastoadmin #Fediverse #SysAdmin #Ruby #Rails #Security @tux @AlienJay @aping
The "Vaults" folder encryption app (https://flathub.org/apps/io.github.mpobaschnig.Vaults) is a very cool concept, I think it would benefit from being more widely discovered (keywords may help: https://github.com/mpobaschnig/vaults/issues/195)
I wonder what I could use it for, in a future where GNOME OS will provide per-user home directory encryption out of the box with #systemd, and Pika Backups already has encryption.
Anyone using Vaults (or similar) for something interesting?
#encryption #gocryptfs #CryFS #infosec #security #Linux #GNOMEOS


Imagine you're having a remote appointment with your doctor for a very personal health issue.
Your doctor is a tech enthusiast, and is proudly wearing the new Apple Watch with all the recording features enabled.
You don't see the "Audible and visible signals for Live Rewind", because you don't see your doctor's wrist on videochat or on speakerphone.
The "Omitted content" safeguard fails to detect the sensitive conversation, because none of the pre-selected keywords are detected.
"What about all the privacy laws protecting me?", you claim in distress.
Sadly, your doctor is unaware and thinks "surely Apple respects all the laws by default?"
The medical clinic isn't informed about privacy risks related to new technologies, and hasn't implemented any training or policies about it yet.
Your sensitive health data is collected by Apple's new features, stored on their servers, blissfully unaware of the infringements to your consent, your privacy, and all the laws supposed to protect you.
This is only one scenario of the many surveillance nightmares we might hear about in the coming months and years.
Brace yourself.
The Open Source Security Summit is less than a week away! Featuring insights on cyber policy and geopolitics, the ethics and culture shaping the #security community, and more, this free virtual event is one you won’t want to miss.
Save your spot now: https://bitwarden.com/open-source-security-summit/

The #ColdWar is over. " #PaxAmericana" is over
It's regional powers abusing their neighbors now
#Ukraine, #Georgia etc near #Russia
#Canada, #Venezuela etc near #USA
#Taiwan, #Philippines etc near #China
Here's an amazing bit of #diplomacy #drama on the point
Philippine #Defense Secretary #GilbertoTeodoro at a #SouthKorea #security forum is handed a note apparently from a Chinese #military attaché
And ad libs this witty, dignified reaction
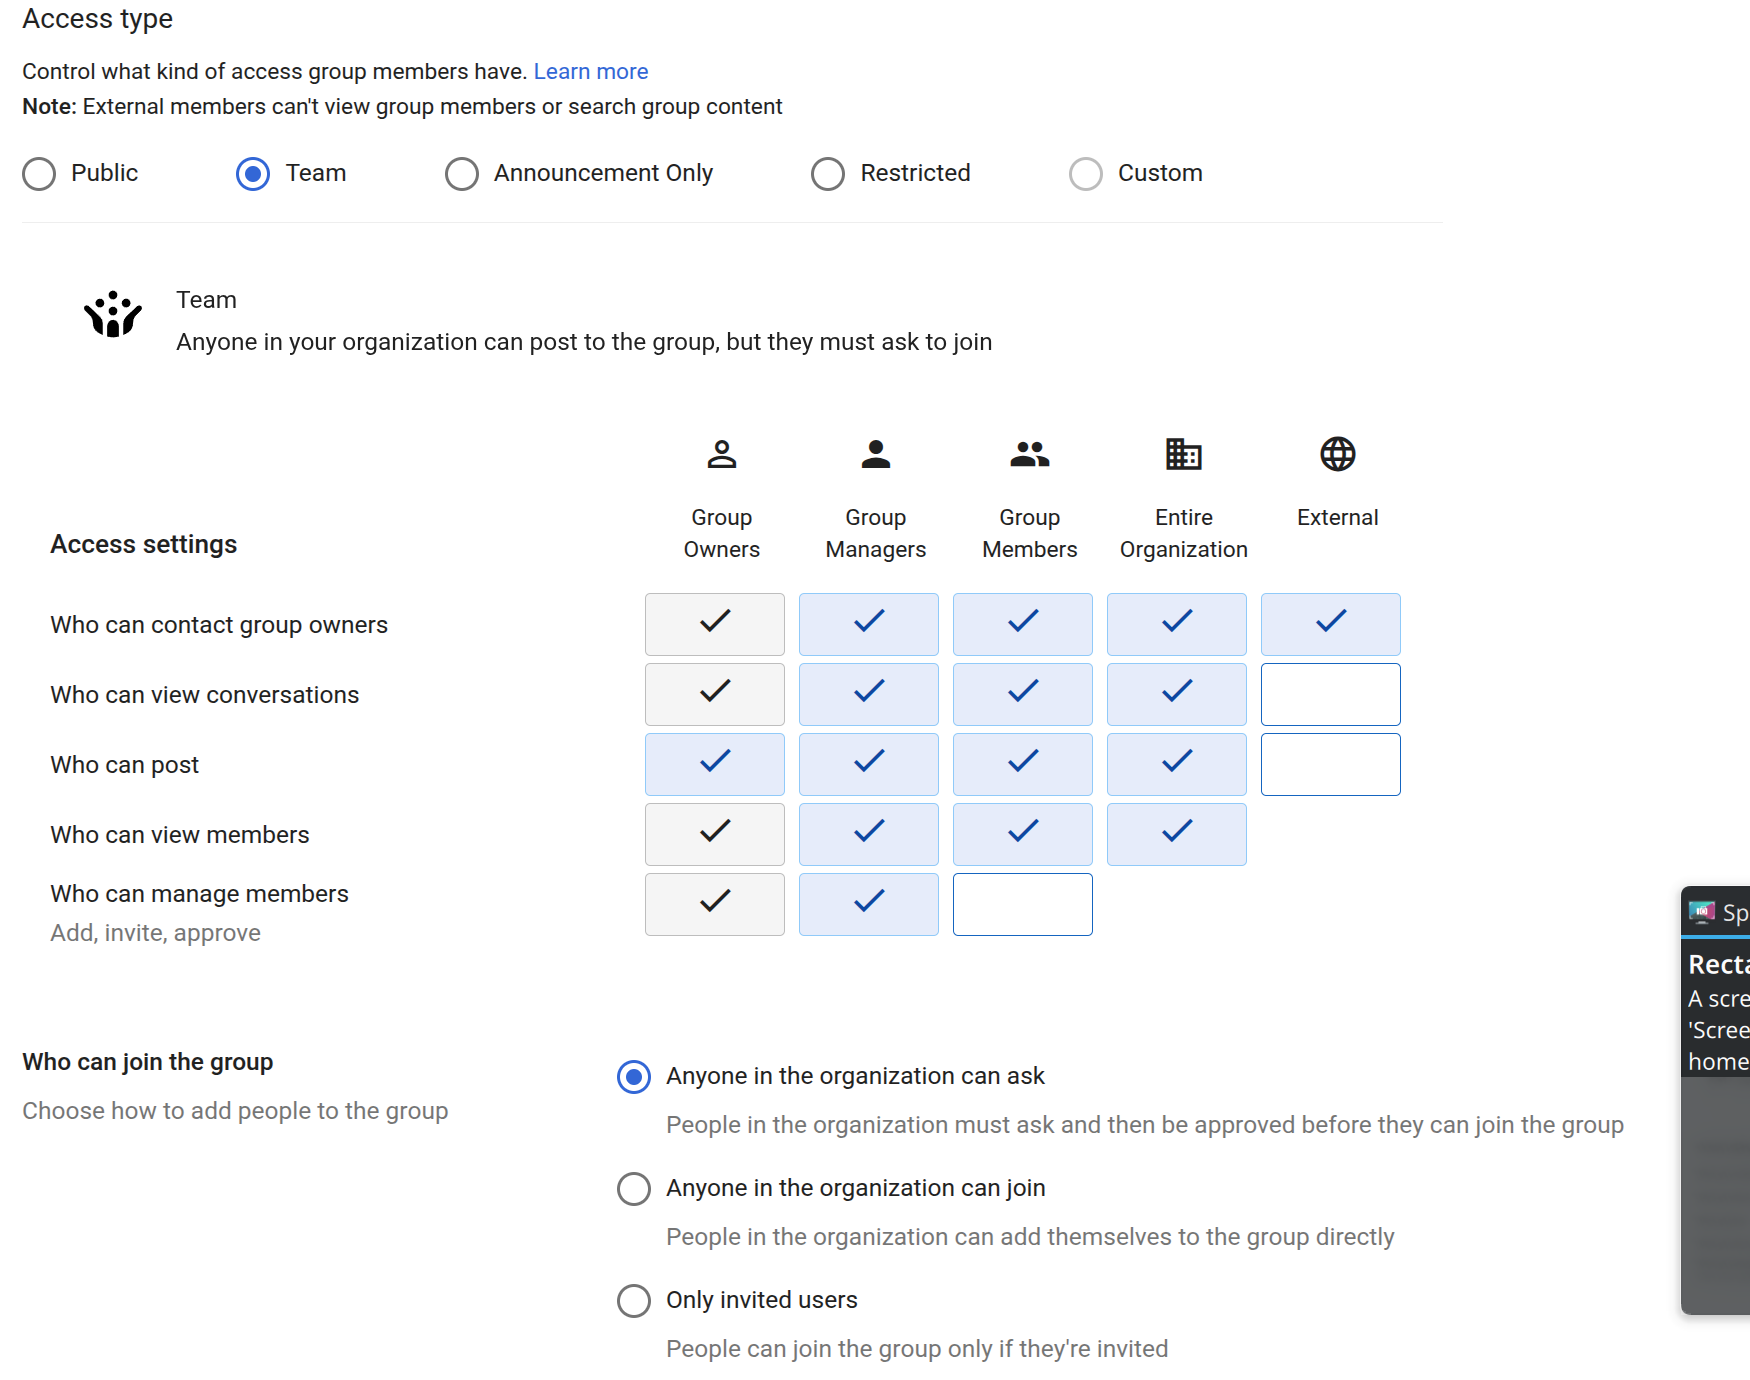
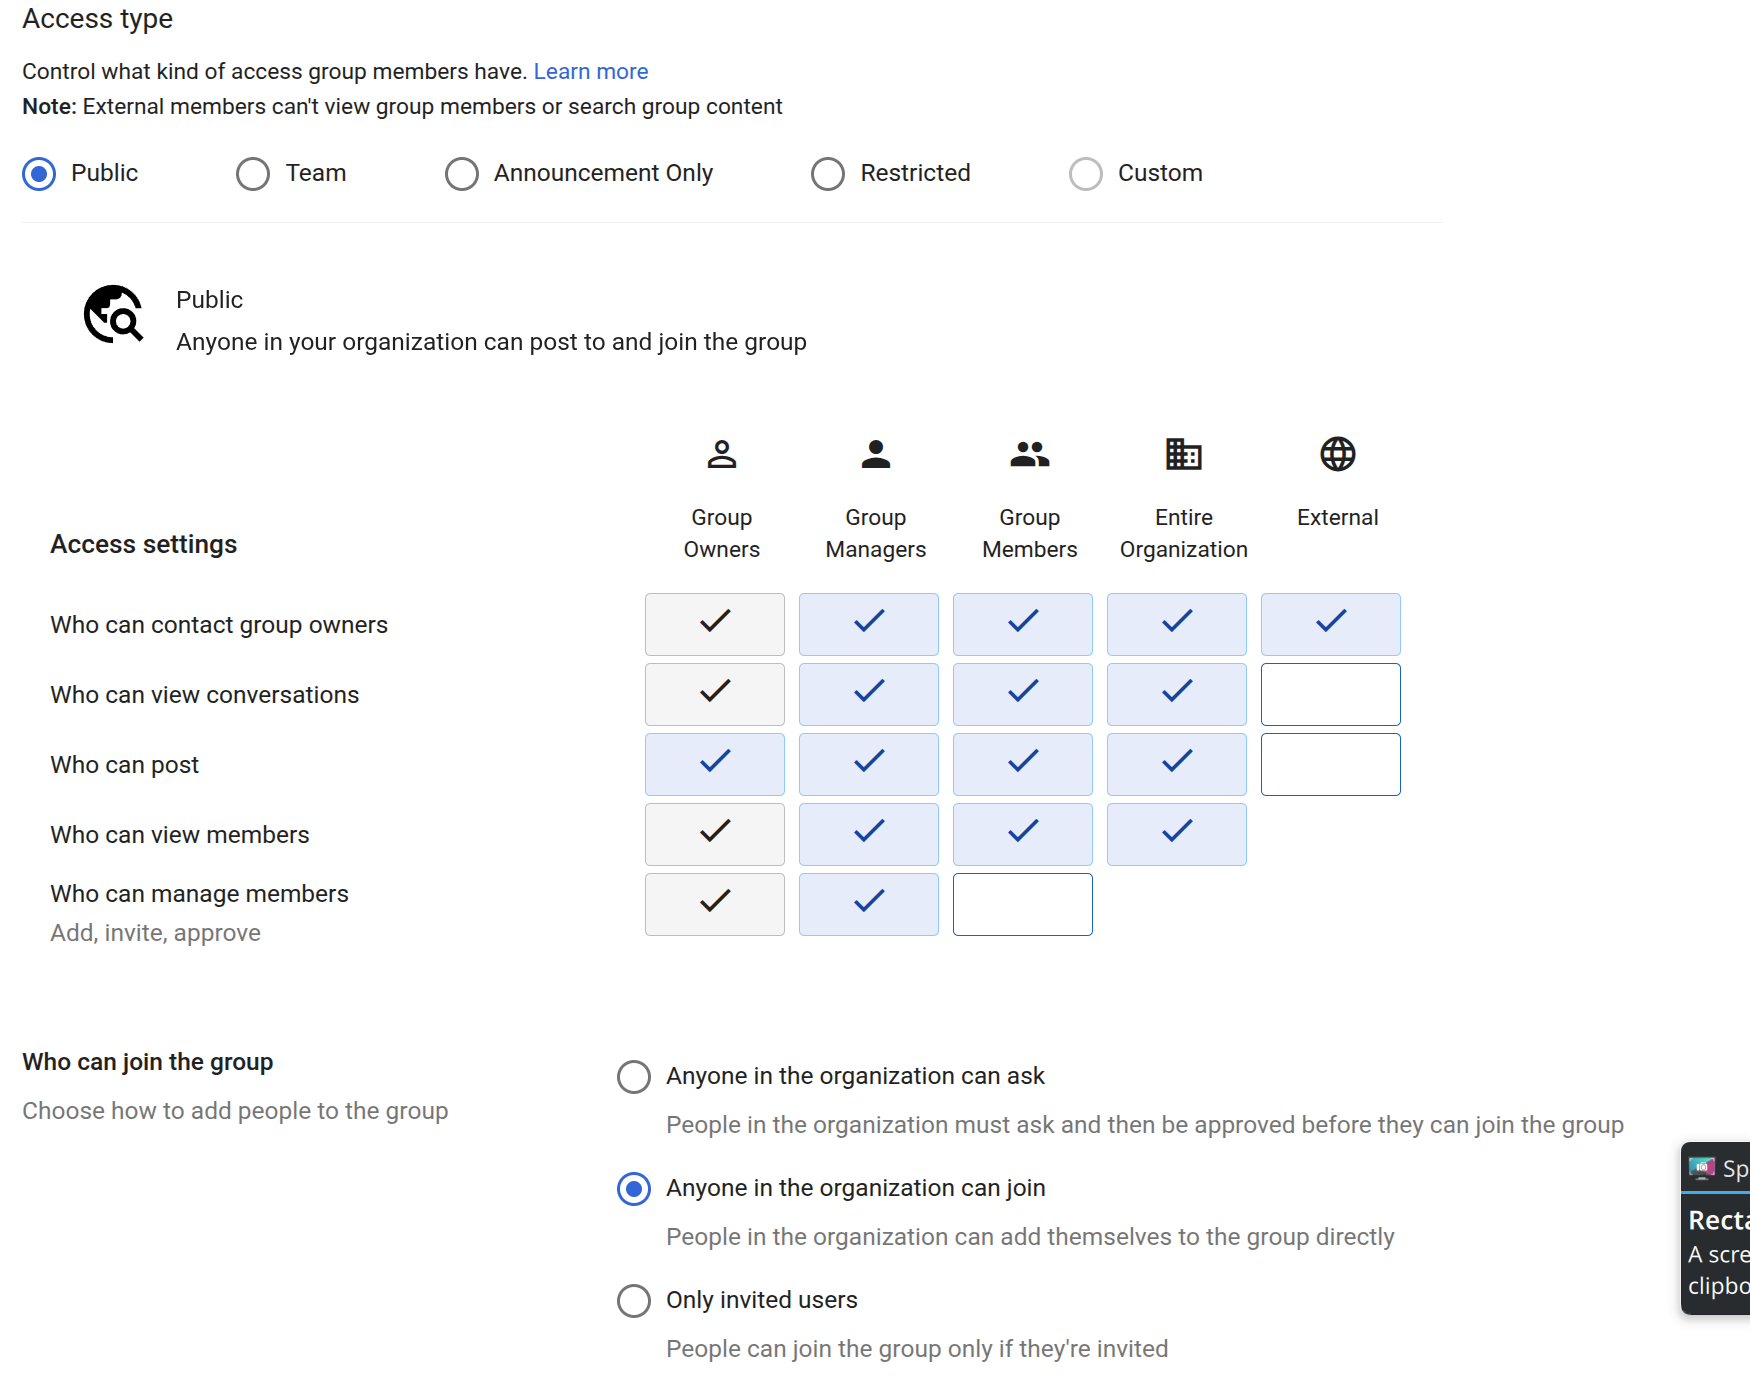
I've had admin powers at 5+ companies' Google Workspace/G Suite over the past decade or so. Every single one had groups which were misconfigured, often so anyone in the whole company could join without approval or see the message history at https://groups.google.com without being a member at all.
This is because for any sensible configuration of Google Groups when using it for email groups you have to use the "Custom" permissions mode. The default Public mode doesn't allow external people to email the group, but does allow the whole company to see all the messages. The default Team mode, has the same problem of everyone being able to see all the messages.
Also let's not forget that dangerous little "Anyone in the organisation can join" toggle at the bottom which is on by default. So any random new starter can join your confidential company directors group and get all the emails sent to it.
Giving Google the benefit of the doubt here, I think the reasoning might be that Google Groups is intended as a kind of company forum, not for private email groups. However that isn't how anyone uses it in my experience...
#security #infosec #google #googleworkspace
Alt...
Screenshot of the default Google Group settings for team mode
Alt...
Screenshot of the default Google Group settings for public mode