Search results for tag #infosec

This dumb password rule is from ADP.
Forced to change the password during the first login. At least they
could use proper grammar in their rule list.
https://dumbpasswordrules.com/sites/adp/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Apple.
Can't contain 3 or more consecutive identical characters, nor can it be more than 63 characters long.
https://dumbpasswordrules.com/sites/apple/
#password #passwords #infosec #cybersecurity #dumbpasswordrules

This dumb password rule is from Moose Mobile.
Moose mobile is an Australian mobile service provider that imposes poor password requirements.
"The password must be of minimum 4 and maximum 15 characters. The Confirm Password field may only contain alpha-numeric characters."
https://dumbpasswordrules.com/sites/moose-mobile/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from IBM.
12-63 characters
One uppercase character
One lowercase character
One number
Sufficiently Strong
Special characters are optional.
Double byte characters are not allowed
https://dumbpasswordrules.com/sites/ibm/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from La Banque Postale.
Password must be 6 digits and entered on custom pad.
https://dumbpasswordrules.com/sites/la-banque-postale/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from WellStar MyChart.
Your password must be between 8 and 20 characters.
https://dumbpasswordrules.com/sites/wellstar-mychart/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Saturn.
Passwords need to be between 8 and 15 characters.
https://dumbpasswordrules.com/sites/saturn/
#password #passwords #infosec #cybersecurity #dumbpasswordrules

Here’s something that will blow your mind. Most U.S. water systems have internet-based logic controllers. And a large number of them use NO PASSWORDS OR DEFAULT PASSWORDS.
Yeah. Public water systems ready for the hacking. Which came to light because there are signs of attacks. Enough of them that CISA had to issue a warning to all water facilities, recommending they disconnect them or actually use a fucking password.
CNN cites about 30 water systems were attacked this week, with six other states having reported related cyber incidents. A security expert in the water sector said “the scale and coordination of the recent cyberattacks targeting Minnesota water suppliers is unprecedented.”
https://www.cnn.com/2026/07/31/politics/sweeping-cyberattack-us-water-systems
#Water #Utilities #Hackers #WaterSystems #WaterFacilities #InfoSec #Passwords
This dumb password rule is from Minnesota Unemployment Insurance.
Locked to *exactly* 6 chars, alphanumeric only, not special chars.
https://dumbpasswordrules.com/sites/minnesota-unemployment-insurance/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Moose Mobile.
Moose mobile is an Australian mobile service provider that imposes poor password requirements.
"The password must be of minimum 4 and maximum 15 characters. The Confirm Password field may only contain alpha-numeric characters."
https://dumbpasswordrules.com/sites/moose-mobile/
#password #passwords #infosec #cybersecurity #dumbpasswordrules

Following the cyberattacks on water & wastewater (WWS) in the U.S. over the last week, we looked at exposure of Rockwell, Siemens, and Schneider Electric devices, as those are vendors explicitly named in CISA’s updated advisory on this activity (https://www.cisa.gov/news-events/cybersecurity-advisories/aa26-097a).
Rockwell exposures have declined about 21% since we last looked at this in April, primarily driven by a drop in U.S. exposures.
While this is encouraging, I want to note this line from CISA’s most recent alert:
> Threat actors targeting exposed PLCs have modified passwords to lock out operators and disconnected the PLCs by changing their IP addresses.
I’ll also note this from an FBI alert about the activity:
> At least one organization reported modified PLC project files after noticing ladder logic discrepancies across several sites. Additionally, across several victims, similarities in network setup provided by third parties may provide MCA the opportunity to multiply successes when vulnerable network and hardware setups exist across customers.
I’m going out on a limb to say this is not the same flavor of hacktivist activity we have seen around WWS in the recent past. This feels distinctly different and potentially more harmful.
More details on the exposures:
https://censys.com/blog/cisa-alert-water-tower-plc-targeting/
New from me: analysis of a June #Cl0p extortion campaign. In a departure from their previous targeting, the data stolen in this campaign may be a bit different than what they've taken in the past. The campaign targeted PTC's Windchill and FlexPLM products, product lifecycle management tools used in manufacturing and industrial engineering.
Rather than financial, HR, or customer data, the compromised data in this case may include things like supply chain details, product designs and schematics, and other intellectual property. This is particularly notable given the adoption of Windchill across the energy, electronics, medical device tech, and defense sectors.
This dumb password rule is from Ticketmaster.de.
Your password length is limited between 8 and 32 characters.
https://dumbpasswordrules.com/sites/ticketmaster-de/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from GoDaddy.
Some characters are **too** special.
https://dumbpasswordrules.com/sites/godaddy/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
Last night I "discovered" a vulnerability in a very widely used open-source tool. The tool is nearly 40 years old, and the vulnerability is at least 28 years old.
Interestingly, Apple has a fix included that dates it back to 2008, but it appears for whatever reason the fix never made it to upstream.
Result? Everyone else is vulnerable today. I am not pointing fingers here, but clearly something went wrong.
I've now reported the issue upstream, which will hopefully eventually lead to a fix being distributed to every affected platform.
I am not going to disclose the details of the vulnerability right now, even though the fix has been public for a very, very long time now. As far as I can tell, most Linux and BSD systems are vulnerable right now, so letting coordinated disclosure happen only makes sense.
This dumb password rule is from Hetzner.
- 8 or more characters
- At least one uppercase and one lowercase letter
- At least one number or special character
Okay, fair enough, but after putting in a password with some special characters this message appears:
- Invalid characters, allowed are: A-Z a-z 0-9 ä ö ü ß Ä Ö Ü ^ ! $ % / ( ) = ?...
https://dumbpasswordrules.com/sites/hetzner/
#password #passwords #infosec #cybersecurity #dumbpasswordrules


 🍵
 [
This dumb password rule is from Crunchyroll.
At least 6 characters.
No spaces allowed.
There is no password complexity required (no special characters, numbers, uppercase or lowercase letters required).
You could make the password 123456. It also lets you change your password to your previously used password.
https://dumbpasswordrules.com/sites/crunchyroll/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from PCPartPicker.
There are no rules for passwords. Passwords can be any length (including one character)
of any complexity. No password change confirmation emails are sent.
https://dumbpasswordrules.com/sites/pcpartpicker/
#password #passwords #infosec #cybersecurity #dumbpasswordrules

This was posted yesterday.
Socket: Distributed npm Package Cluster Delivers Cross-Platform RAT Targeting Alibaba Developers https://socket.dev/blog/npm-rat-targets-alibaba @SocketSecurity #infosec #npm #JavaScript
This dumb password rule is from CenturyLink.
So many bad ideas: a low maximum length, requiring six specific character types while not accepting common symbols,
plus a weird restriction that makes random generation harder.
https://dumbpasswordrules.com/sites/centurylink/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Targobank.
Your password must:
- must not be your username
- must at least eight characters
- must contain at least one number character
- must contain at least one uppercase character and 1 lowercase character
- must not contain spaces
- must not contain three identical characters in a row
- must not conta...
https://dumbpasswordrules.com/sites/targobank/
#password #passwords #infosec #cybersecurity #dumbpasswordrules

Plexfiltration Update: One of the companies I've written to about their use of deleteduser.com (and internaluser.com actually, they are a two-fer) in email notifications, appears to be some sort of managed service desk who provide IT support for lots of smaller businesses
They continually email me support tickets, many of which contain screenshots (see attached) of the systems being worked on - to include creds and things. (There are no creds or otherwise identifying info in the example below).
I have had no response from this company and the tickets continue to flow in.

Alt...
Screenshot of someone troubleshooting a Microsoft SQL Server
This dumb password rule is from Credit Union Australia (CUA) Health.
Password must be between 7 and 10 characters, contain both an uppercase and a lowercase letter and have at least one number.
https://dumbpasswordrules.com/sites/credit-union-australia-cua-health/
#password #passwords #infosec #cybersecurity #dumbpasswordrules

Uhm, I got that strange email from Stripe this morning. One of the API keys has been leaked. That API key was used in n8n and then later in Zapier.
Either way, good job on Stripe detecting this and I highly recommend checking your Zapier and n8n integrations. Something is off here.
This dumb password rule is from Really Useful Storage Boxes.
- Have a length between 8 and 20 alphanumeric characters (without accents)
- Contain at least 1 CAPITAL letter
- Contain at least 1 lowercase letter
- Contain at least 1 numeric character
- Contain at least 1 special character taken from the following list: *$@&()[]{}=#.-!?+/£€%
https://dumbpasswordrules.com/sites/really-useful-storage-boxes/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
A QUESTION TO #INFOSEC TOOTERS
had a friend call me about suspicious emails from their bank. they didn't respond but checked their accounts with the bank’s app. they saw transactions they didn't do but that were marked as done thru the app.
they wanted to know what to do. i told them:
1. call whichever fraud/stolen bank card number they found on the website immediately.
2. freeze the app but don’t uninstall yet
3. go to the bank immediately monday
they did so and called with updates… 🧵
This dumb password rule is from Combank Digital.
Only a staggering 8-12 characters allowed with prescribed selection of special characters.
https://dumbpasswordrules.com/sites/combank-digital/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Twilio.
Restriction in inclusion of characters such as 'Twilio' in password. Password must be 16 or more characters & Can't include 3 or more consecutive repeated characters.
https://dumbpasswordrules.com/sites/twilio/
#password #passwords #infosec #cybersecurity #dumbpasswordrules

A full an exhaustive #infosec analysis (including the updated version) of the #Whitehouse app is here:
https://www.atomic.computer/blog/white-house-app-security-analysis/
As a counterpoint, this security firm says "nothing to see here... because everything is shitty in mobile world"
https://www.nowsecure.com/blog/2026/03/31/an-experts-perspective-on-the-white-house-app-putting-security-findings-in-context/
I am going with the 1st source, as it still has major designed-in anti-privacy/malware features.
This dumb password rule is from University of Western Australia (Pheme).
Passwords:
1. Must contain at least 8 characters;
2. Must contain at least 3 out of 4 types of characters
(uppercase letters, lowercase letters, digits, special characters);
and
3. Must not contain
"the user's account name or parts of the user's full name
that exceed two consecutive characters".
...
https://dumbpasswordrules.com/sites/university-of-western-australia-pheme/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Air France.
- Between 8 to 12 characters
- Should contain capital, lowercase letters and numbers
https://dumbpasswordrules.com/sites/air-france/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from CAF (French Family Allowance Fund).
You have to enter your 8-digit password using this Frenchy keypad.
https://dumbpasswordrules.com/sites/caf-french-family-allowance-fund/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from NASA Earth Data.
Username must:
- Be a Minimum of 4 characters
- Be a Maximum of 30 characters
- Use letters, numbers, periods, and underscores
- Not contain any blank spaces
- Not begin, end or contain two consecutive special characters(._)
Password must contain:
- Minimum of 8 characters
- One Uppercase letter...
https://dumbpasswordrules.com/sites/nasa-earth-data/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
Plexfiltration update: the AI work zone compliance tool has started emailing me thousands of pictures from a (I think) Saudi industrial facility again, to my internaluser.com domain. #infosec
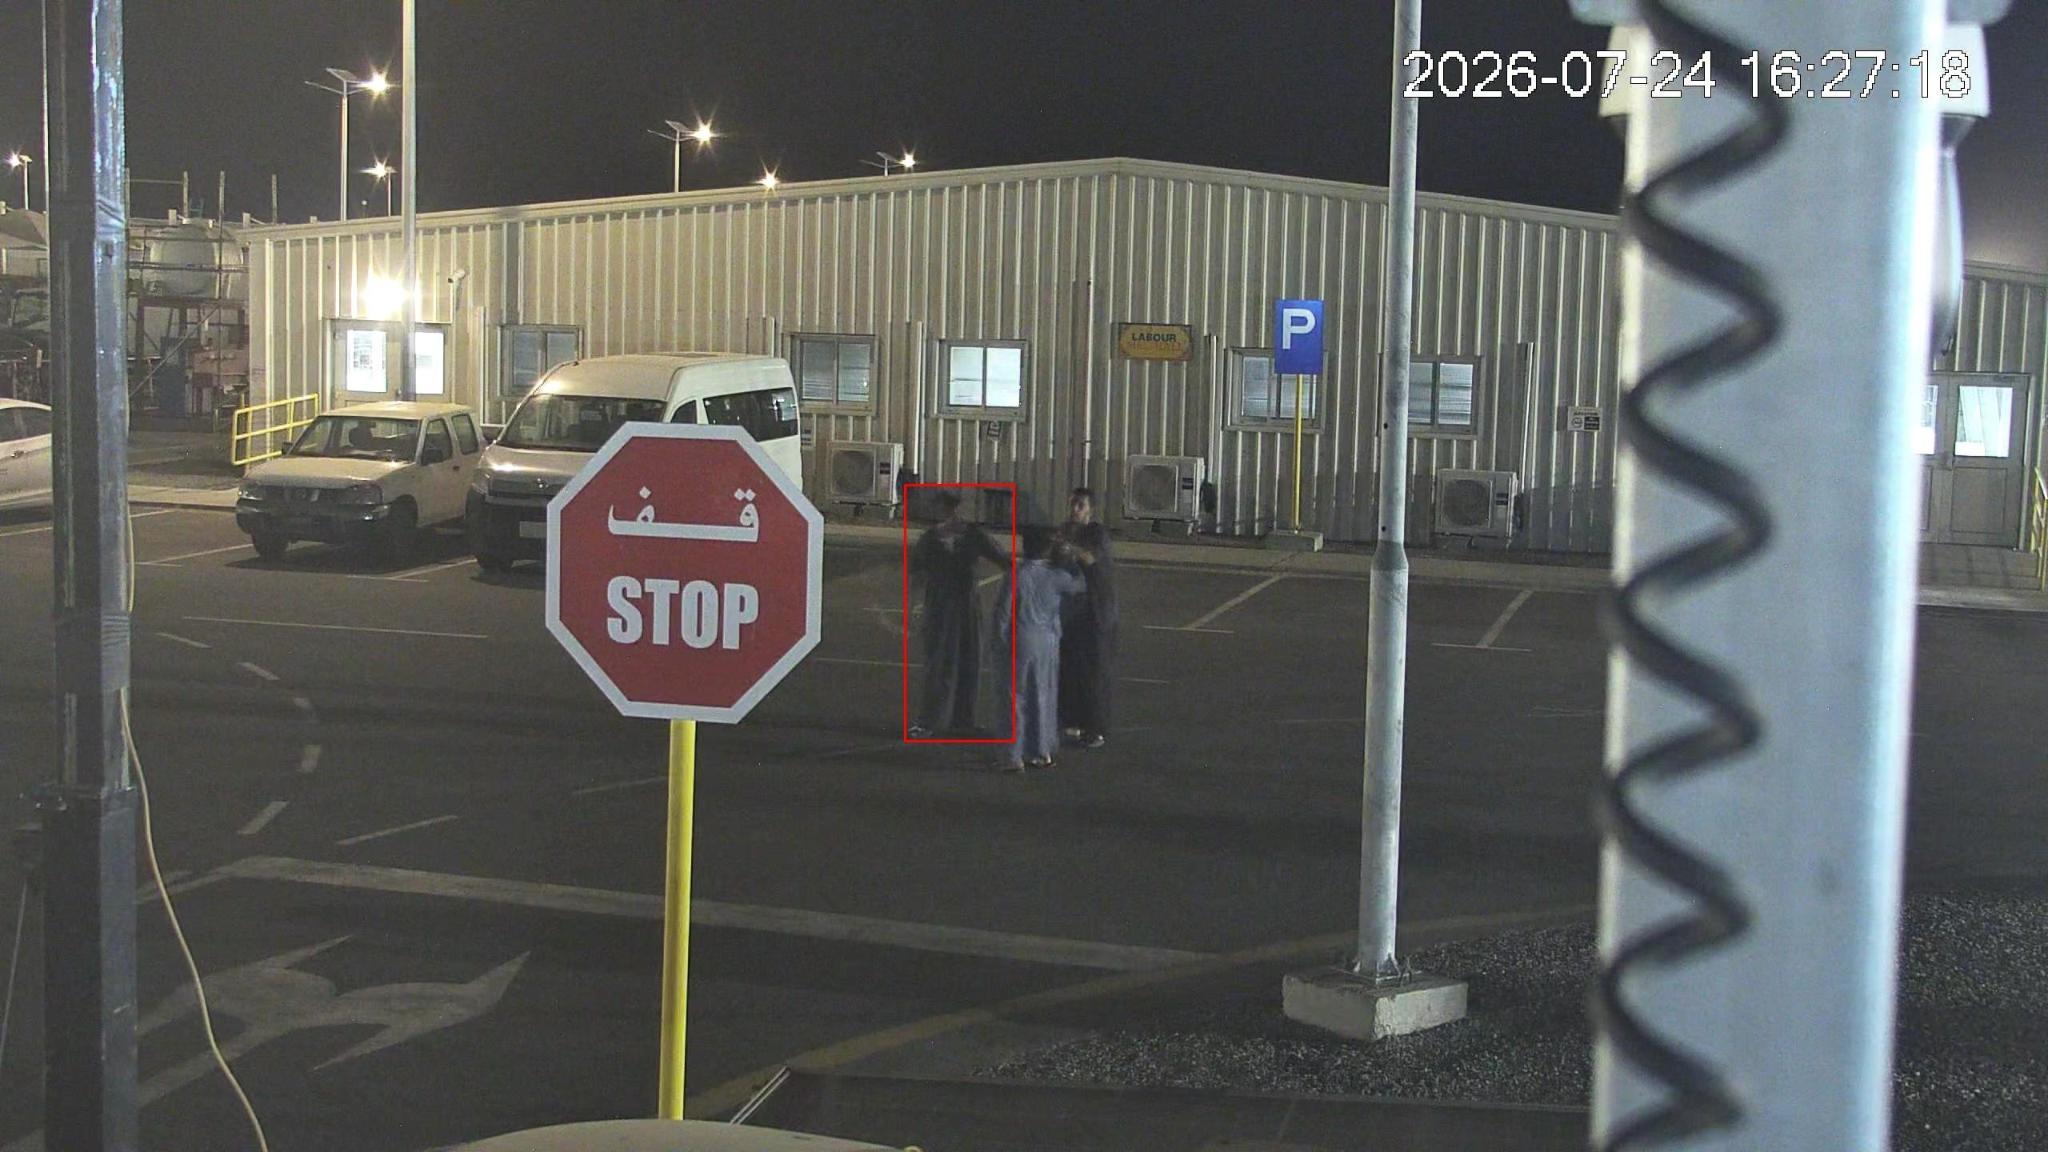
Alt...
some security camera still showing a group of people in a parking lot in front of a stop sign
Well that sure is going to be a "fun time" for the next couple of weeks/months for a lot of people…
"Immediate kernel patching and a full reboot are the only reliable mitigations."
https://www.bleepingcomputer.com/news/linux/new-refluxfs-linux-flaw-lets-attackers-gain-root-privileges/
Is that Host Unknown and their smash hit "I accepted the risk" I'm starting to hear playing in the distance? 🙃
#infosec
This dumb password rule is from Sephora.
Password must be between 6 and 12 characters. No other rules
specified.
https://dumbpasswordrules.com/sites/sephora/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
Socket published this yesterday, if you missed it:
Socket: Large-Scale GitHub Actions Abuse Powers a Distributed cPanel and WHM Exploitation Campaign https://socket.dev/blog/github-actions-abuse-powers-cpanel-and-whm-exploitation @SocketSecurity #infosec #threatresearch #GitHub
This dumb password rule is from KPMG Talent Community.
While stating otherwise, the site actually *accepts a backslash* in the password
and displays a forward slash as the example of the disallowed backslash
Password:
- Must be at least 8 characters long
- Must contain at least 1 number
- Must contain at least 1 letter
- Must contain at least 1 spec...
https://dumbpasswordrules.com/sites/kpmg-talent-community/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
Hot take:
I hate how all these articles talk about how OpenAI’s clanker “broke out” and attacked Hugging Face.
No, OpenAI’s dog slipped its chain because they don’t know what the hell they’re doing, and it bit another dog.
#AI #SlopPocalypse #FuckAI #Infosec #cybersecurity
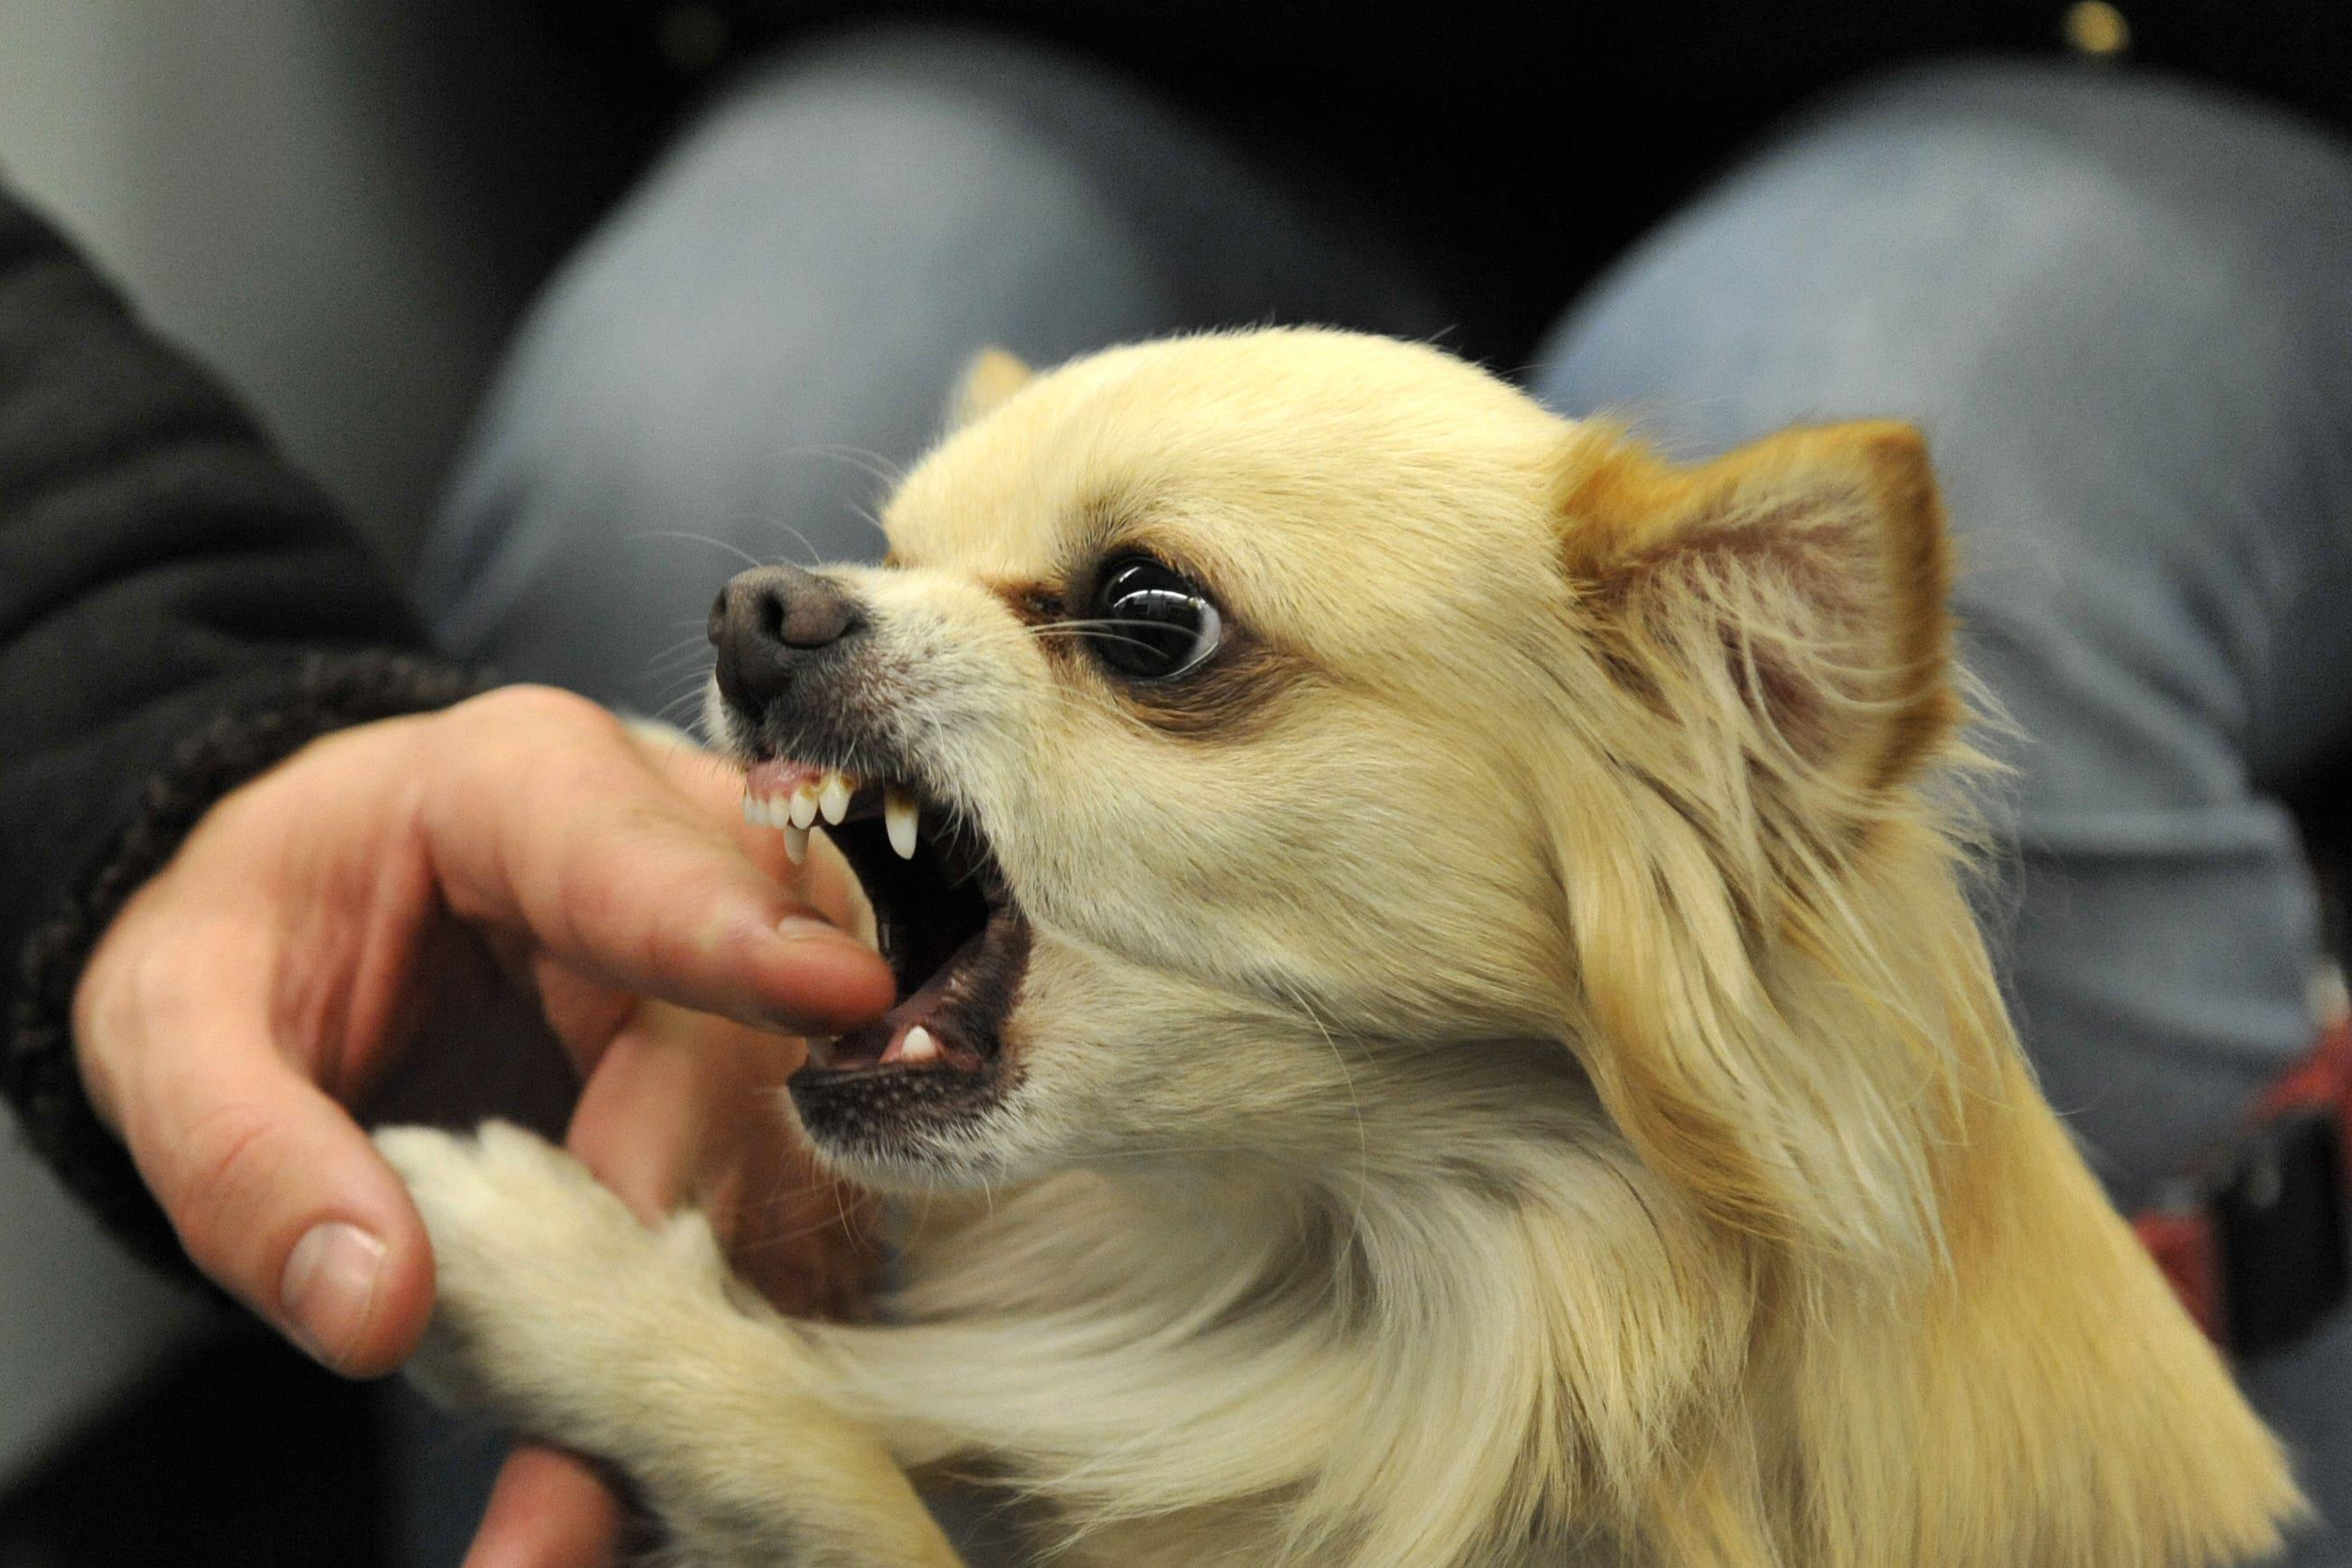
Alt...
Little dog biting a person’s finger
This dumb password rule is from Dutch Tax Authorities (Belastingdienst).
At least 8 and at most 25 characters, of which at least 3 of the characters were not used in the previous password.
No more than 3 of the same characters.
At least 1 upper case and 4 lower case characters.
No more than 3 special characters.
It's not like hashing passwords is a thing or something.
https://dumbpasswordrules.com/sites/dutch-tax-authorities-belastingdienst/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
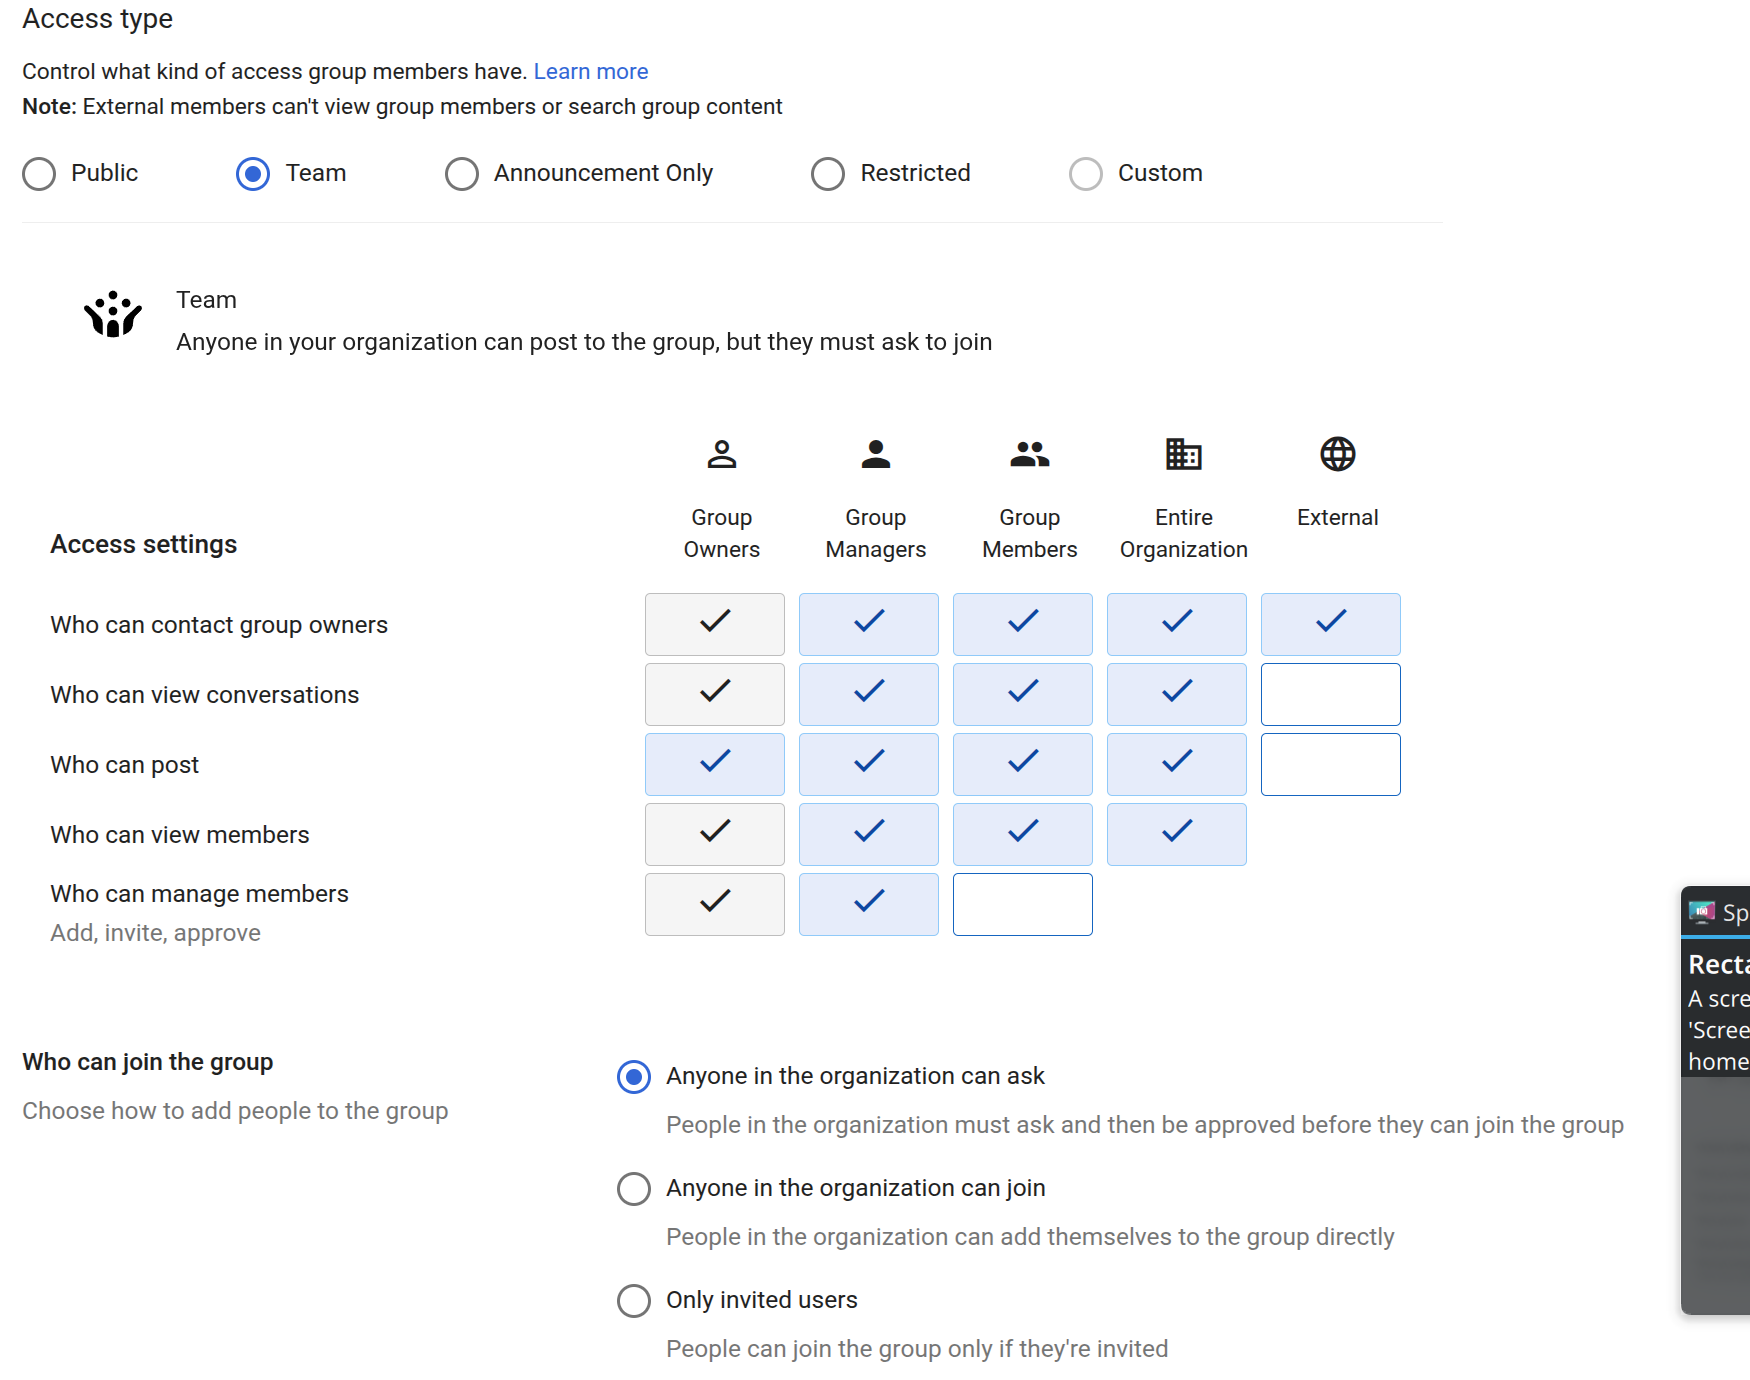
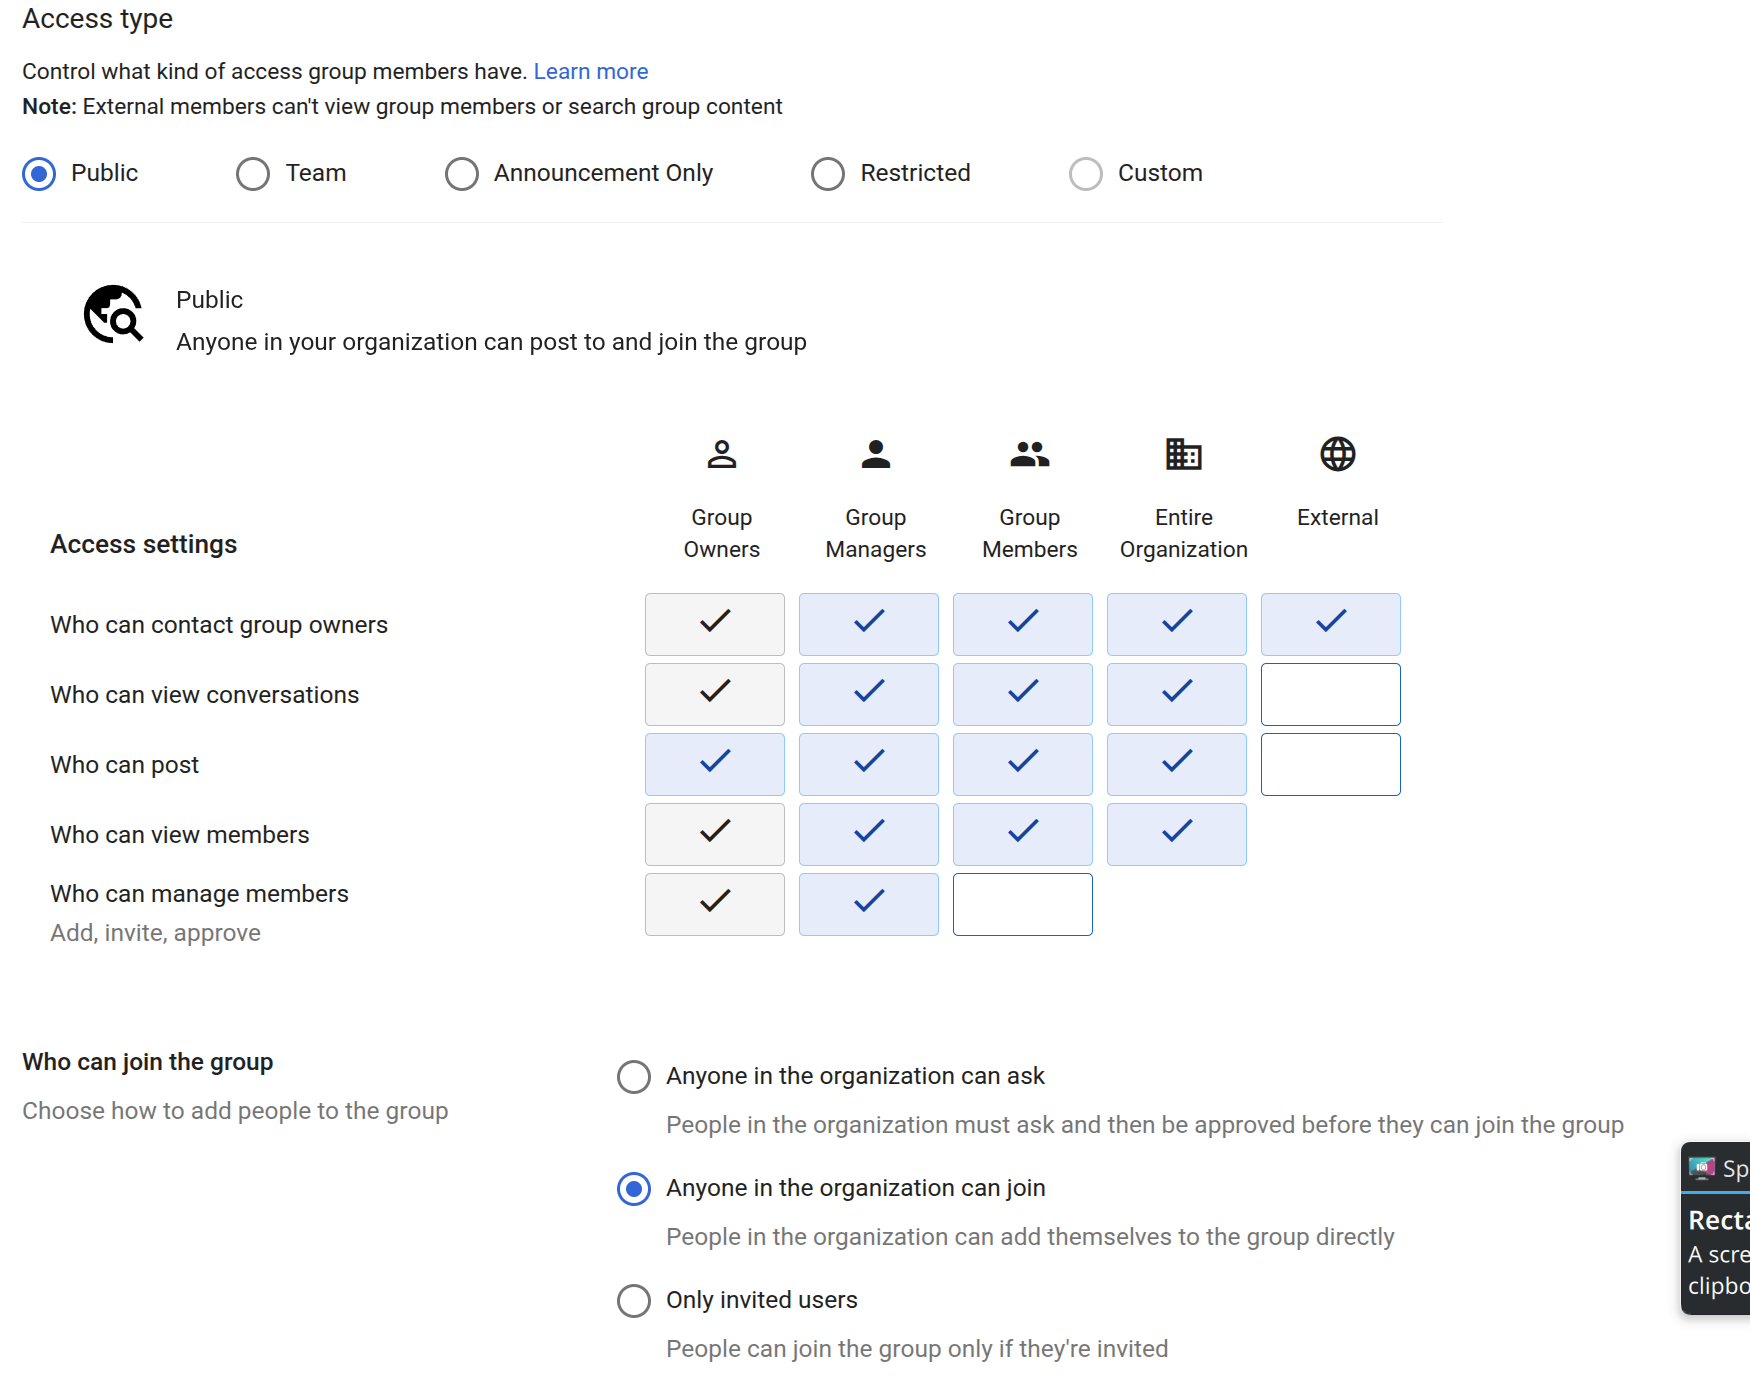
I've had admin powers at 5+ companies' Google Workspace/G Suite over the past decade or so. Every single one had groups which were misconfigured, often so anyone in the whole company could join without approval or see the message history at https://groups.google.com without being a member at all.
This is because for any sensible configuration of Google Groups when using it for email groups you have to use the "Custom" permissions mode. The default Public mode doesn't allow external people to email the group, but does allow the whole company to see all the messages. The default Team mode, has the same problem of everyone being able to see all the messages.
Also let's not forget that dangerous little "Anyone in the organisation can join" toggle at the bottom which is on by default. So any random new starter can join your confidential company directors group and get all the emails sent to it.
Giving Google the benefit of the doubt here, I think the reasoning might be that Google Groups is intended as a kind of company forum, not for private email groups. However that isn't how anyone uses it in my experience...
#security #infosec #google #googleworkspace
Alt...
Screenshot of the default Google Group settings for team mode
Alt...
Screenshot of the default Google Group settings for public mode