Search results for tag #infosec

This dumb password rule is from Kryterion Webassessor.
I was quite surprised to see this when I was registering for my Google Professional Cloud **Security** Engineer certification. Nice part is that they **don't allow quotes** as special character, so I assume there possibly might be some other issues on their backends. :-)
https://dumbpasswordrules.com/sites/kryterion-webassessor/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
OpenAI is hiring #infosec folks. Don't work for OpenAI regardless of how much money they will throw at you.
This dumb password rule is from USAA Bank.
Password cannot be longer than 12 characters but they don't tell you that until after you try a new password. To make up for this fact they've added dubious additional security features on top of this weak foundation.
https://dumbpasswordrules.com/sites/usaa-bank/
#password #passwords #infosec #cybersecurity #dumbpasswordrules

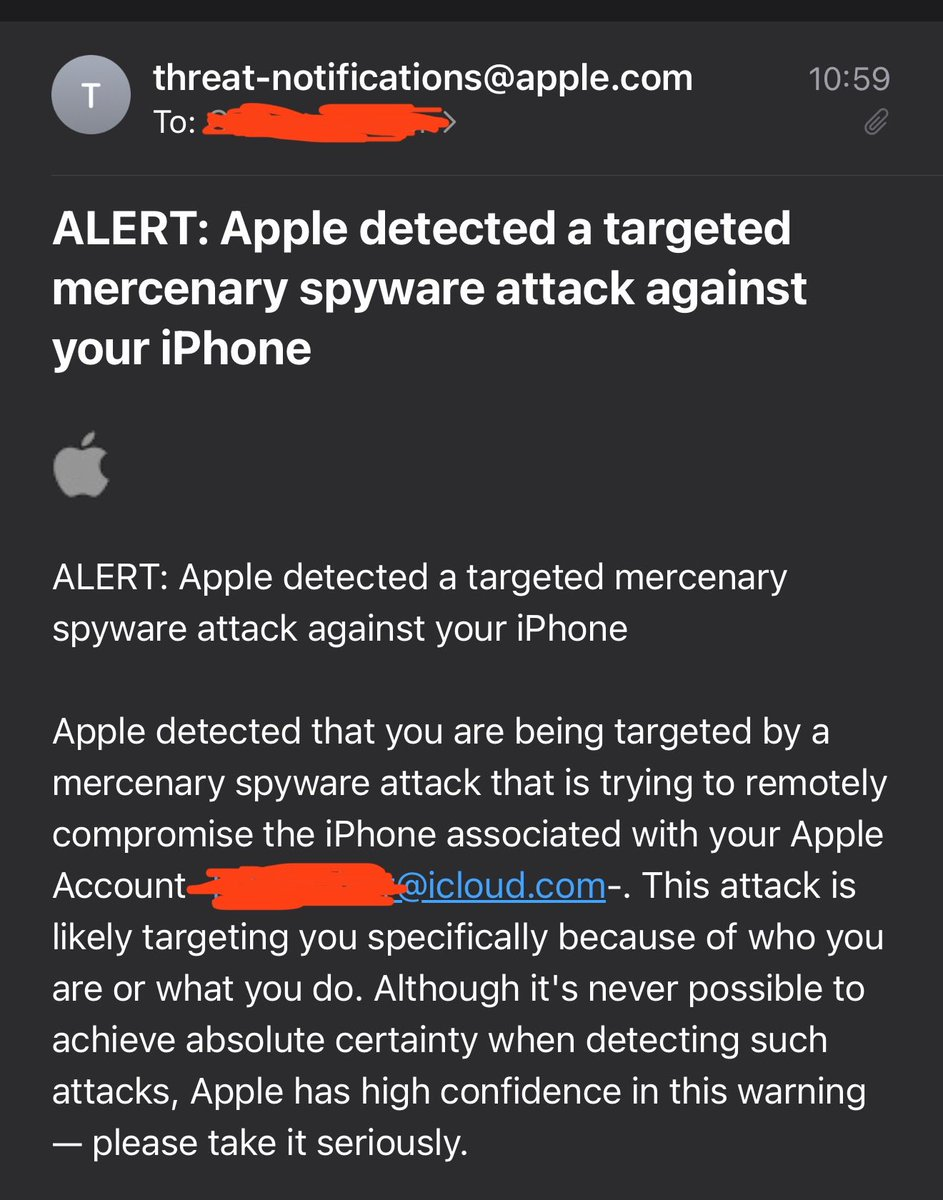
@briankrebs Have you ever gotten this notification 🔔 📳 😨  🤦🏼 😱 #infosec
Alt...
- threat-notifications@apple.com 10:59
To: tial
ALERT: Apple detected a targeted
mercenary spyware attack against
your iPhone
#
ALERT: Apple detected a targeted mercenary
spyware attack against your iPhone
Apple detected that you are being targeted by a
mercenary spyware attack that is trying to remotely
compromise the iPhone associated with your Apple
Account icloud.com-. This attack is
likely targeting you specifically because of who you
are or what you do. Although it's never possible to
achieve absolute certainty when detecting such
attacks, Apple has high confidence in this warning
— please take it seriously.
This dumb password rule is from Credit Union Australia (CUA) Health.
Password must be between 7 and 10 characters, contain both an uppercase and a lowercase letter and have at least one number.
https://dumbpasswordrules.com/sites/credit-union-australia-cua-health/
#password #passwords #infosec #cybersecurity #dumbpasswordrules


long post, asking for volunteer development help [SENSITIVE CONTENT]
So, I think I might make this more formal via email and announcement, but this has been taking up a large chunk of mental space. I desperately need help in developing HardenedBSD. While I'm so grateful for the many kind and encouraging words, there's still so many hours in a day.
I'm also very grateful we have one person who recently has stepped up, helping move the Pledge port ahead (and closer to full API compat.)
Please consider this post as unofficial. This is just "my thoughts as I've experienced them the past few days." If something comes from publicly posting my thoughts, all the better.
I'm wondering if anyone knows any folks interested in the kinds things we do at HardenedBSD. specifically looking for folks to mentor to do either osdev on hbsd itself, or in developing the censorship- and surveillance-resistent mesh network proof-of-concept.
i could budget a small amount for acquiring HaLow mesh gear. i don't have the budget for a laptop or other equipment. the only requirement is that all this R&D work be done on HardenedBSD.
When it comes to hardware acquisition, it's hard to know who to trust. I would like to make sure donated funds used properly and don't want to be scammed.
On the osdev side, I would like an implementation of random fd assignment. open(2) and friends usually just use the first available number, increasing until maxfd limit is hit.
i would like to change it to be less predictable, to a random search mode rather than incremental search.
This would help mitigate file descriptor reuse bugs.
Of course, we would collaborate via #Radicle for any development work.
One last thing: I should be explicit in that all this is unpaid volunteer work. I have never received payment for my work and don't intend to.
I understand that a large portion of volunteer work fizzles out or doesn't work out. That's fine. I would just expect return to the HardenedBSD Foundation of any procured hardware.
This dumb password rule is from Australia Immi Platform.
The Australian immigration platform requires at least 14 characters and at least one from three of the four groups: lowercase letters, uppercase letters, digits, and special characters.
The random generator in my password manager only needed one second attempt to avoid 'dangerous' special charact...
https://dumbpasswordrules.com/sites/australia-immi-platform/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from SecureAccess Washington.
Central authentication for all Washington State services
(DoL, ESD, etc).
Password must have *exactly* 10 characters, but form happily
lets you enter more and only throws errors after submit,
providing no useful feedback.
https://dumbpasswordrules.com/sites/secureaccess-washington/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Copart.
Copart: "The security of our members is extremely important to us."
Also Copart: "We're gonna need you to keep your password between 5-10 characters."
https://dumbpasswordrules.com/sites/copart/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from O2 Spain.
When registering in *Mi O2* app, password length must be exactly 7 or 8 characters (numbers and letters only).
As O2 is part of Telefónica (Movistar), it seems to use the same backend (at least in Spain), so it has the [`same password requirements`](https://dumbpasswordrules.com/sites/movistar/).
https://dumbpasswordrules.com/sites/o2-spain/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
Alt...
1 2 |
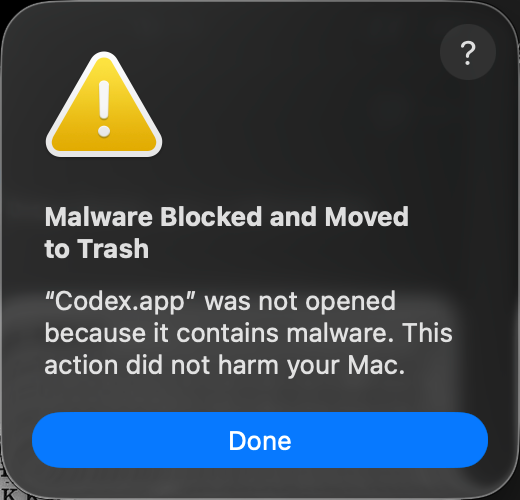
Malware Blocked and Moved
to Trash
“Codex.app” was not opened
because it contains malware. This
action did not harm your Mac.
CO eee
Ee
This dumb password rule is from Gigabyte RMA system.
Your password must contain:
Between 8-12 characters
An upper case letter (A, B, C, etc.)
a lower case letter (a, b, c, etc.)
A number (1, 2, 3, etc.)
A symbol (-, ~, !, #, $, %, &, (, ), +, =, .)
https://dumbpasswordrules.com/sites/gigabyte-rma-system/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
 MissConstrue [She/Her (Crone Extraordinaire)] » 🌐
@MissConstrue@mefi.social
So...this is bad. #47 just signed an executive order allowing American private companies to carry out #hacking operations against foreign criminal groups.
They lay out a bunch of "restrictions" and a whole million dollar escrow to get in the program. A million! Elon might have to look in his cupholder for some change.
It's an insane idea. First, threat actors use innocent architecture, the odds of a misfire are massive. Second, hack-backs are are good way to get arrested in another country, or have international warrants issued, even if Diaper Daddy says you can. Third, I'm pretty sure Marques & Reprisals is a Congressional privilege.
Like, I see how this might seem like a good idea to someone who is 80 years old, and takes advice from the Secretary of Scotch and an Abandoned Victorian Doll, but else....not so much.
Gold plated nonsense from Dear Leader: https://www.whitehouse.gov/presidential-actions/2026/08/expanding-capabilities-to-combat-transnational-cyber-enabled-crime/
This dumb password rule is from NVV (Nordhessische VerkehrsVerbund).
Password length must be 4 to 10 characters with only a few special characters allowed.
https://dumbpasswordrules.com/sites/nvv-nordhessische-verkehrsverbund/
#password #passwords #infosec #cybersecurity #dumbpasswordrules


Hey gang, we need to talk about the recent presidential memorandum authorizing offensive security operations by the private sector. That's because I care about your safety, the rule of law, and a functioning internet. A lot of folks might be excited about the opportunity to use their hacking skills to take out bad actors and criminals in a way that's safe and legal for them. That's not what this is.
At best, this memo provides you with some limited protection from prosecution by the federal government for what's otherwise criminal activity. That protection is only provided if you follow their rules. And it's only as good as Trump's promises, only as long as he perceives you to be useful to him personally, and possibly only as long as Trump retains power.
It provides you with no protection against prosecution by other jurisdictions. You are not a government actor or a uniformed soldier, so you will have no protections from prosecution under sovereign immunity or as a lawful combatant.
Every one of these actions is likely to be considered a criminal offense in every jurisdiction that your operations impact. That includes direct operations as well as support (e.g., offsec tool building, standing up infrastructure for malware delivery or C2). It includes the jurisdictions that your targets are in, as well as every jurisdiction that your operations travel through and that host your infrastructure. It includes upstream and downstream actions by other operators that you might not be fully aware of, if they can tie you to a criminal conspiracy.
Your identity and your operations will not remain secret. This administration has shown they cannot and will not keep secrets. Our president was charged with criminal violations of the espionage act, and his drunkard of a SECDEF has notoriously leaked classified details of military operations to a reporter, so we know they're not trustworthy with secrets.
We've shown that governments can identify and charge cyberespionage operators since the APT1 indictments in 2014, and in some cases we've even successfully arrested, tried, and imprisoned hackers operating for foreign governments. You should assume that other countries have similar investigative capabilities.
You will be subject to arrest, extradition, trial, and imprisonment every time you set foot abroad for business, vacation, or visiting family, possibly for the rest of your life. You could be subject to international sanctions that might freeze your finances. You'll almost certainly wind up a target for intelligence collection by foreign intelligence services. You could also be considered an unlawful combatant and legitimate target for kinetic and non-kinetic military operations by the military forces of the countries you've pissed off.
You should also consider the unreliability of the Trump regime's designations for targeting. They've routinely designated civilian or even functionally nonexistent organizations as criminal or terrorist organizations. You cannot trust their assurances that the bad guys you're harming are actually bad guys.
Please don't make a dumb decision that ruins your life, especially not for the false promises of the Trump regime.
This dumb password rule is from Afraid.org FreeDNS.
Password must be between 4 and 16 characters long
https://dumbpasswordrules.com/sites/afraid-org-freedns/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Michigan.gov.
Must use special characters, but only from this list of stuff we think is safe or whatever.
https://dumbpasswordrules.com/sites/michigan-gov/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
Storing private key material in dumpable mappings: security vulnerability? What say ye? Yay or nay?
| Aye: | 2 |
| Nodiddly: | 0 |
This dumb password rule is from amaysim.
Passwords must be 6-15 characters. If you enter more than 15 characters at signup, there is no error,
but the system apparently silently truncates to 15 characters. So of course, logging in subsequently
fails if you enter the untruncated password. How convenient.
https://dumbpasswordrules.com/sites/amaysim/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Benergy4.
12 to 25 characters, only these special chars allowed: @+/'!#$^?:,.(){}[]~-.
Also, security questions.
https://dumbpasswordrules.com/sites/benergy4/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
Alt...
< From delta community on Reddit
10:53 7 wll FE
fool -
Pilot Messages « 1001ve
Live cockpit ACARS, intercepted
Q DAL591 [x
N6705Y REICH
ACARS history is limited to the last 24 hours
DLO517 DL2990 DL0918 DLO7
© 2 messages
o System 16:512
"091630 KLAS KATL6
A
NO INFO AS OF NOW
WE HAVE A BUNCH OF PAX
THAT WERE AT A CYBER
CONFRENCE IN LAS THE
WERE ABLE TO JAM OUR
WIFI AND BRODCAST THERE
SIGNIAL"
o Crew 16:34
"091630 KLAS KATL6
A
HEY ALERT CORP SECL
WE HAVE A PAX ON TH. 4 tryflightdeck.com
HAS CREATED A SCAM Wir
CALLED DELTA WIFI FAST
WE BELIEVE THEY ARE
TRYING TO SCAM THE OTH
PAX"
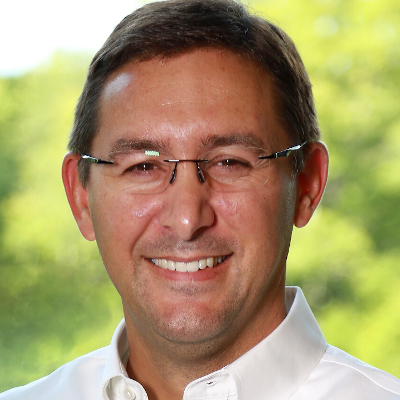
I work in #infosec and consider myself pretty well educated on what’s happening with #AI.
But I’m about 33% of the way through @emilymbender and Alex Hanna’s book, “The AI Con”, and I’ve really learned a lot more.
If you’re skeptical or curious about AI, this is a must-read. I’m recommending it to everyone I know.
“The AI Con: How to Fight Big Tech's Hype and Create the Future We Want”, by Emily M. Bender and Alex Hanna
Edit: Added text in this post with the title and authors. It's also in the image's ALT text. Sorry!
#books #bookstodon #reading #AI #technology #nonfiction

Alt...
“The AI Con: How to Fight Big Tech's Hype and Create the Future We Want”, by Emily M. Bender and Alex Hanna
This dumb password rule is from Targobank.
Your password must:
- must not be your username
- must at least eight characters
- must contain at least one number character
- must contain at least one uppercase character and 1 lowercase character
- must not contain spaces
- must not contain three identical characters in a row
- must not conta...
https://dumbpasswordrules.com/sites/targobank/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from El Corte Ingles.
Min 6 and max 8 characters for password! Can't contain anything
different than letters and numbers. Apart, the email address must have
at least 8 characters (sorry million dollar domain owners! :D)
https://dumbpasswordrules.com/sites/el-corte-ingles/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
 boosted
Wer seinen eigenen Mailserver betreibt, kennt das Problem
Secure Your Server: acht Checks, ein Scan, für immer kostenlos
Ich betreibe neben vielen privaten Domains auch meinen eigenen Mailserver, da hängt viel an einer sauber konfigurierten Domain: DNS-Einträge exakt, TLS sauber, SSH gehärtet. Wer das prüfen will, trifft auf ein Dutzend Scanner, die fast alle dasselbe tun: sich einen einzigen Ausschnitt anschauen und ab einem gewissen Punkt ein Konto oder eine Kreditkarte verlangen. Deshalb gibt es jetzt Secure Your Server: acht Kategorien von DNS bis PGP in einem einzigen Scan, dazu ein echter Mail-Zustellungstest, für immer kostenlos, ohne Konto, ohne Tracking. Teste deine eigene Domain, bevor es jemand mit weniger guten Absichten tut.
#chrislo #digitaleunabhängigkeit #itsicherheit #cybersecurity #infosec #opensource #selfhosting #datenschutz #dsgvo #digitalesouveränität #security #vereine

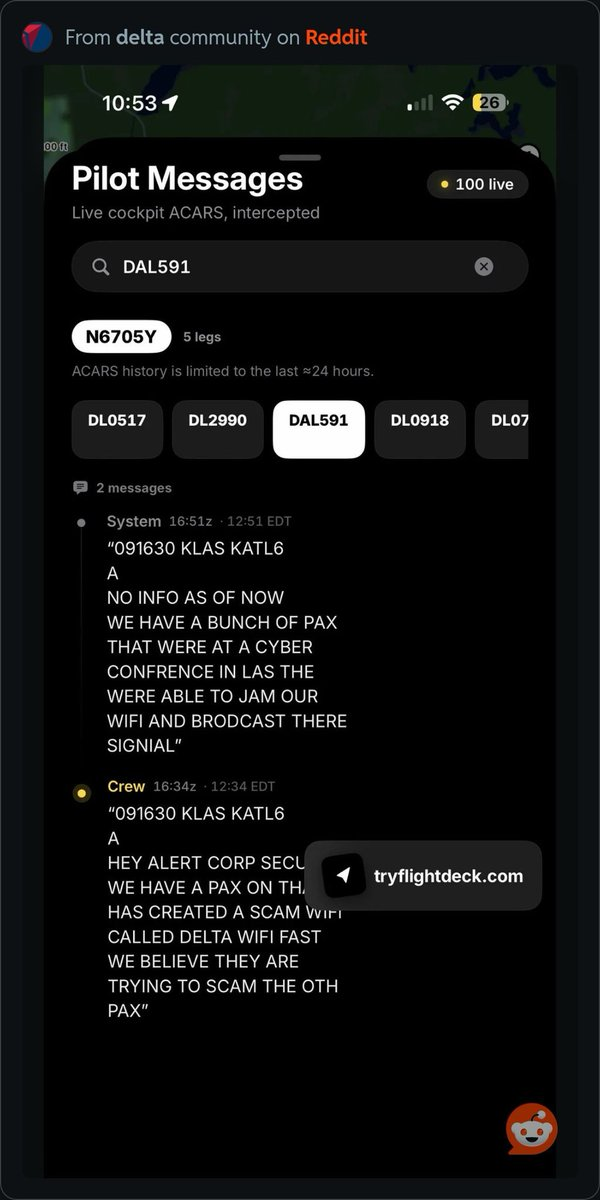
RE: https://live.acarsdrama.com/@acarsdrama/117072256729860162
WHAT DID YOU ALL DO?!?!?!
Dan MacLeodboosted
Air to Ground Message:
NO INFO AS OF NOW WE HAVE A BUNCH OF PAX THAT WERE AT A CYBER CONFRENCE IN LAS THEY WERE ABLE TO JAM OUR WIFI AND BROADCAST THEIR SIGNAL
Area: Liberal, KS, USA
Type: Boeing 757-200
A: #aadee4f6c99
F: #fdcd8d51430

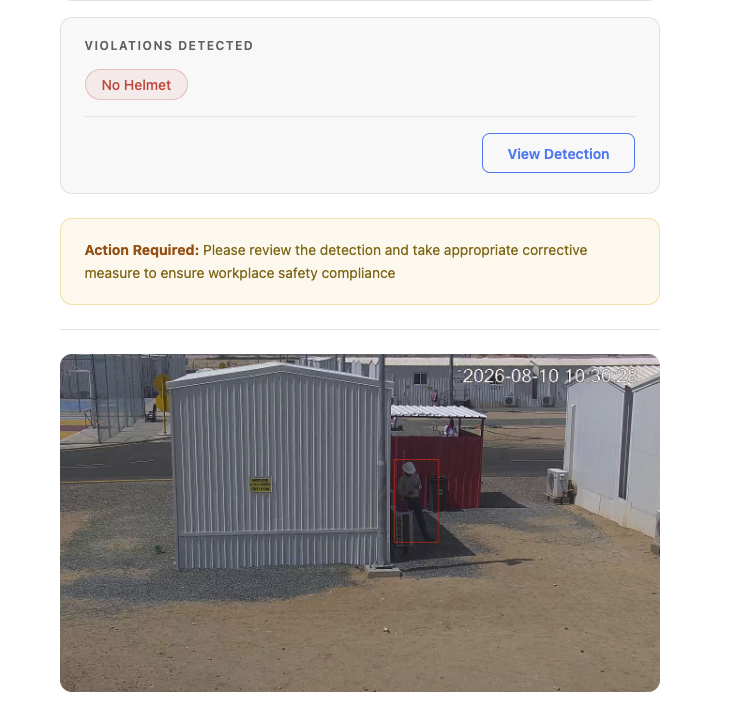
i am once again being informed about 100's of workplace violations occurring at a middle eastern industrial site that are not, in fact, violations - because this fella is clearly wearing a helmet
Alt...
An email sent to me at internaluser.com that shows a worker flagged for not wearing a helmet when they are by some AI tool.
This dumb password rule is from Bendigo Bank.
**Exactly** eight characters.
https://dumbpasswordrules.com/sites/bendigo-bank/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Netflix.
[The help page](https://help.netflix.com/de/node/54078)
and the [password reset page](https://www.netflix.com/password) say:
Ihr Passwort muss zwischen 4 und 60 Zeichen lang sein und darf keine Tilde (~) enthalten.
https://dumbpasswordrules.com/sites/netflix/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from BinckBank.
Between 10 and 16 letters and/or digits. No special characters are allowed.
Must be renewed at least every 180 days, but you can configure to let the password expire sooner.
When changing the password, the new password cannot be too similar to the existing password.
https://dumbpasswordrules.com/sites/binckbank/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Techcombank.
Your password must:
- Be between 6 and 8 characters long
- Contains at least 1 number character
- Contains at least 1 lowercase character
- Contains at least 1 uppercase character
- Neither space nor unicode character is allowed. In fact,
NO special characters is allowed
- Must be changed every 9...
https://dumbpasswordrules.com/sites/techcombank/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from PayPal.
Must be between 8 and 20 characters, no spaces, uppercase and lowercase, one symbol...
The rule limits special characters to !@#$%^&*(). but my current password has a "-" in it so someone decided to restrict this further which is totally backwards. Things are meant to get better not worse!
https://dumbpasswordrules.com/sites/paypal/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
Wired covered deleteduser.com in an article about placeholder domains and the crazy emails that get sent to them:
This dumb password rule is from AOK (German Health Insurance).
This is the online customer portal of the German health insurance company AOK. They have an extensive set of rules for both passwords and usernames.
The password rules are:
- Length between 8 and 14 characters
- At least one letter, one number and one special character
- Special characters are: !...
https://dumbpasswordrules.com/sites/aok-german-health-insurance/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
FreeRadical.zone is a Mastodon server themed around infosec and privacy and technology and leftward politics and cats and dogs.
This server has been online since 2017.
You can find out more at https://freeradical.zone/about or contact the admin account @tek
#FeaturedServer #InfoSec #Privacy #Technology #Mastodon #Fediverse #FreeFediverse
This dumb password rule is from Tanishq.
Password must contain:
- 6 to 16 characters.
- At least one special character (@, #, $, %, * and & only).
- At least one alphabet.
- At least one number.
https://dumbpasswordrules.com/sites/tanishq/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from SONY.
- between 8 and 30 characters
- at least one number or special character
- not part of email address
- avoid common passwords
- repeating characters 3 or more times should be avoided
- currency characters and 3 or more consecutive characters, also in reverse order, should be avoided
Somehow "$" i...
https://dumbpasswordrules.com/sites/sony/
#password #passwords #infosec #cybersecurity #dumbpasswordrules

https://wordpress.org/documentation/wordpress-version/version-7-0-3/
Update y'all WordPress installs immediately. Multiple security issues fixed that affect both the current major branch and also older branches.
This dumb password rule is from IBM.
12-63 characters
One uppercase character
One lowercase character
One number
Sufficiently Strong
Special characters are optional.
Double byte characters are not allowed
https://dumbpasswordrules.com/sites/ibm/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
This dumb password rule is from Fidelity National Information Services.
White label online banking provider. Typically appears as `BANK.ibanking-services.com` or `BANK.ebanking-services.com`. If your small local bank has a crappy online banking experience, these guys probably provide it.
`\<>'` and spaces prohibited, upper bound. Passwords of exactly the maximum len...
https://dumbpasswordrules.com/sites/fidelity-national-information-services/
#password #passwords #infosec #cybersecurity #dumbpasswordrules

Sharing the following on behalf of a friend. Any contribution is incredibly helpful. Boosts of this post for visibility also greatly appreciated. Finally, #infosec and #dev friends, if you have any leads on jobs I would be more than happy to pass along.
> After being laid off and facing a cancer recurrence, he's now fighting to keep his home during treatment that could last several months. If you’re able, please consider donating or sharing to help him stay afloat and focus on his health—every bit makes a difference.